You can view and edit the interface-level assignments. To edit an assignment:
In the Manager, navigate to Policy → <Admin Domain Name> → Intrusion Prevention → Policy Manager.
Double-click on the row of a policy assignment. The interfaces details panel is displayed on the right side of the page.
Interfaces tab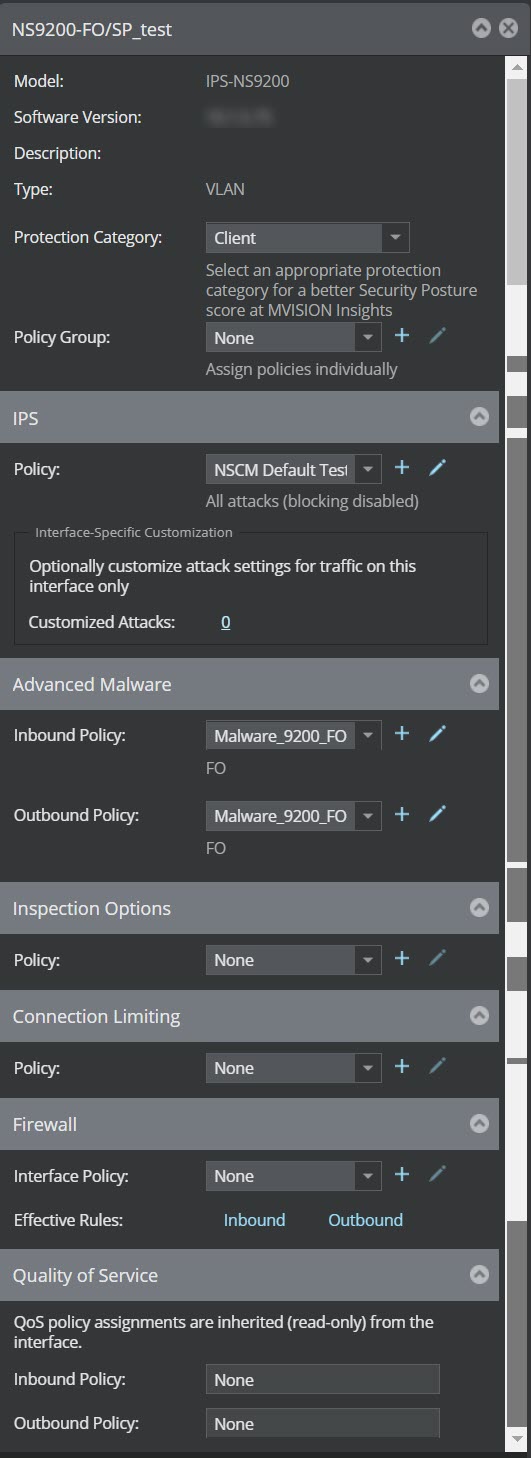
The following fields are displayed.
Option
Definition
Model
Specifies the model of the device
Software Version
Specifies the software version running on the device
Description
Displays the description of the interface assignments
Type
Specifies the type of interface
Protection Category
Select a protection category from the drop-down list for a better security posture score at the Trellix Insights. The protection category options available are:
None
Server
Client
Client & Server
Exclude
By default, the protection category is None . When the option None is selected, the telemetry data sent to Trellix Insights flags the interface for incomplete configuration.
The protection category Exclude can be selected in case you want to exclude the interface configuration from security posture scoring on Trellix Insights.
Policy Group
Select the type of policy group from the drop-down list.
Click
 to add a new policy group.
Click
 to edit or view the existing policy group details.
IPS
Select the type of IPS policy from the drop-down list.
Click
to add a new IPS policy.Click
to edit or view IPS policy details.Note
If the Policy Group option selected as None, you can manually assign the IPS policy. If the Policy Group option is already selected, you will not have the option to edit the IPS policy because these details are defined in the selected policy group.
In the Customized Attacks field, click on the hyperlink to customize the attacks. By default value is 0. The hyperlink is displayed only if the number of customized attack is more than 0.
Click
 to reset the customization to the local attack definitions. This option is not displayed if the number of customized attacks is 0.
Click
 to merge the local policy with the baseline policy. This option is not displayed if the number of customized attacks is 0.
Advanced Malware
Select the type of advanced malware policy from the drop-down list.
In the Inbound Policy field, select the inbound policy from the drop-down list. Click
to add a new advanced malware policy. Click to edit or view the advanced malware policy.In the Outbound Policy field, select the outbound policy from the drop-down list. Click
to add a new advanced malware policy. Click to edit or view the advanced malware policy.Note
If the Policy Group option selected as None, you can manually assign the advanced malware policy. If the Policy Group option is already selected, you will not have the option to edit the policy because these details are defined in the selected policy group.
Inspection Options
Select the type of Inspection Options policy from the drop-down list.
Click
to add a new Inspection Options policy.Click
to edit or view Inspection Options policy details.Note
If the Policy Group option selected as None, you can manually assign the Inspection Options policy. If the Policy Group option is already selected, you will not have the option to edit the Inspection Options policy because these details are defined in the selected policy group.
Connection Limiting
Select the type of Connection Limiting policy from the drop-down list.
Click
to add a new Connection Limiting policy.Click
to edit or view Connection Limiting policy details.Note
If the Policy Group option selected as None, you can manually assign the Connection Limiting policy. If the Policy Group option is already selected, you will not have the option to edit the Connection Limiting policy because these details are defined in the selected policy group.
Firewall
In the Interface Policy field, select the interface policy from the drop-down list. Click
to add a new interface policy. Click to edit or view the interface policy.Note
If the Policy Group option selected as None, you can manually assign the firewall policy. If the Policy Group option is already selected, you will not have the option to edit the policy because these details are defined in the selected policy group.
In the Port Policy field, select the port policy from the drop-down list. Click
to add a new port policy. Click to edit or view the port policy.Note
The Port Policy field is displayed only for interfaces and is not displayed for sub-interfaces.
To view the effective rules, in the Effective Rules field click Inbound button to view the inbound rules, or click Outbound button to view the outbound rules.
Quality of Service
In the Inbound Policy field, select the inbound policy from the drop-down list. Click
to add a new QoS policy. Click to edit or view the inbound policy.In the Outbound Policy field, select the outbound policy from the drop-down list. Click
to add a new QoS policy. Click to edit or view the outbound policy.Note
If the Policy Group option selected as None, you can manually assign the QoS policy. If the Policy Group option is already selected, you will not have the option to edit the QoS policy because these details are defined in the selected policy group.
The Interfaces tab has some useful filtering options to locate and view the policy assignments. String based filter is available for those columns where policy assignments are displayed based on the text typed in the text field of the Filters option. By typing the first few characters in the text field, the policies matching the typed characters are displayed on the page.
Note
When the policy assignments are displayed by using the Filters option, the header of column by which the policy assignments are filtered is highlighted in orange color. By clicking the Clear All Filters button, the filter is removed and all the policy assignments are displayed on the page.
Click a column header and select the option to sort based on ascending or descending order. The options are Sort Ascending and Sort Descending.The column based on which the list is sorted is indicated in the column header by an up arrow icon for ascending order and down arrow icon for descending order.
For a consolidated view of a group of policy assignments, click on the column header of the field (Example : Direction) by which it should be grouped and click Group by this field.
Note
To remove the display of policy assignments by groups, unselect the Show in groups check-box option from the column header. The Show in Groups option is enabled only if the Groups by this field option is selected.
Click Save to save the changes.
Note
You must assign an alternate policy for a Sensor's interfaces/subinterfaces in cases where the original policy needs to be deleted. For example, you have created an IPS policy called Custom1. You apply it to interfaces G1/2, G1/3, and G1/4 on a Sensor. After some time, you determine Custom1 does not work effectively, and you want to delete it. The Manager will not allow you to delete a policy that is currently enforced. You have to change the policy of each Sensor resource where the custom policy is applied before deleting the custom policy itself.