You can enable Layer 7 Data Collection per interface or sub-interface. To optimize Sensor performance, you can also specify the protocols and the fields that are to be exported.
Click the Policy tab.
From the Domain drop-down list, select the domain you want to inspect traffic.
Navigate to Intrusion Prevention → Policy Manager.
On the Interface tab, double-click the interface to enable the advanced traffic inspection.
The <Device name/Interface> panel opens.
In the Inspection Options section, select the policy from the Policy drop down list.
To create a new policy, click the
 icon or double-click on the policy to edit an already assigned policy.
The Properties page opens. Enter the Name and Description. Select the Visibility and click Next.
The Inspection Options page opens.
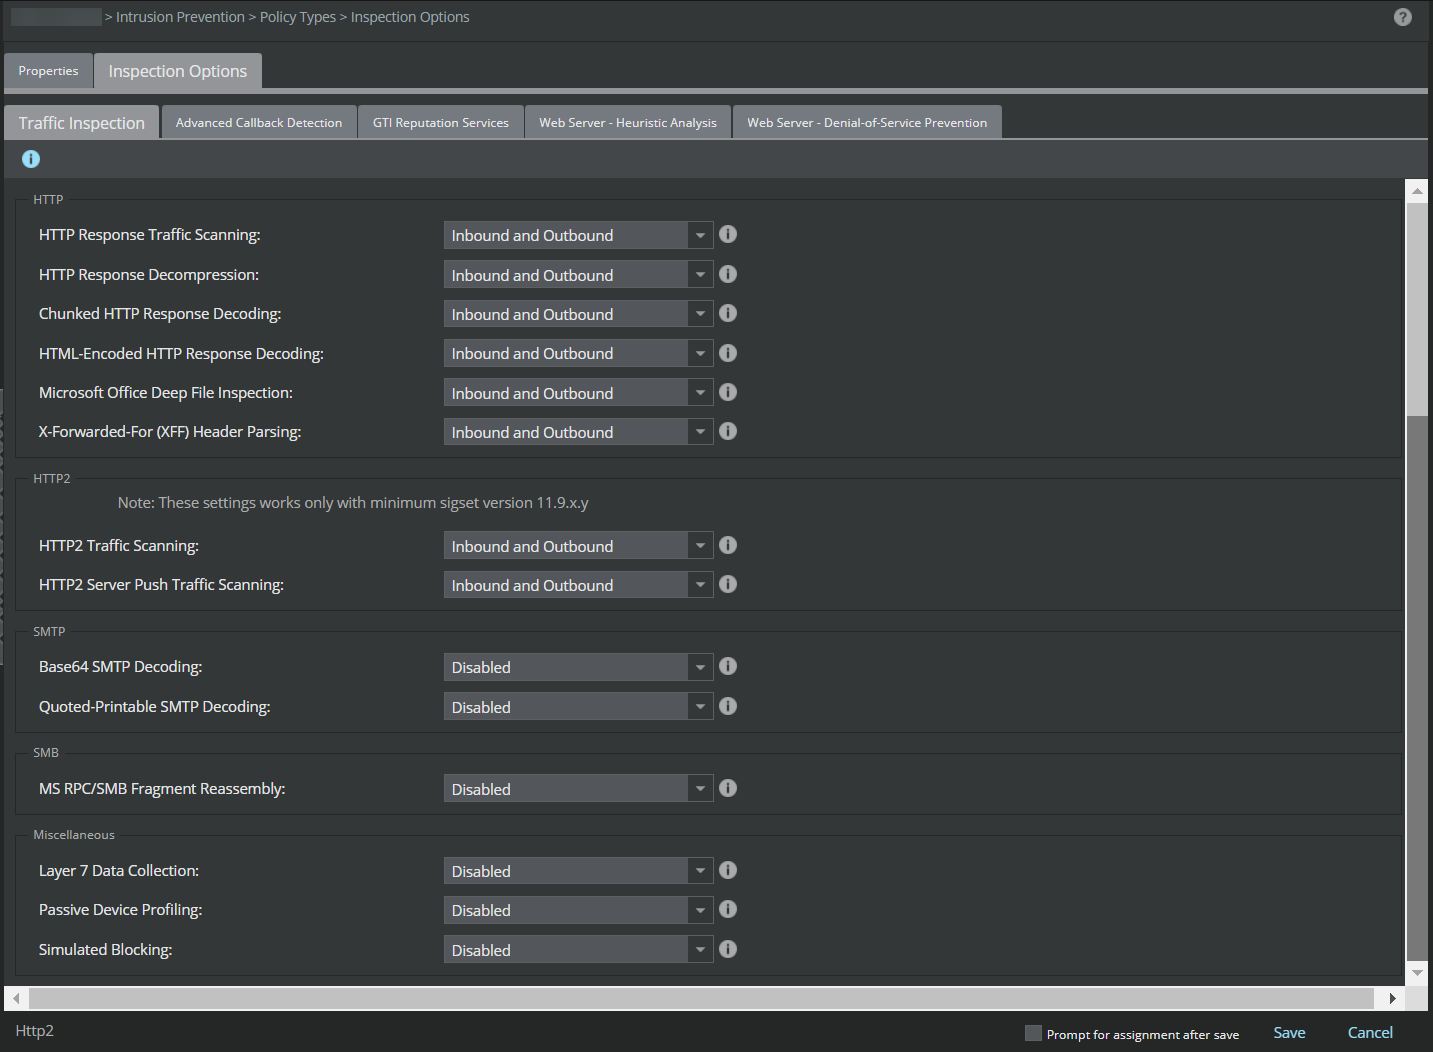
On the Traffic Inspection tab, under Miscellaneous, enable Layer 7 Data Collection in the required direction.
Click Save in the Inspection Options page.
To save the configuration changes, click Save in the <Device name/Interface> panel.
Perform the following steps to manage the layer 7 data collection options:
Click the Devices tab and select the domain from the Domain drop-down list.
In the left pane, click the Devices tab. Select the device from the Device drop-down list.
Navigate to Setup → Advanced → L7 Data Collection.
The Layer 7 Data Collection page is displayed.
In the Layer 7 Data Collection page, there are two tabs: Flows and Protocols. Using these two tabs, you can configure the required Layer 7 Data Collection options.
Important
Enabling Layer 7 Data Collection is per interface or sub-interface. However, the Layer 7 Data Collection options are device wide. That is, these changes are applied to all the interfaces and sub-interfaces of the corresponding device.
You must do a hitless or full reboot for any changes made on the Flows tab to take effect. For NS-series Sensors, you must do a full reboot as hitless reboot is not supported when SSL decryption is enabled.
You must deploy the configuration changes to the required Sensors for the changes made on the Protocols tab to take effect.
Flows tab
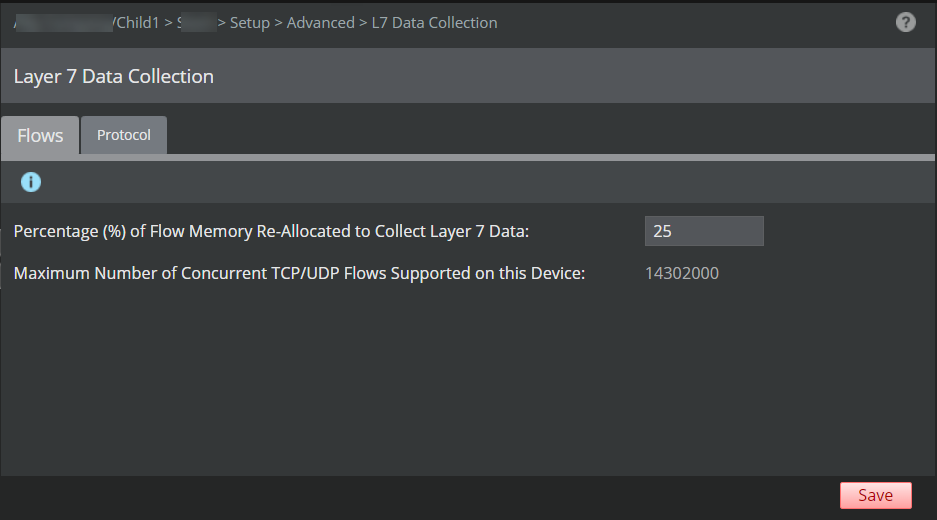
The Flows tab helps maintain the balance between flow memory percentage re-allocated for the collection of layer 7 data and number of concurrent TCP/UDP flows that a Sensor can support. The higher the percentage of flow memory re-allocated to collect layer 7 data, the higher is the probability that all layer 7 data will be collected, but the fewer number of concurrent TCP/UDP flows a Sensor would be able to support.
The following configuration options are available in the grid view of the Flows tab:
Option
Definition
Percentage (%) of Flow Memory Re-Allocated to Collect Layer 7 Data
The percentage of the maximum number of concurrent flows that capture Layer 7 data. The default value is 20%.
Note
The default value is set to 100% for the following Sensor models:
For NS9600, NS7600, and NS3600 Sensors
For NS7500 and NS9500 Sensors above version 10.1.5.116
For example, an NS7500 Sensor with 7.5Gbps throughput supports around 10,000,000 concurrent flows. So if you enable Layer 7 Data Collection with a value set to 30%, up to around 3,000,000 flows can capture Layer 7 data. Currently, if there are 5,000,000 flows passing through the Sensor, then only the first 3,000,000 flows are examined for Layer 7 data capture.
You can modify the percentage of flows that capture Layer 7 data. However, this will change the number of concurrent flows supported by the Sensor. Click Save to save the changes.
Maximum Number of Concurrent TCP/UDP Flows Supported on this Device
The maximum number of concurrent TCP/UDP flows supported by the Sensor. This capacity differs based on the Sensor model.
Refer to NS-series Sensor capacity by model number and Virtual IPS Sensor capacity by model number for the value for each model.
Save
Applies the changes across the Sensor. You must do a hitless or full reboot for the changes to take effect.
Note
For NS-series Sensors, you must do a full reboot as hitless reboot is not supported when SSL decryption is enabled.
Protocols tab
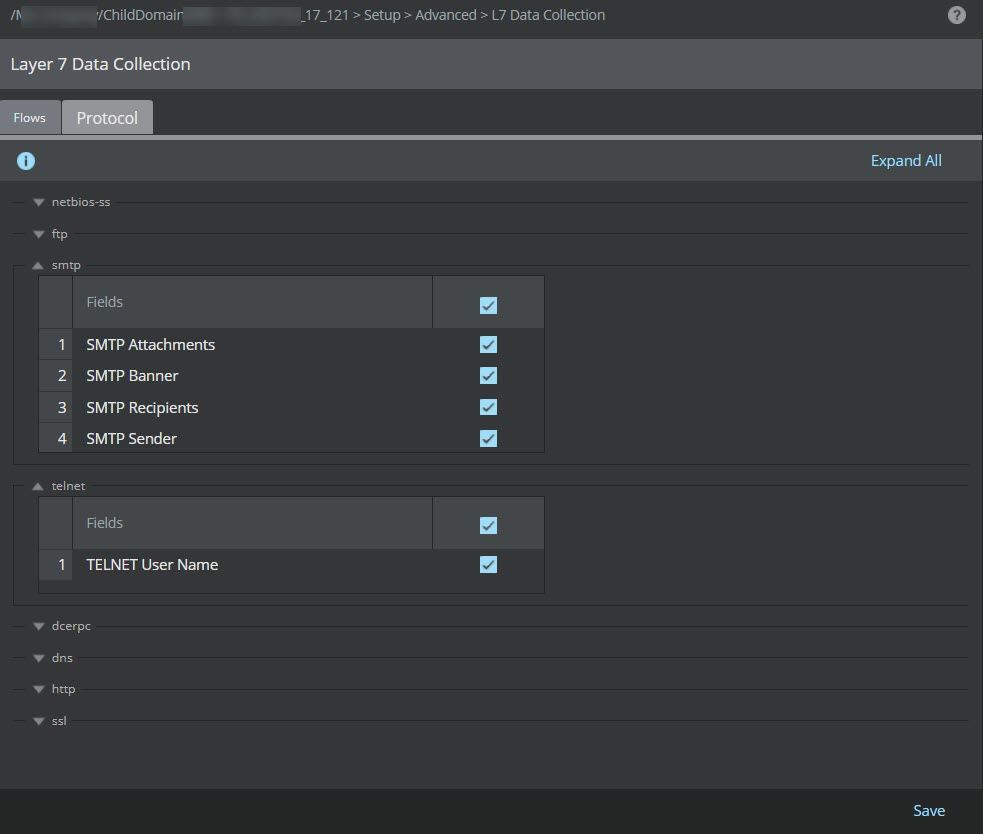
Using the Protocols tab, you can choose to enable the collection of layer 7 data for certain fields of the required protocols and optimize Sensor performance.
Use the
 button to view or customize the associated fields of all protocols listed on this tab. All fields are collapsed by default.
The following configuration options are available on the Protocols tab:
Option
Definition
netbios-ss
Click
 to view or customize the corresponding fields for the NetBIOS and SMB protocols. All fields are enabled by default. To disable a specific field, deselect the associated check-box.
Note
To view or customize the SMBv1 and SMBv2 fields, you need to use Manager and Sensor that are running on 11.1 Update 8 release versions, and a compatible signature set with SMB related attack signatures.
The following fields are available:
NetBIOS ActionNetBIOS File NameRelevant fields of command
SMB CMD NEGOTIATEin the request direction onlyRelevant fields of the command
SMB CMD TREE-CONNECT-ANDXin the request direction onlyRelevant fields of the command
SMB CMD Transin the request direction onlyRelevant fields of the command
SMB CMD Trans2in the request direction onlyRelevant fields of the command
SMB Headerin both request and response directionsRelevant fields of the command
SMBv2 Createin both request and response directionsRelevant fields of the command
SMBv2 Findin the request direction onlyRelevant fields of the command
SMBv2 Headerin both request and response directionsRelevant fields of the command
SMBv2 IOCTLin the request direction onlyRelevant fields of the command
SMBv2 NEGOTIATEin both request and response directionsRelevant fields of the command
SMBv2 Readin the request direction onlyRelevant fields of the command
SMBv2 Session Setupin both request and response directionsRelevant fields of the command
SMBv2 Tree Connectin both request and response directionsRelevant fields of the command
SMBv2 Writein the request direction only
ftp
Click
to view or customize the corresponding fields for the FTP protocol. All fields are enabled by default. To disable a specific field, deselect the associated check-box.The following fields are available:
FTP ActionFTP BannerFTP File NameFTP Return CodeFTP User Name
smtp
Click
to view or customize the corresponding fields for the SMTP protocol. All fields are enabled by default. To disable a specific field, deselect the associated check-box.The following fields are available:
SMTP AttachmentsSMTP BannerSMTP RecipientsSMTP Sender
telnet
Click
to view or customize the corresponding field for the TELNET protocol. All fields are enabled by default. To disable a specific field, deselect the associated check-box.The following field is available:
TELNET User Name
dcerpc
Click
to view or customize the corresponding field for the DCERPC protocol. All fields are enabled by default. To disable a specific field, deselect the associated check-box.Note
DCERPC L7 data collection is supported over TCP only.
Note
To view or customize DCERPC fields, you need to use Manager and Sensor that are running on 11.1 Update 8 release versions, and a compatible signature set with DCERPC related attack signatures.
The following fields are available:
Relevant fields of the command
DCERPC BindRelevant fields of the
DCERPC Headerin both request and response directionsRelevant fields of the command
DCERPC Request
dns
Click
to view or customize the corresponding fields for the DNS protocol. All fields are enabled by default. To disable a specific field, deselect the associated check-box.Note
To view or customize both DNS request and response fields, you need to use Manager and Sensor that are running on 11.1 Update 7 release versions, and a compatible signature set with DNS related attack signatures.
The following DNS request and response based fields are available:
DNS OPCodeDNS RRNameDNS RRTypeRelevant fields of the command
DNS RSP AnswerRelevant fields of the command
DNS RSP Answer RdataRelevant fields of the command
DNS RSP AuthorityRelevant fields of the command
DNS RSP Authority RdataDNS RSP Header FlagsDNS TXIDDNS Type
http
Click
to view or customize the corresponding fields for the HTTP protocol. All fields are enabled by default. To disable a specific field, deselect the associated check-box.The following fields are available:
HTTP CLSIDHTTP HostHTTP Request Content TypeHTTP Request FilenameHTTP Request MethodHTTP Request ReferrerHTTP Request URLHTTP Response Content TypeHTTP Return CodeHTTP Server TypeHTTP URIHTTP User-AgentHTTP2 STREAM IDHTTP2 Settings Enable Push (Client)HTTP2/3 HTTP VERSION
ssl
Click
to view or customize the corresponding fields for the SSL protocol. All fields are enabled by default. To disable a specific field, deselect the associated check-box.The following fields are available:
SSL Certificate Common NameSSL Server Name Indication
Save
Applies the changes across the Sensor. You must deploy the configuration changes to the required Sensors for the changes to take effect. For more information, see Deploy pending changes to a device.