Following are the steps to enable mobile malware detection:
The GTP feature is disabled on the Sensor by default. You can enable the GTP feature on the Sensor by using the these steps:
Go to Devices → <Admin Domain Name> → Devices → <Device Name> → Setup → Advanced → Advanced Device Settings and select Inspect Tunneled Traffic and click Save. This enables parsing of traffic for all supported tunneling protocols including GTP for malware detection. By default, this checkbox is deselected.
Note
At an admin domain level, configure this for multiple Sensors by navigating to Devices → <Admin Domain Name> → Global → IPS Device Settings → Advanced Device Settings and select Inspect Tunneled Traffic and click Save.
Check the status of tunneled traffic with this CLI command:
Syntax:
show parsetunneledtraffic statusDisplays the status of the current tunneling configuration of the Sensor.
Enable GTI File Reputation under Policy → <Admin Domain Name> → Intrusion Prevention → Policy Types → Advanced Malware and click
 .
To create a new policy and enable the GTI File Reputation for the required file type, navigate to Policy → <Admin Domain Name> → Intrusion Prevention → Policy Manager.
Configure the DNS Server under Devices → <Admin Domain Name> → Global → Common Device Settings → Name Resolution.
For more information, see section Configure the DNS server details, chapter Configure Firewall Policies.
Set the policy to Default Prevention under Policy → <Admin Domain Name> → Intrusion Prevention → Policy Types → IPS.
Note
The Default Prevention policy is set by default. In case it is not set, then navigate to the above mentioned path to set it.
You can set and view the following policy details configured in the Manager:
Reconnaissance attack details
Callback Detector details
Network Forensics details
Packet Capture details
Customizing scan attack details
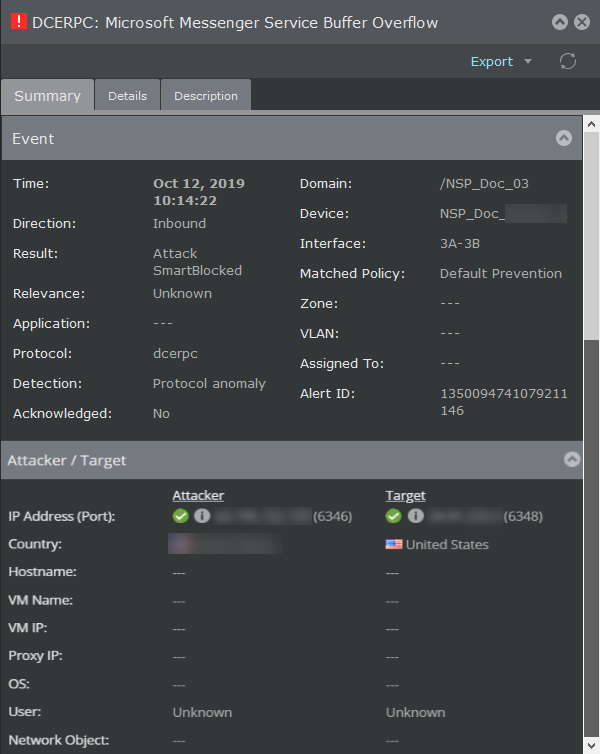
Trellix IPS generates alerts and events, which help keep track of the malware, bots, worms detected.
You can view the attacker and target IP addresses from where the attack was generated when GTP feature is enabled. The alerts can be viewed in Attack Log which also displays the details of the attack.