Make sure you have configured a syslog server with an IP address that will be reachable to the respective Sensors.
By configuring settings in the page, you can enable syslog forwarding for all devices in the domain.
Select Devices → <Admin Domain Name> → Global → IPS Device Settings → IPS Event Logging.
Configure the following fields.
Field
Description
Enable Logging
Select the checkbox to configure the settings.
Syslog Server IP Address
The IP address of the syslog server which becomes the destination of the alert notifications sent by all devices.
Syslog Server Port (UDP)
Port on the target syslog server that is authorized to receive syslog messages.
The default protocol for syslog forwarding from Sensors is UDP. Therefore, this port must not be altered.
Syslog Facility
Standard syslog prioritization value. The choices are as follows:
Security/authorization (code 4)
Security/authorization (code 10)
Log audit (note 1)
Log alert (note 1)
Clock daemon (note 2)
Local user 0 (local0)
Local user 1 (local1)
Local user 2 (local2)
Local user 3 (local3)
Local user 4 (local4)
Local user 5 (local5)
Local user 6 (local6)
Local user 7 (local7)
Attack Severity to Syslog Priority Mapping
You can map each severity (Informational, Low, Medium, or High) to one of these standard syslog severities:
Emergency – System is unusable
Alert – Action must be taken immediately
Critical – Critical conditions
Error – Error conditions
Warning – Warning conditions
Notice – Normal but significant condition
Informational – Informational messages
Debug – Debug-level messages
Send Test Message
Clicking this option sends a test message from the Manager to the syslog server.
It is used to check whether the syslog server is reachable.
Provide any filtering parameters that you want to provide.
Field
Description
Attack Logging
Log All Attacks sends notifications about every attack that passes through the Sensor.
Log Some Attacks sends notifications about specific attacks based either on the severity or the settings in the attack definition.
Selecting The attack definition has syslog notification explicitly enabled instructs the Sensor to check the attack definition before sending out syslog notifications.
Note
If you only select this checkbox and do not configure any of the attack definitions for syslog notification, no notifications will be forwarded to the server.
Selecting Minimum Severity of instructs the Sensor to check the severity of the attack before forwarding the notification. Only attacks of a specific severity and higher will be forwarded; therefore, you must specify the lowest severity attacks.
For example, if you only select this checkbox and specify Low, all attacks that have a severity of low or higher will be notified to the server.
Select the message you want displayed in the notification.
Field
Description
Message
The default message is a quick summary of an alert with two fields for easy recognition: Attack Name and Attack Severity. A default message reads:
Attack $IV_ATTACK_NAME$ ($IV_ATTACK_SEVERITY$).The variables listed in the table are supported by the Sensor.
Note
Prior to Sensor software version 10.1.5.116, the variables $IV_MALWARE_FILE_SHA1_HASH$ and $IV_MALWARE_FILE_SHA256_HASH$ do not display the file hashes.
Syslog variable name
Description
Attack Log column
$IV_ADMIN_DOMAIN$
The domain to which the Sensor that detected the attack belongs.
Domain
$IV_ALERT_ID$
The globally unique ID that the Manager assigns to an alert.
Alert ID
$IV_ALERT_TYPE$
The Sensor decides the type of alert. This is mainly used by the Manager for its internal processing. This is not related to the Attack Category or Attack Sub-category. Some example alert types are signature, statistical anomaly, threshold anomaly, port scan, and host sweep.
Not available
$IV_APPLICATION_PROTOCOL$
The application-layer protocol associated with the attack traffic. This is not related to the Application Identification feature, and this information is displayed even if you have not enabled Application Identification. There could be instances when a Sensor might not be able to detect the protocol.
Application
$IV_ATTACK_CONFIDENCE$
This is a value between 1 and 7. For example, a confidence level of 7 indicates that there is low possibility of the attack being a false-positive.
The attack confidence values are inversely related to the Benign Trigger Probability (BTP) values of attack signatures.
Confidence 1 = BTP 7 (high)
Confidence 2 = BTP 6 (high)
Confidence 3 = BTP 5 (medium)
Confidence 4 = BTP 4 (medium)
Confidence 5 = BTP 3 (medium)
Confidence 6 = BTP 2 (low)
Confidence 7 = BTP 1 (low)
Note
When the BTP value is 0, there is no corresponding confidence value for the attack.
Not available
$IV_ATTACK_COUNT$
The number of times the attack occurred. This information is more relevant for suppressed alerts. Consider you have enabled alert suppression such that the alert is raised only when the attack is seen 5 times within 30 seconds. Subsequently, the Sensor detected this attack 10 times within 30 seconds. Then the attack count for this alert is 10.
Attack Count
$IV_ATTACK_ID$
Trellix Advanced Research Center assigns a universally unique hexadecimal value to each attack. This field displays the integer value of the hexadecimal ID assigned by Trellix ARC.
The equivalent hexadecimal value is displayed in the Attack Information & Description page as Intruvert ID.
$IV_ATTACK_NAME$
The name assigned by Trellix ARC to an attack.
Name
$IV_ATTACK_SEVERITY$
Indicates the severity value of an attack specified in the corresponding attack definition.
0 - Informational
1 to 3 - low
4 to 6 - medium
7 to 9 - high
Attack Severity (high, medium, low, or informational)
$IV_ATTACK_SIGNATURE$
The ID of the signature that matched the attack traffic.
Not available
$IV_ATTACK_TIME$
The time when the Sensor created the alert.
Time
$IV_CALLBACK_ACTIVITY
The name of the Callback Activity family.
Callback Activity
$IV_CATEGORY$
The category to which the attack belongs. This is decided by Trellix ARC. Some examples are exploit, policy violation, and reconnaissance. You can view the attack categories in the IPS Policy Editor when you group by Attack Category.
Attack Category
$IV_CC_DOMAIN
The name of the Callback Activity domain.
C&C Domain
$IV_DESTINATION_IP$
The destination IP address to which the attack is destined.
Target IP Address
$IV_DESTINATION_PORT$
The port number on the destination host to which the attack traffic is sent.
Target Port
$IV_DEST_APN$
This is the destination Access Point Name (APN). This information is part of a mobile subscriber's identity data and is relevant only if you have deployed Sensors to monitor mobile networks. To see this data, you must enable capturing and tagging of mobile subscriber data in the alerts by using the
set mnsconfigSensor CLI command.Not available
$IV_DEST_IMSI$
This is the destination International Mobile Subscriber Identity (IMSI). The details provided for APN apply to this as well.
Not available
$IV_DEST_OS$
The operating system installed on the destination host.
Target OS (in Alert Details panel)
$IV_DEST_PHONE_NUMBER$
This is the destination mobile phone number. The details provided for APN above apply to this as well.
Not available
$IV_DETECTION_MECHANISM$
The method the Sensor used to detect the attack. For example, signature, multi-flow-correlation, threshold, and so on. Each method relates to a specific attack category.
Detection (in Alert Details panel)
$IV_DIRECTION$
Indicates whether the attack traffic originated from your network or the outside network. For example, inbound direction means that the attack traffic originated from the outside network, targeting the hosts on your network.
Direction
$IV_INTERFACE$
The interface or sub-interface on which the Sensor detected the attack traffic.
Interface
$IV_LAYER_7_DATA
Provides the Layer 7 data.
Layer 7 Data
$IV_MALWARE_CONFIDENCE$
Confidence level of the malware as detected by the engine
Malware Confidence
$IV_MALWARE_DETECTION_ENGINE$
Engine which detected the malware(GAM,GTI,PDF‑JS,etc).
Engine
$IV_MALWARE_FILE_LENGTH$
The length of the malware file.
Not available
$IV_MALWARE_FILE_MD5_HASH$
The MD5 hash of the malware file(fingerprint).
File Hash
$IV_MALWARE_FILE_NAME$
The name of the malware file. For SMTP traffic, it displays the file name of the attachment and for HTTP traffic, it displays the URL of the file.
File Name
$IV_MALWARE_FILE_SHA1_HASH$
The SHA1 hash of the malware file (fingerprint).
File Hash
$IV_MALWARE_FILE_SHA256_HASH$
The SHA256 hash of the malware file (fingerprint).
File Hash
$IV_MALWARE_FILE_TYPE$
The file type of the malware file
Not available
$IV_MALWARE_VIRUS_NAME$
The virus name as detected by GAM.
Not available
$IV_NETWORK_PROTOCOL$
The network protocol, such as TCP, of the attack traffic.
Protocol (in the Alert Details panel)
$IV_QUARANTINE_END_TIME$
The time when the attacking host will be out of quarantine. This is relevant only if you had enabled Quarantine feature.
Not available
$IV_RESULT_STATUS$
Indicates whether the attack traffic reached the victim host.
Result
$IV_SENSOR_ALERT_UUID$
The universally unique ID assigned by the Sensor for the alert. For a specific alert raised by a specific Sensor, the Central Manager also displays the same ID.
Alert ID
$IV_SENSOR_CLUSTER_MEMBER$
The member Sensor of a HA pair that generated the alert.
Not available
$IV_SENSOR_NAME$
The Sensor that generated the alert.
Device
$IV_SOURCE_IP$
The IP address of the attacking host.
Attacker IP Address
$IV_SOURCE_OS$
OS of the attacking host.
Attacker OS (in Alert Details panel)
$IV_SOURCE_PORT$
The port number on the attacking host from which the attack traffic is sent.
Attacker Port
$IV_SRC_APN$
This is the source Access Point Name (APN). This information is part of a mobile subscriber's identity data and is relevant only if you have deployed Sensors to monitor mobile networks. To see this data, you must enable capturing and tagging of mobile subscriber data in the alerts by using the
set mnsconfigSensor CLI command.Not available
$IV_SRC_IMSI$
This is the source International Mobile Subscriber Identity (IMSI). The details provided for APN apply to this as well.
Not available
$IV_SRC_PHONE_NUMBER$
This is the source mobile phone number. The details provided for APN apply to this as well.
Not available
$IV_SUB_CATEGORY$
The subcategory to which the attack belongs. This is decided by Trellix ARC, and is a classification within Attack Category. Some examples are brute-force, buffer-overflow, host-sweep, and restricted-application. You can view the attack subcategories in the IPS policy editor when you group by Attack Subcategory.
Attack Subcategory (in Alert Details panel)
$IV_VLAN_ID$
The VLAN ID seen on the attack traffic.
VLAN
Click Save.
You have now enabled syslog forwarding for all Sensors belonging to a domain. You will notice in the IPS Event Logging page of a Sensor that all settings you have just configured are automatically inherited by each Sensor. The only remaining step to begin sending notifications will be to perform a configuration update in each Sensor.
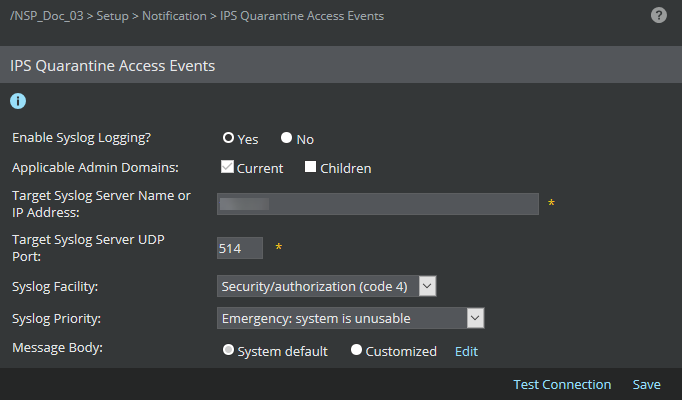
However, if you want to modify settings for any of the Sensors, you will need to configure these settings individually for each Sensor. To configure a Sensor for syslog forwarding, go to Enable syslog forwarding for alert notifications at the Sensor level.