The following are the steps to enable syslog forwarding for a Sensor.
Click the Devices tab.
Select the domain from the Domain drop-down list.
On the left pane, click the Devices tab.
Select the device from the Device drop-down list.
Select Setup → Quarantine → Logging.
Enabling syslog forwarding for a Sensor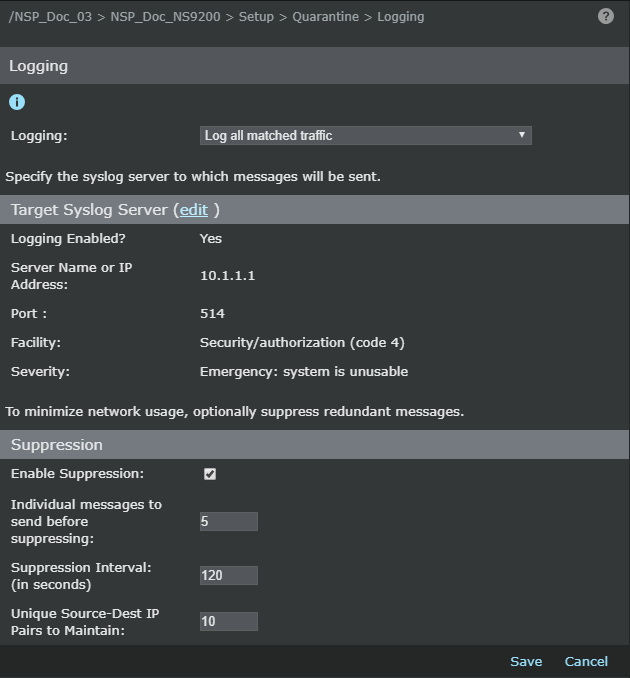
Specify the Sensor-level syslog details in the corresponding fields.
Option
Definition
Logging
Sets the condition when the Manager or the Sensor should send the log message to the syslog server. The options are:
Disabled on this device — This disables logging on the device. This option overrides the setting on the individual access rules. The remaining options in the Logging page are not displayed if you choose this option.
Log all matched traffic — Logs all traffic that matched a rule regardless of whether it was dropped/denied or permitted. This option overrides the setting on the individual access rules.
Log all dropped/denied traffic — Logs all traffic that was either dropped or denied according to an access rule. This option overrides the setting on the individual access rules.
Log all permitted traffic — Logs all traffic that was permitted according to an access rule. This option overrides the setting on the individual access rules.
Log traffic only if the matched rule is configured to log — Logs only if you had configured logging for the corresponding access rule.
Target Syslog Server
Displays the syslog server details that you have configured at the corresponding admin domain. Click Edit to go to the Syslog page and modify the required details.
Enable Suppression
Option to suppress redundant messages. Only if you select it, the remaining fields in the Suppression table are displayed.
Suppressing log entries causes the Sensor to send initial log entries representing the first instance of an event (the number of which is configurable), and then suppress further instances of the same event for a configurable number of seconds. This is a useful tool in keeping the log file size under control.
Individual messages to send before suppressing
Indicates the number of messages to be sent within the seconds specified in the Suppression Interval field for suppression to begin.
Suppression Interval (in seconds)
Time span in which you accumulate instances of the same rule match. This value acts as a timer; when the timer expires, the current instance is cleared to make room for a new suppression instance.
Unique Source-Dest IP Pairs to Maintain
Determines the number of unique suppression instances to maintain at a given time. For example, if you enter the number 10, then 10 unique instances can be tracked at a given time. Once 10 is reached, all other cases are kept in a single "wildcard" instance; thus, other unique combinations that occur outside of the 10 uniquely maintained instances are maintained as one instance, and source and destination IP do not appear in the summary since multiple addresses may be involved. An entry is removed after the time limit (Suppression interval) expires.
Save
Saves the configuration in the Manager database.
Note
Do a configuration update to the applicable Sensors for the configuration to take effect.
Cancel
Reverts to the last saved configuration.