You can inherit the syslog details from the parent domain or configure specifically for the current domain. This applies to all the Sensors in the domain only with respect to Quarantine. You can also choose to apply it to a child domain.
Steps:
To access the Syslog page, do the following.
Click the Manager tab.
From the Domain drop-down list, select the domain you want to work in.
Select Setup → Notification → IPS Quarantine Access Events.
Specify the domain-level syslog details in the corresponding fields.
Syslog server details for Quarantine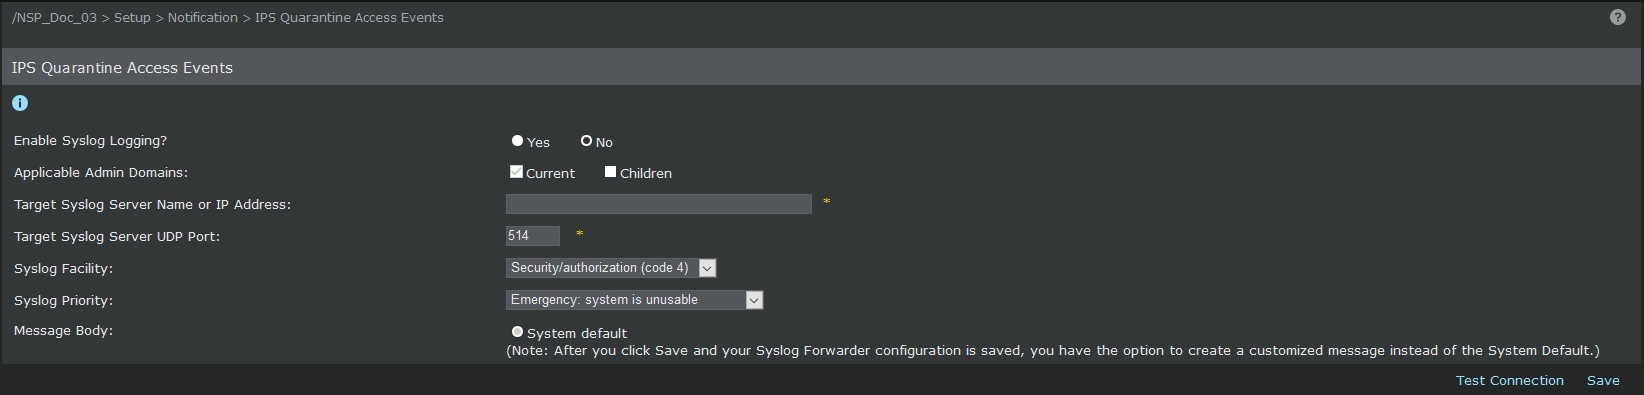
Option
Definition
Enable Syslog Logging?
If you select Yes, the details of the traffic that matched a quarantine zone access rule is forwarded to a syslog server. You can also configure the details now and enable it at a later time.
Applicable Admin Domains
Current — The syslog configuration applies only to the current domain. This is always enabled for the current domain.
Children —The syslog configuration applies to child domains as well. You can also modify this syslog configuration at a child domain if required.
Target Syslog Server Name or IP Address
Enter the syslog server name or its IP (IPv4 or IPv6) address. If you specify the syslog server name:
The Manager uses the DNS servers configured in its TCP/IP properties.
If you choose the Sensor to forward the logs to a syslog, then the Sensor uses the DNS servers that you configured in the Name Resolution page for the Sensor.
Target Syslog Server UDP Port
Enter the communication port number on the target server which is authorized to receive syslog messages. The standard port for syslog, which is 514, is pre-filled in the field. If you are using a non-standard port, then replace 514 with that number.
Syslog Facility
Lists the syslog prioritization values.
By default, the syslog messages forwarded to a syslog server are of Security/authorization <prioritization value>.
Syslog Priority
Lists the syslog priority values.
By default, the syslog messages forwarded to a syslog server are of Debug severity.
Message Body
Optionally, customize the default syslog message. There are two types:
System Default — The default message is a quick summary for easy recognition.
Customized — You can customize the message after you successfully save the syslog configuration details. Click Test Connection to view the option to edit the default message.
Important
Till 11.1 Update 4 release, all Syslog notifications generated from the Manager UI were prefixed with the timestamp format MMM DD HH:MM:SS. From the 11.1 Update 5 release onwards, along with this timestamp, additional timestamp with format [MMM DD, YYYY HH:MM:SS] is appended to each Syslog notification from the Manager for auditing purposes. This timestamp update is independent of the syslog variables (default or customized) used to configure syslog notifications.
As a user, you need to update the Syslog parsing logic in the third-party Syslog application(s) in use to avoid any timestamp conflicts in the Syslog notifications.
Test Connection
Checks if the Manager is able to send syslogs to the syslog server. Check your syslog server if it has received the test message from the Manager. If not, check the syslog server name or IP address that you had provided. Ping the syslog server from the Manager server to see if the Manager is able to reach the syslog server.
Note
You can use the test connection feature, even if you have set Enable Syslog Logging? to no.
Save
Saves the syslog configuration changes in the Manager database. Once you click Save, you will be able to customize the message format sent to the syslog server.
Note
If you have modified the syslog configuration, then do a configuration update of the Sensors for the changed settings to take effect.