The CAC authentication feature is disabled by default. It is mandatory to set up the CAC user accounts and import the CAC certificates to the Manager, before enabling it.
To enable CAC, do the following:
Steps:
Log in to the Manager GUI.
Go to, Manager → <Admin Domain Name> → Setup → GUI Access → CAC Authentication.
The CAC Authentication page opens.
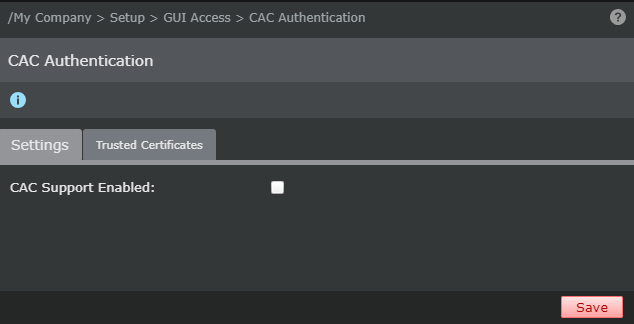
In the Settings tab, configure the CAC Authentication as needed.
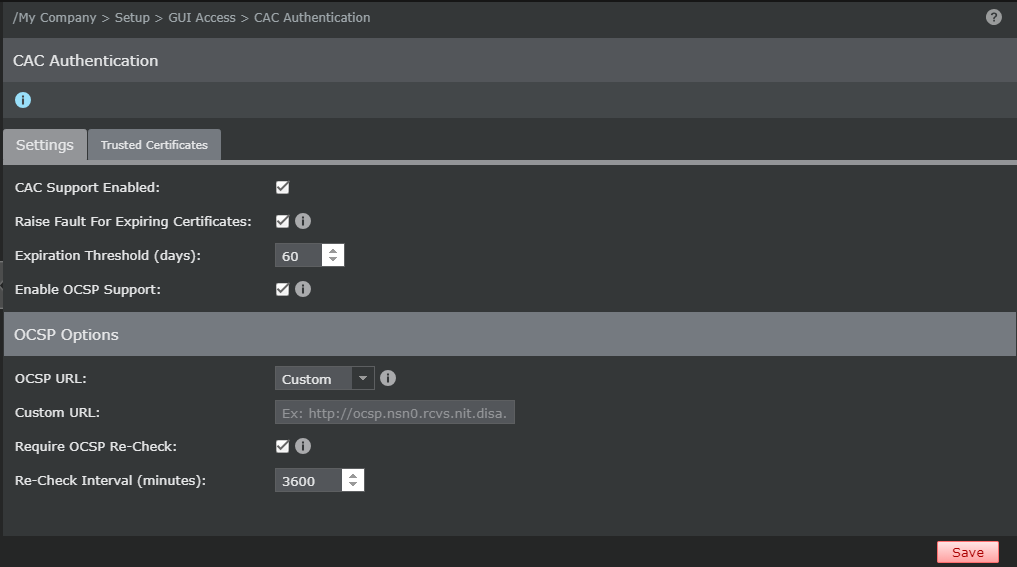
The table below describes the fields available for configuration:
Field
Description
CAC Support Enabled
Select the checkbox to enable CAC Authentication. By default, the CAC Authentication is disabled.
Raise Fault for Expiring Certificates
Select the checkbox to configure the Manager to generate faults when a trusted certificate is about to expire.
Expiration Threshold (days)
Number of days for the trusted certificate expiration when a fault is generated in the Manager.
Note
The Expiration Threshold (days) can be within the range of 30 to 60 days only.
Note
The Expiration Threshold (days) can be configured only when the Raise Fault for Expiring Certificate option is enabled.
Enable OCSP Support
Select the checkbox to enable OCSP Support. By default, the OCSP Support is disabled.
OCSP Options
OCSP URL
Select Default to use the OCSP URL defined in the trusted certificate or Custom to configure a unified OCSP URL for all trusted certificates in the Manager.
Custom URL
Specify the OCSP URL for authenticating the trusted certificates.
Note
The Custom URL field is available only when you have the OCSP URL option set to Custom.
Require OCSP Re-Check
Select Yes to verify the authenticity of the trusted certificate after a definite interval.
Re-Check Interval (minutes)
Specify the duratin in minutes after which the authenticity of the trusted certificate is rechecked.
Note
The Re-Check Interval (minutes) can be within the range of 30 to 1440 minutes only.
Note
The Re-Check Interval (minutes) can be configured only when the Require OCSP Re-Check option is enabled.
Click Save.
Log in to the Manager shell.
Stop the Manager service using the
manager stopcommand.Restart the Manager service using the
manager startcommand.