The User Activity option enables the forwarding of Trellix IPS audit information to a syslog server. Syslog forwarding enables you to view the forwarded audit information via a third-party syslog application. For syslog forwarding, the root domain and parent domains have the option to include audit information from all corresponding child domains. To enable syslog forwarding for audit notification, do the following:
Select Manager → <Admin Domain Name> → Setup → Notification → User Activity → Syslog.
The Syslog page is displayed.
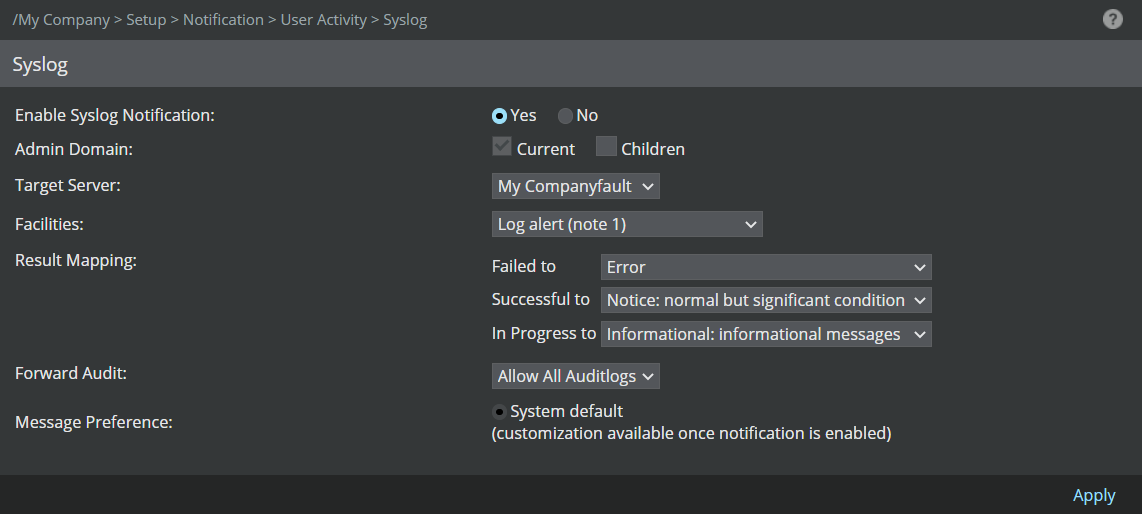
Fill in the following fields:
Field
Description
Enable Syslog Notification
Yes is enabled; No is disabled
Admin Domain
Current— Send notifications for audit information in the current domain. Always enabled for current domain.
Children— Include audit information for all child domains of the current domain.
Target Server
Choose the target server from the drop-down to which audit information is forwarded.
Facilities
Standard syslog prioritization value. The choices are as follows:
Security/authorization (code 4)
Security/authorization (code 10)
Log audit (note 1)
Log alert (note 1)
Clock daemon (note 2)
Local user 0 (local0)
Local user 1 (local1)
Local user 2 (local2)
Local user 3 (local3)
Local user 4 (local4)
Local user 5 (local5)
Local user 6 (local6)
Local user 7 (local7)
Result Mapping
You can map each audit result (Failed to, Successful to, and In Progress to) to one of the standard syslog severities listed below (default result severities are noted in parentheses):
Emergency— System is unusable
Alert— Action must be taken immediately
Critical— (HIGH) Critical conditions
Error— Error conditions
Warning— (MEDIUM) Warning conditions
Notice— (LOW) Normal but significant condition
Informational— (INFORMATIONAL) Informational message
Debug— Debug-level messages
Forward Audit
Select the severity of the audit that you want to be forwarded to the syslog server. The options are:
Allow all Auditlogs
Failed only
Successful only
In Progress only
Message Preference
Select the preference of the message. The options are:
System default— This is available by default
Customized— This is available once the notification is enabled
Click Apply.
Note
You must click Apply before you will be able to customize the message format sent to your syslog server.
Select the Message Preference to send as the syslog forwarding message. The choices are:
System Default — The default message is a quick summary of a fault with three fields for easy recognition: Action, Result, and Time. A default message reads:
$IV_AUDIT_ACTION$ $IV_AUDIT_RESULT$ at $IV_AUDIT_TIME$
Customized — Create a custom message. To create a custom message, do the following:
Click Edit to create a custom message.
Type a message and select (click) the parameters for the desired alert identification format. The following figure displays a custom message. You can type custom text in the Message field as well as click one or more of the provided elements below the field box.
Click Save when finished to return to the Syslog page. The Customized button is automatically selected after you have customized the Message Preference.
A few important points to consider:
For syslog information to appear correctly, ensure that you use the dollar-sign ($) delimiter immediately before and after each element. Example: $ATTACK_TIME$
From 11.1 Update 9 release, $IV_MANAGER_DETAILS$ is introduced to display the hostname and IP addresses of the Manager. For an MDR setup, it further specifies if the Manager is primary or secondary.
From the 11.1 Minor 6 release, the IPS Manager can send 16384 bytes in a single syslog message.
Till 11.1 Update 4 release, all Syslog notifications generated from the Manager UI were prefixed with the timestamp format MMM DD HH:MM:SS. From the 11.1 Update 5 release onwards, along with this timestamp, additional timestamp with format [MMM DD, YYYY HH:MM:SS] is appended to each Syslog notification from the Manager for auditing purposes. This timestamp update is independent of the syslog variables (default or customized) used to configure syslog notifications.
As a user, you need to update the Syslog parsing logic in the third-party Syslog application(s) in use to avoid any timestamp conflicts in the Syslog notifications.
Syslog variables for audit notificationSyslog variable name
Description
$IV_AUDIT_ACTION$
The audit action value based on the action ID that was passed.
$IV_AUDIT_RESULT$
Indicates the stage of auditing (received, succeeded, failed, or ongoing).
$IV_AUDIT_TIME$
Time stamp of the audit message.
$IV_AUDIT_MESSAGE$
The audit message.
$IV_AUDIT_USER$
The username for the audit.
$IV_AUDIT_CATEGORY$
The action taken for the audit.
$IV_AUDIT_DOMAIN$
Name of the domain.
$IV_AUDIT_DETAIL_COMMENT$
Displays committed comments if the audit details are available.
$IV_AUDIT_DETAIL_DELTA$
Displays audit data if the audit details are available.
$IV_MANAGER_DETAILS$
The hostname and IP address of the Manager. For an MDR setup, it further specifies if the Manager is primary or secondary.
Click Save.