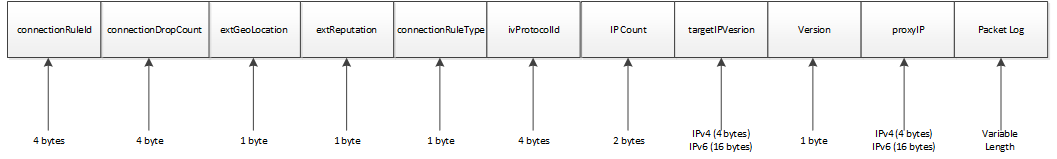
All alerts that have iv_alert.alertType = 5 are hostsweep alerts. Its iv_alert_data.typeSpecific data has following format:
First byte contains number of IP information to follow. If there are ten IPs involved in the hostsweep, then first byte of typeSpecificData will contain value 10. Each subsequent four bytes will contain the actual IP values.
Total length of typeSpecificData in above example will be 1 + ( 10* 4) = 41 bytes.
The source and destination VLAN ID follow with each being 4 bytes. These fields are applicable only for NTBA alerts.
The details of the alert are as follows:
Number of bytes | Value |
|---|---|
4 | Connection rule ID |
4 | Connection drop count |
1 | External geographical location |
1 | External reputation |
1 | Connection rule type |
4 | Protocol ID |
2 | IP address count |
4 (IPv4) or 16 (IPv6) | Version of the target IP address |
1 | Version information |
4 (IPv4) or 16 (IPv6) | Proxy IP address |
Variable length | Packet logs |