The Sensor is deployed inline in the host network; having established the baseline of the normal traffic pattern for the network in the first 48 hours of deployment (learning mode), and built a long-term profile for the statistical data on the SYN segments in the TCP connection. Consider that the Sensor is in the detection mode. It continues to gather statistical data and update its long-term profile. The learning mode uses statistical data gathered over a time window to create normal short-term and long-term profiles.
Consider the following example of a TCP SYN flood attack.
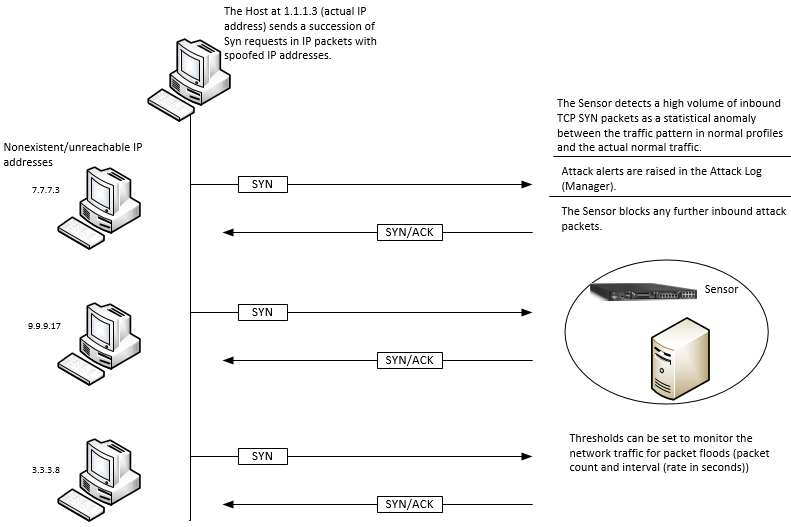
There is a flood of TCP SYN packets using spoofed IP addresses to the target host.
The Sensor detects a high volume of inbound TCP SYN packets. This upsurge in the packets is regarded as an anomaly between the traffic pattern in normal profiles and the actual network traffic. The Sensor monitors statistical anomalies in traffic with reference to learned data (DoS profiles) on normal traffic. Refer to the section Statistical anomaly. The following is a sample DoS profile. Bin 2 indicates a lower percentage of long-term traffic when compared to the short term, and hence traffic is blocked.
0: 0.0.0.0/6 AS=1.563% LT=49.969% ST=100.00% stR=1.0001: 128.0.0.0/2 AS=25.000% LT=0.021% ST=0.00% stR=0.000*2: 64.0.0.0/2 AS=25.000% LT=1.615% ST=100.00% ltR=2357.098 stR=148966.4003: 192.0.0.0/2 AS=25.000% LT=0.021% ST=0.00% stR=0.0004: 32.0.0.0/3 AS=12.500% LT=0.000% ST=0.00% stR=0.0005: 16.0.0.0/4 AS=6.250% LT=0.000% ST=0.00% stR=0.0006: 8.0.0.0/5 AS=3.125% LT=0.000% ST=0.00% stR=0.0007: 4.0.0.0/6 AS=0.000% LT=11.752% ST=0.00% ltR=16885.654 stR=0.000Based on the configured DoS policy settings, alerts are raised in the Attack Log. The learning mode can be customized on the Manager for inbound, outbound, or bidirectional traffic. The severity of the attack and Sensor response is also configurable. Refer to the section Configure the Learning mode.
The alerts in the Attack Log display the SYN packet rate data relating to the violated learning mode measure, the violated measure's packet rate for the last minute when the alert was raised, and the ranges of IP addresses, both source and destination, that were involved in the DoS attack.
The Sensor blocks any further inbound attack packets. The blocking of packets can be enabled while configuring the learning mode or from the Attack Log once an alert is raised.
Additionally, thresholds can also be set to monitor the number of packets per second.
In the threshold mode, the Sensor monitors the network traffic for packet floods, transmitting through from a source to a destination as detected within a Sensor interface or subinterface. When configuring the DoS policy or customizing at the interface or subinterface level, the count and interval (rate in seconds) for the threshold attacks to be detected.
Note
Combining threshold and learning methods greatly improves reliability of detection.
DoS policy applies to inbound, outbound, and bidirectional traffic. Inbound traffic is that traffic received on the port designated as outside (that is, originating from outside the network) in inline or tap mode. Typically, inbound traffic is destined to the protected network, such as an enterprise intranet.
Outbound traffic is that traffic sent by a system in your intranet, and is on the port designated as inside (that is, originating from inside the network) in inline or tap mode.
When GTI is enabled, IP Reputation is applicable only for inbound connections. When GTI is enabled and Connection Limiting rules are configured, you can block the malicious traffic received on the inbound connections. For example, you can deploy a Sensor in front of a web server, and enable GTI along with Connection Limiting policies and Advanced Malware policies to limit access to the server and prevent DoS attacks.