Traffic that uses a different path for the request vs. response is termed as asymmetric traffic. There are chances of having asymmetric traffic within a network, when networks increase in size.
If there are chances of asymmetric traffic in your network, consider the following options:
Install IPS Sensors at a location where the traffic is symmetric.
Implement a port clustering configuration for asymmetric traffic. Port clustering (referred to as Interface groups in the Manager) enables multiple ports on a single Sensor to be grouped together for effective traffic monitoring. Asymmetric networks are common in load balancing and active/passive configurations, and a complete transmission may be received on one segment, but depart on another. Thus, keeping state of asymmetric transmissions is essential for successfully monitoring the traffic. Interface groups normalize the impact of traffic flows split across multiple interfaces, thus maintaining state to avoid information loss.
Place an IPS Sensor each on the request and the response path of the asymmetric traffic and create a HA pair to sync up the traffic flow between the two Sensors.
If you are using a HA pair to monitor asymmetric traffic where the TCP traffic is going through two geographically different data centers, connect the Sensors using dark fiber. In this option, both the Sensors will have full state.
When the distance between the two IPS Sensors is such that a HA pair cannot be created, consider enabling Stateless Inspection. In Stateless Inspection, the Sensor detects attacks without requiring a valid TCP state. This option should be used only when Sensors are placed in a network where the Sensors do not see all packets of a TCP flow like in an asymmetric network configuration.
Note
When Stateless Inspection is enabled, ACLs and syn cookie protection cannot be enabled. So, HTTP redirection to the Remediation Portal may or may not work depending on your network deployment scenario, for example, in a setup where SYN+ACK packets cannot be sent from the Sensor to the client.
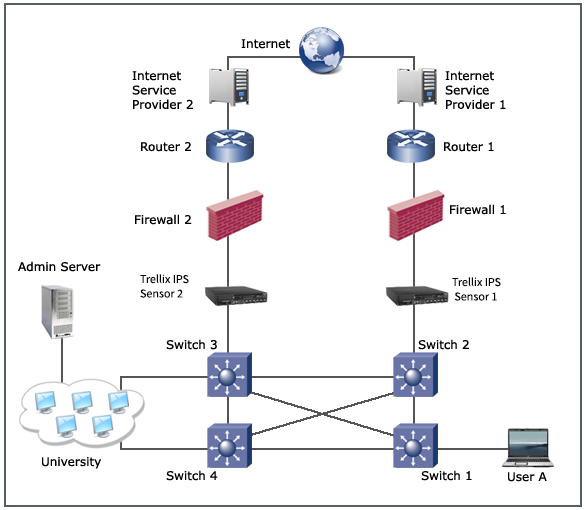
The diagram below explains HTTP traffic flow in an asymmetric network between User A and the University Admin server. The outgoing connection flow from User A is through Switch 1, Switch 2, IPS Sensor 1, Router 1, Internet Service Provider 1, to the Internet connection. The return path for the packet however, is through Internet Service Provider 2, Router 2, etc. If traffic flows by the Sensor in an asymmetric manner as described above, all packets of a TCP flow are not visible to a single Sensor.
In such a scenario, if Stateless Inspection is enabled, the Sensor will inspect packets without having the valid state for the TCP connection. Consequently, it might generate false positives that is, when a single communication flow is divided across paths, each interface will receive and analyze part of the conversation and therefore be susceptible to false positives and false negatives.
Caution
When you enable Stateless Inspection, there are chances of false positives, and the detection accuracy will be lower compared to when the Sensor sees all traffic. Trellix recommends that you use this feature only when network configuration does not allow the Sensor to be placed in locations where it could see all traffic.