Introduction
IPS supports HTTP2 inspection for the following scenarios:
HTTP2 Prior Knowledge
HTTP2 over TLS
Note
HTTP2 upgrade (h2c) scenario is not supported.
When you install/upgrade the Manager, by default, HTTP2 traffic inspection is not enabled.
Enable HTTP2 traffic inspection from the Manager
You can enable HTTP2 traffic inspection at both Global and Devices level in the Manager.
To enable HTTP2 traffic inspection at Global level, go to Devices → <Admin Domain Name> → Global → IPS Device Settings → Advanced Device Settings and select Enable HTTP2 Traffic.
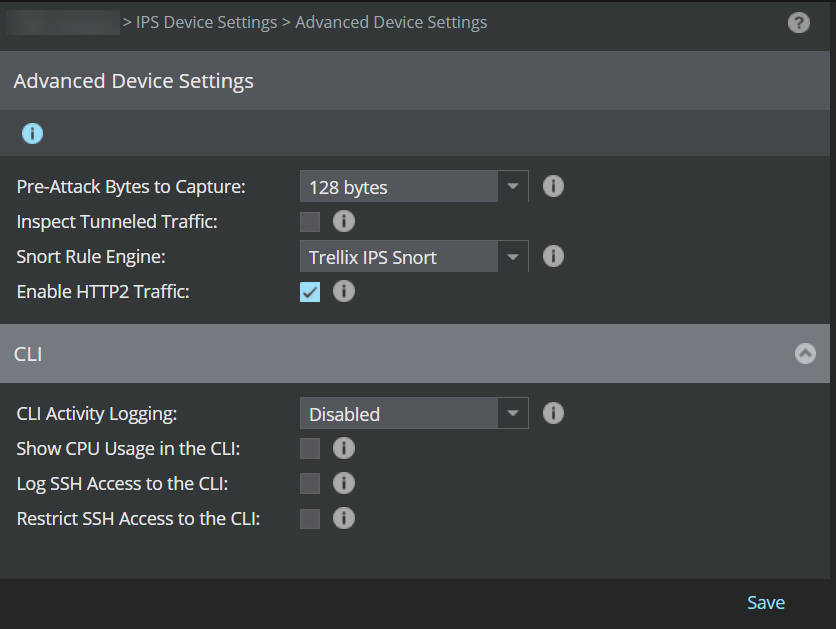
To enable HTTP2 traffic inspection at Devices level, go to Devices → <Admin Domain Name> → Devices → <Device Name> → Setup → Advanced → Advanced Device Settings and select Enable HTTP2 Traffic.
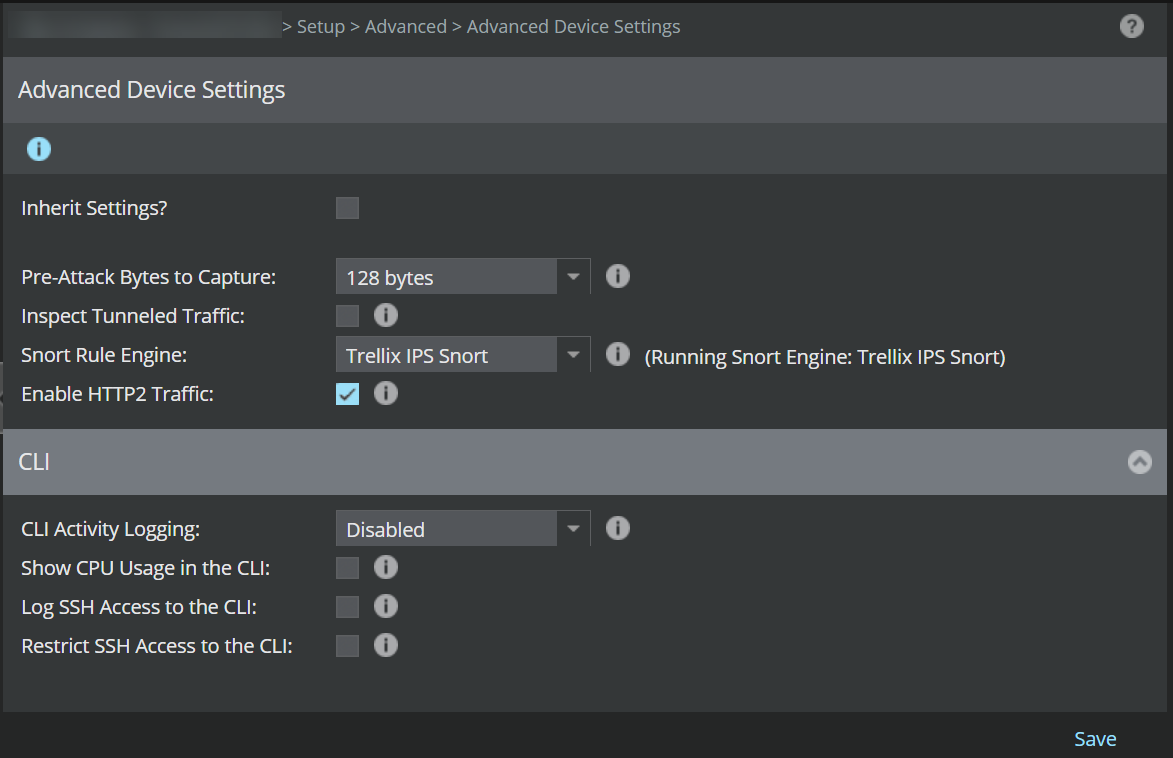
Note
By default, Enable HTTP2 Traffic is disabled.
After enabling the HTTP2 traffic inspection from Devices tab, follow the below steps:
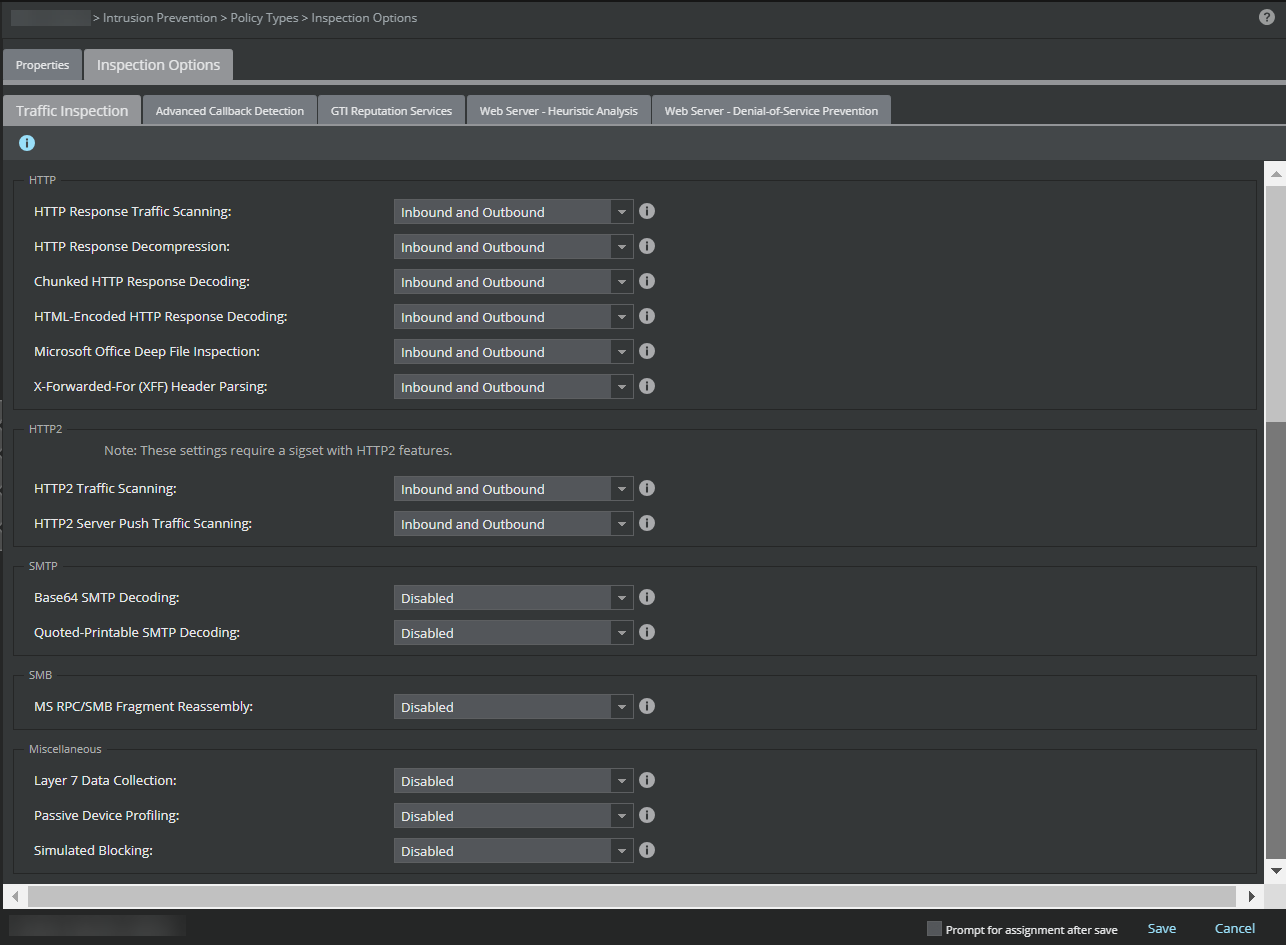
Go to Policy → <Admin Domain Name> → Intrusion Prevention → Policy Types → Inspection Options.
Navigate to Inspection Options tab and click Traffic Inspection tab.
Configure HTTP Response Traffic Scanning based on your requirement.
Go to HTTP2 section, configure HTTP2 Traffic Scanning and HTTP2 Server Push Traffic Scanning based on your requirement.
Click Save.
Notes:
The Sensor requires a reboot when you enable or disable HTTP2 Traffic Scanning. You can check the Sensor reboot status from Device Manager or
statusCLI.HTTP2 Traffic Scanning can be enabled only when HTTP Response Traffic Scanning is enabled.
HTTP2 Server Push Traffic Scanning can be enabled only when HTTP2 Traffic Scanning is enabled.
HTTP2 traffic inspection requires a sigset with HTTP2 features.
Only NS9600, NS9500, NS7600, NS7500, and NS3600 Sensors support HTTP2 traffic inspection.
From 11.1.5.122, HTTP2 traffic inspection with TLS and proxy-based SSL decryption is supported.
HTTP2 performance numbers align with HTTP 1.1 for supported Sensor models.
HTTP2 Protocol settings
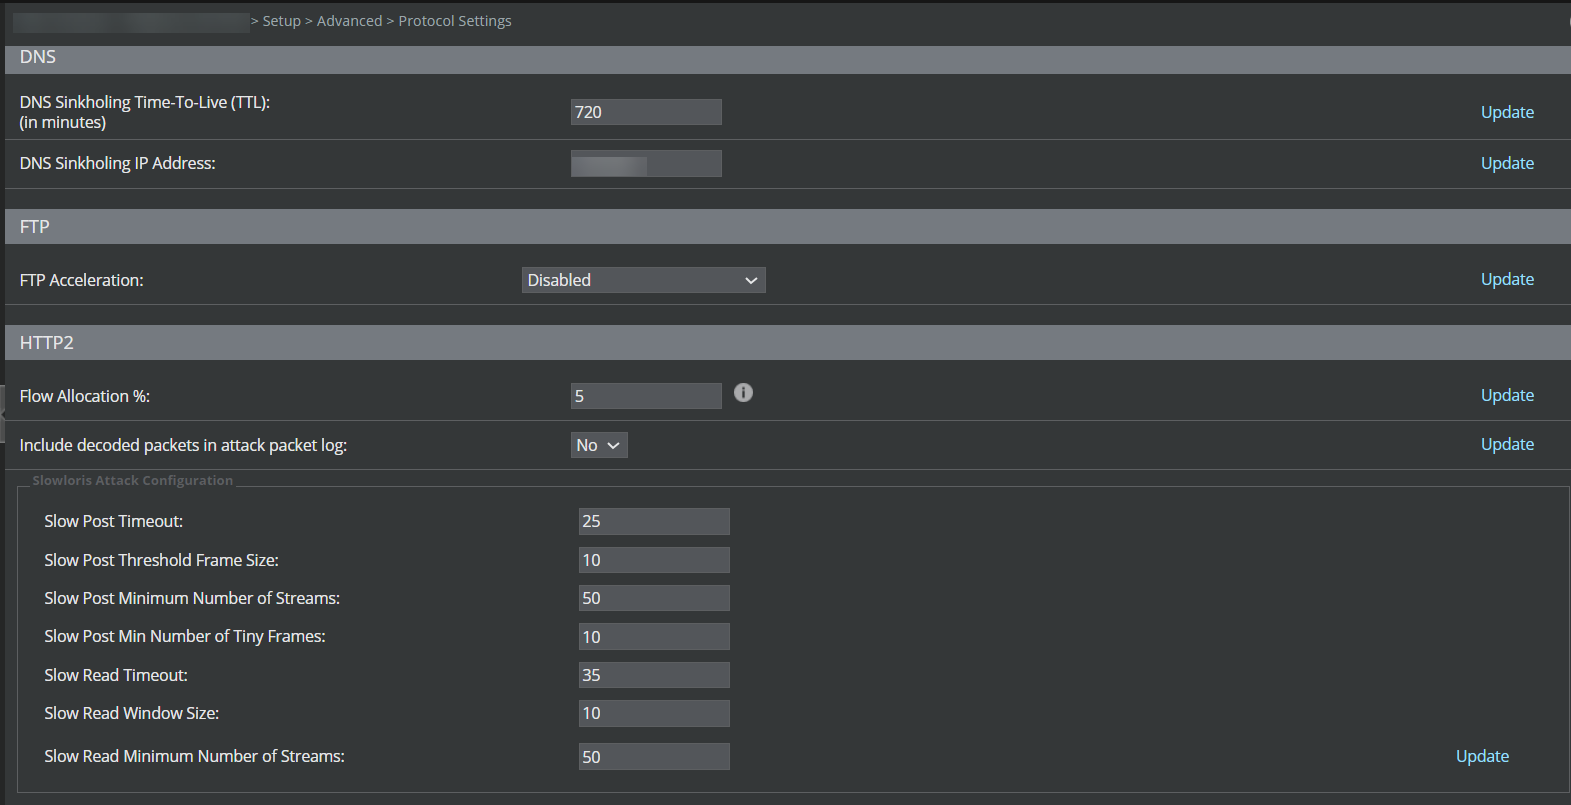
You can configure the HTTP2 protocol settings for any required Sensor from Devices → <Admin Domain Name> → Devices → <Device Name> → Setup → Advanced → Protocol Settings. Go to HTTP2 section, and configure the following:
Parameters | Description |
|---|---|
Flow Allocation % | Set the maximum HTTP2 flows as a percentage of total supported flows. Flow allocation differs for each Sensor model. For NS3600, NS7500, NS7600, NS9500 and NS9600 Sensors the min and max flow allocation are as follows:
After configuring, click Update to apply the changes.
|
Include decoded packets in attack packet log | While inspecting HTTP2 traffic, the Sensor decodes the HTTP2 packets/frames into HTTP requests/responses. By enabling this, the Manager will include decoded HTTP requests/responses along with HTTP2 packets/frames in the attack packet log. After configuring, click Update to apply the changes. |
Slowloris Attack Configuration | Allows you to configure the values for the following parameters:
|
Alert enhancements for HTTP2
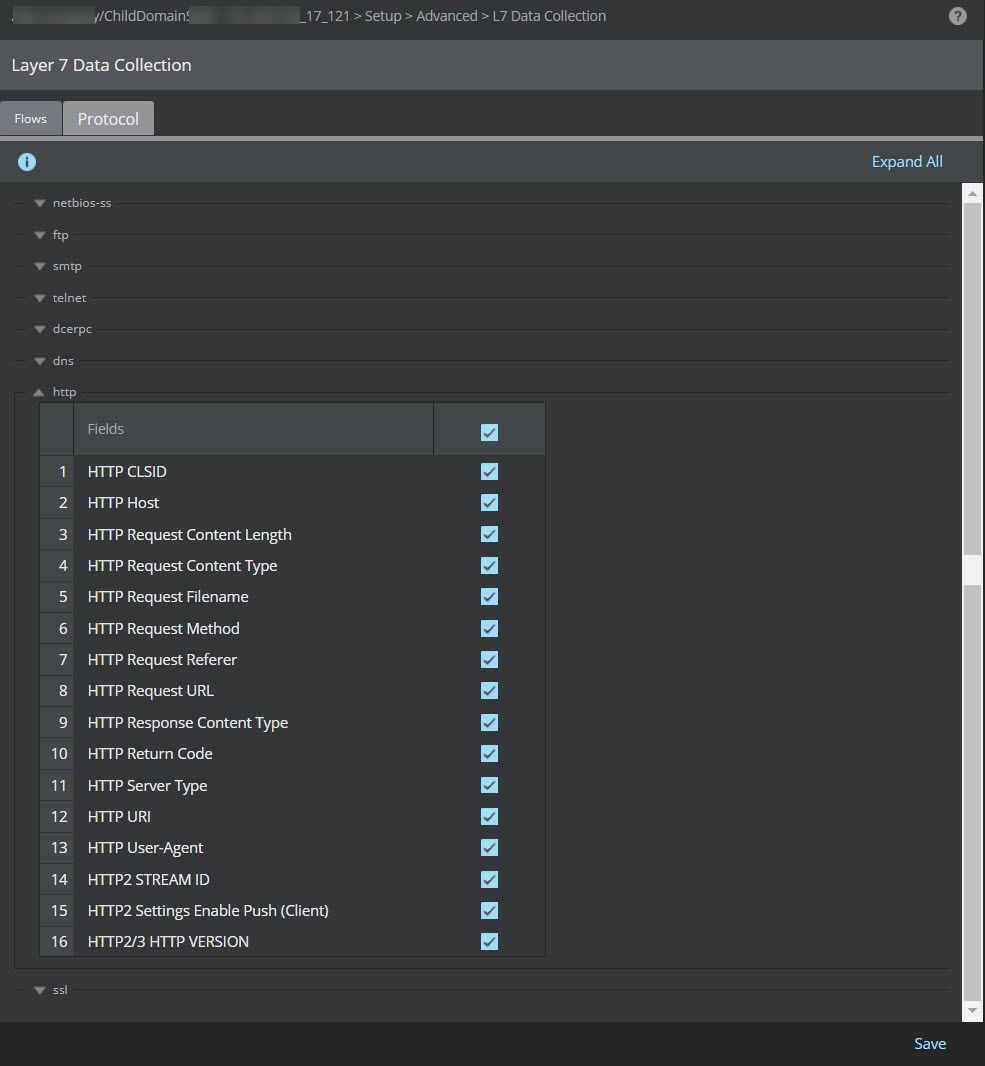
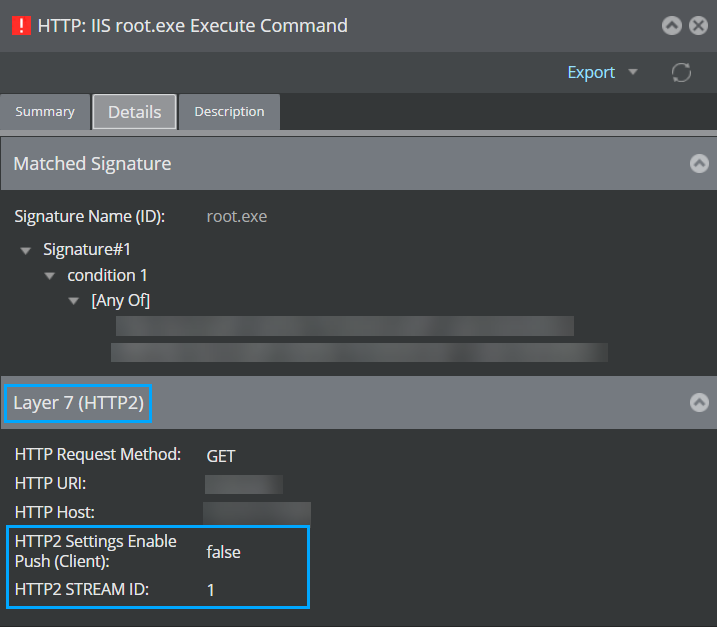
The following new alert fields are included in Layer 7 data:
HTTP2_STREAM_ID
HTTP2_SETTINGS_ENABLE_PUSH
HTTP2/3_HTTP_VERSION
You can customize the alert fields from Devices → <Admin Domain Name> → Devices → <Device Name> → Setup → Advanced → L7 Data Collection.
Note
HTTP2/3 HTTP VERSION is always enabled.
Filter HTTP2 alerts
You can filter HTTP2 alerts through the Attack Log or Reports page in the Manager.
Attack Log
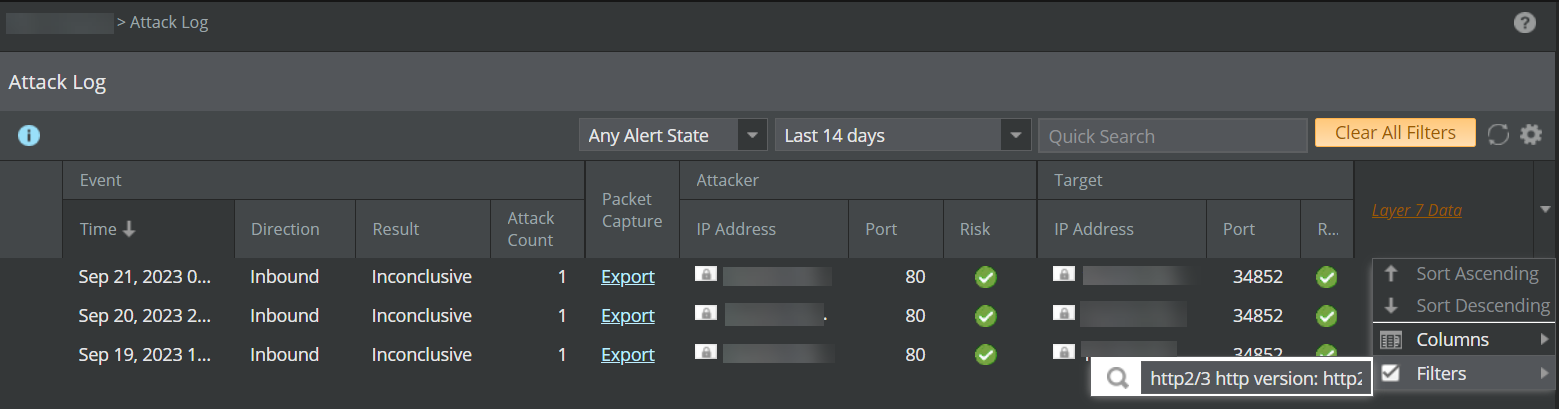
To focus on attacks detected on HTTP2 traffic, you can apply the filter in the Attack Log. To apply the filter, select Filters from Layer 7 Data column drop-down and in the search field, enter HTTP2/3 HTTP VERSION: HTTP2.
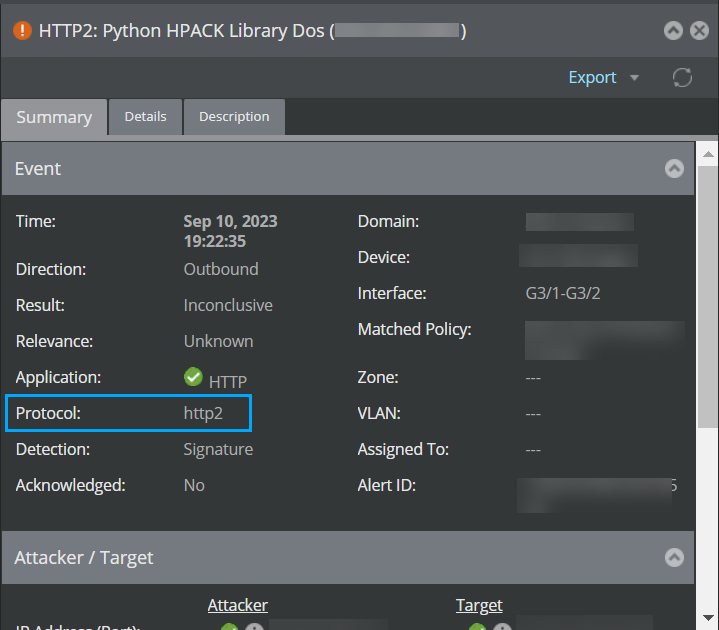
For a particular alert, you can differentiate the HTTP2 alerts by verifying the Protocol data in Summary tab of Details panel in Attack Log page.
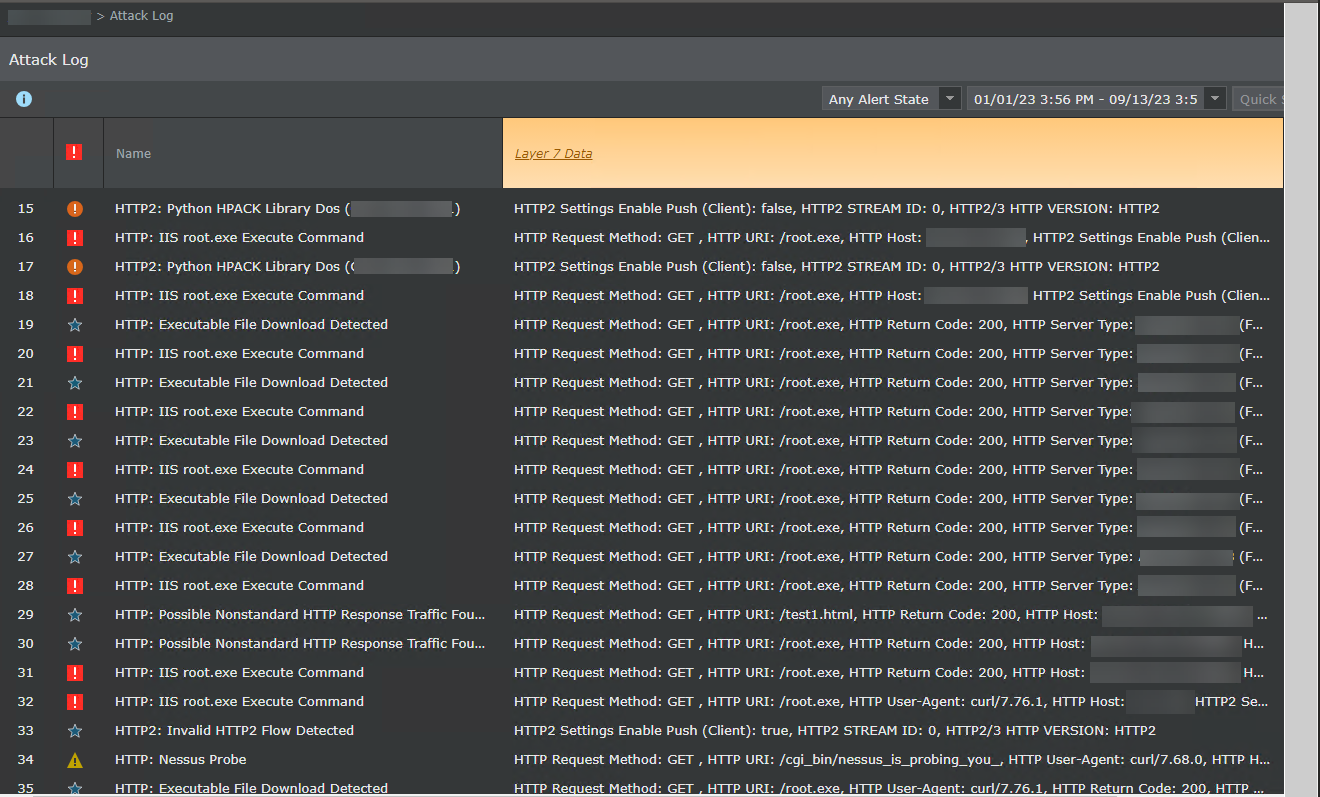
You can also verify the HTTP2 alerts through the Layer 7 section in Details tab of Details panel in Attack Log page.
Reports
You can follow the below steps to create HTTP2 reports:
Go to Analysis → <Admin Domain Name> → Event Reporting → Custom Reports.
In the Custom Reports page, select New.
Select the type of data as Alert Data and click Next.
Specify the required display and click Next.
Specify the required fields and click Next.
Select Protocol and set the property value to be equal to HTTP2 and click Next.
Configure the Date Options and Report Format.
Click Run.
Supported features with HTTP2
In this release, IPS supports following HTTP2 attack categories:
Attack content in a single HTTP2 stream
Attack content across multiple HTTP2 stream
HTTP2 protocol compliance attacks
HTTP2 DoS attacks
Unsupported features with HTTP2
In this release, the following features are not supported over HTTP2 connections:
Malware scanning
URL Reputation
Application Identification
SSL (Known Key, Agent)
Mandate Authentication/HTTP Redirection
Layer 7 Distributed DoS
Trellix Snort Rules
Botnet detection over HTTP
Connection limiting
X-Forwarded-For Header Parsing (XFF)
Decompression (Gzip, Deflate) and Decoding (Chunk, HTML)
Shell Code Detection
Firewall
File Reputation
Web Security
IPS Quarantine