If you had exported any Trellix IPS Custom Attacks, you can import it back into the Manager. Note that this should be the same ZIP file that was created at the time of export. If this ZIP file contains any Snort Custom Attacks, those are imported as well. This feature enables you to import custom attack definitions created on a different Manager as well as the Trellix IPS-defined custom attacks.
Note
When you import the ZIP file containing the exported attack definitions, only the attacks not present in the Manager are imported.
To import the previously exported Trellix IPS Custom Attacks, perform the following steps:
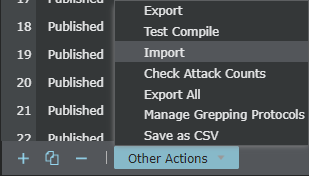
In the Custom Attack Editor, go to Other Actions → Import.
Browse to the location of your saved Trellix IPS Custom Attack ZIP file.
Click Open.
The imported attacks are listed in a new tab in the Custom Attack Editor. If the ZIP contains Snort Custom Attacks, those two types of attacks are listed on separate tabs.
If you are importing Native Custom Attacks:
Select Import Native Trellix IPS Attacks.
Import Native Trellix IPS Attacks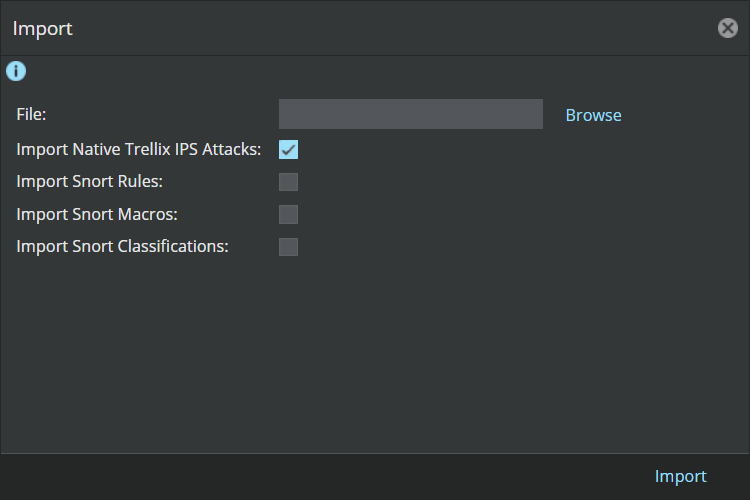
Deselect Import Snort Rules.
Deselect Import Snort Macros.
Deselect Import Snort Classification.
Click Import.
If you are importing Snort Rules:
Deselect Import Native Trellix IPS Attacks.
Select Import Snort Rules.
Import Snort Rules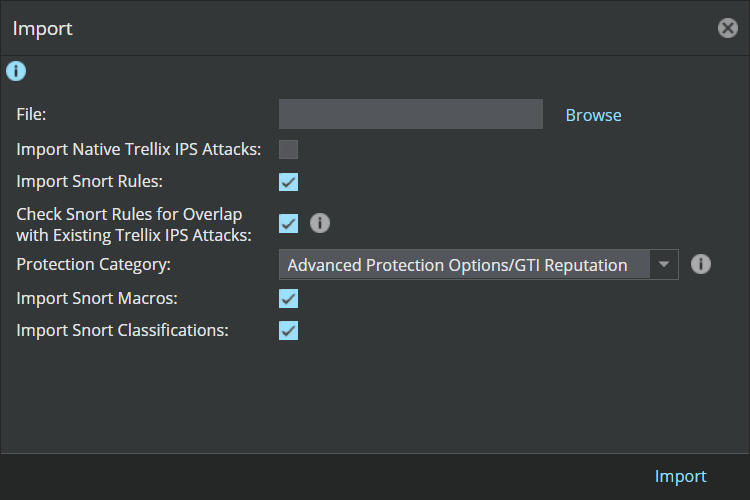
Select Check For Overlaps With Existing Trellix IPS Attacks.
Select a Protection Category value.
Select Import Snort Macros.
Select Import Snort Classification.
Click Import.
Verify if the attack is published in the policies.
Publish the attack with its signatures to the Sensors for attack detection.