Steps:
Go to Devices → <Admin Domain Name> → Global → IPS Device Settings → Advanced Device Settings. The default engine selected is Trellix IPS Snort.
To select the snort engine, click the Snort Rule Engine drop-down and select the Suricata Snort.
A pop-up appears asking you to confirm your changes and informing you that a reboot will be necessary for the change to take effect.
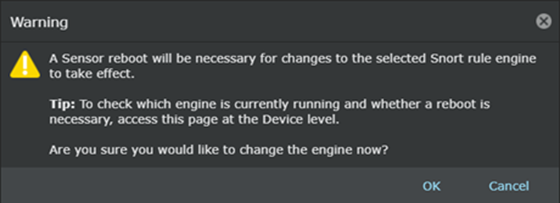
Click OK and then click Save at the bottom of the page.
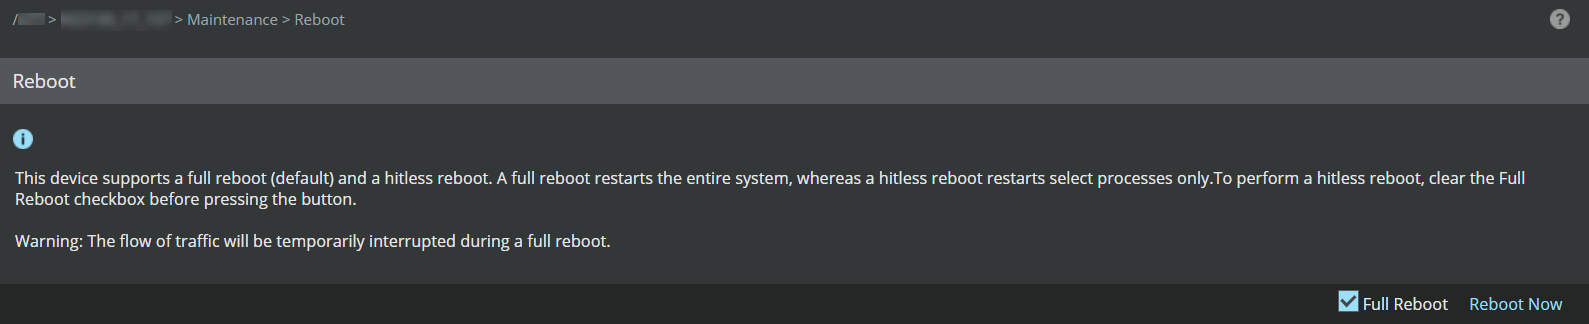
Reboot the Sensors which require this change. Go to Devices → <Admin Domain Name> → Devices. Select the device to reboot. Go to Maintenance → Reboot. Click Reboot Now
After the reboot, the Advanced Device Settings page of the Sensor displays Suricata Snort.
Go to Policy → <Admin Domain Name> → Intrusion Prevention → Policy Types → IPS. Click the Custom Attacks button (bottom left corner).
In the Custom Attack Editor, from the Snort Format tab, click Other Actions → Import
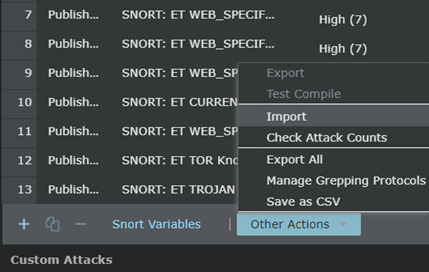
Browse to the location of the rules file to be imported and select the rules file.
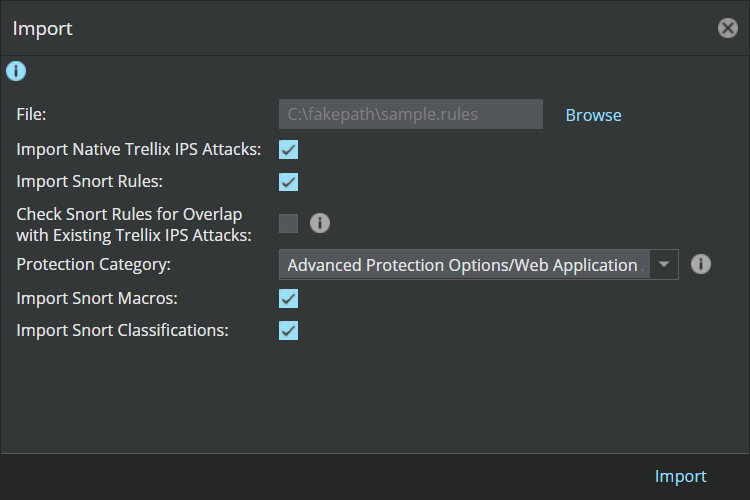
Select a Protection Category value.
The Protection Category indicates the intent of the attack and the intended target. The list of Protection Categories is pre-defined and is provided by Trellix Advanced Research Center. In this scenario, the selected value is Advanced Protection Option/File Reputation
Click Import
After the import, the Import Results screen is displayed.
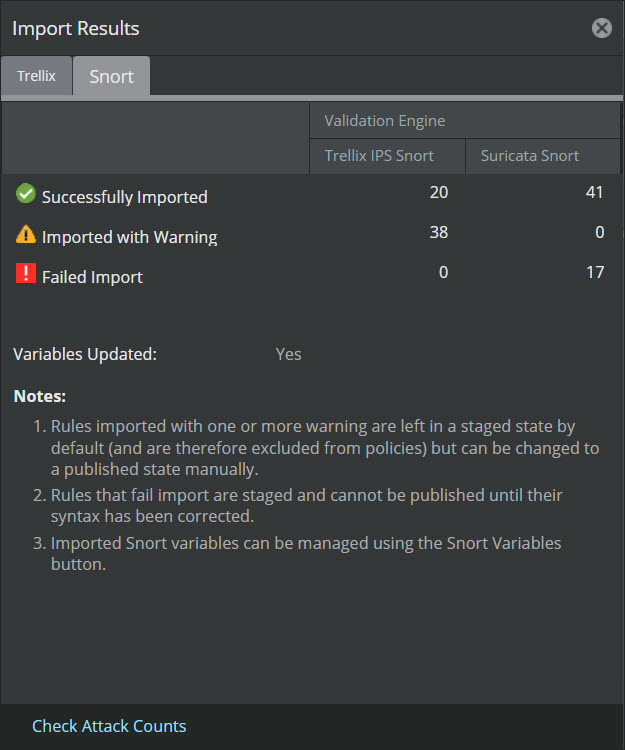
Close the Import Results screen.
View the imported Snort rules.
Know which rules converted successfully, which converted with warnings, and which failed to convert. For more information, see Viewing the imported Snort rules.
View the imported Snort variables.
Know which variables were imported and their classification type. For more information, see Viewing the Snort variables.
Verify if the attacks in Published state are actually published in the policies.
From the Resource Tree, select Policy → <Admin Domain Name> → Intrusion Prevention → Policy Types → IPS .
Double-click one of the All Inclusive policies; for example, you can open the Default Testing policy.
Click Attack Definitions tab.
Sort the attacks based on Name and verify if the Snort rules are published.
Note
You can also create your own attack set profiles to define the exact environment resources you want to protect. For more information, see the Trellix Intrusion Prevention System Product Guide.
Go to Devices → <Admin Domain Name> → Global → Device Manager.
Select the devices on which you want to deploy the imported rules by selecting the check boxes. Click Sync.
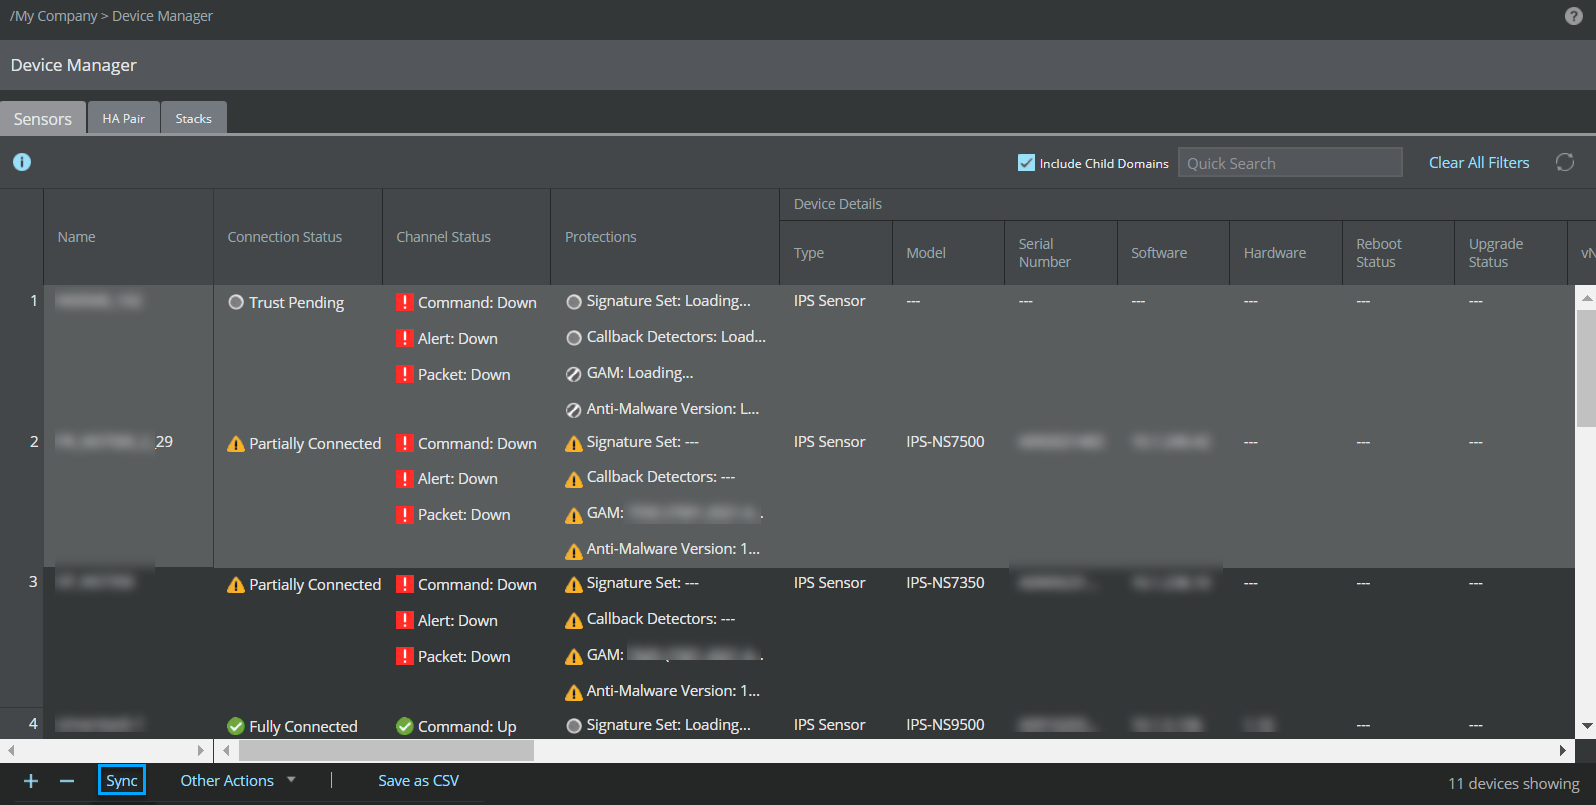
The Bulk Sync window is displayed.
Select Configuration & Signature Set from the window, and click Sync.
This deploys the IPS policies that contain the new Snort rules to the selected Sensors.