Installing Sensors at this point may seem premature. After all, you will no doubt perform tests once the HA pair has been configured. The logic here is to confirm connectivity and proper scanning with as few variables as possible. If basic connectivity and scanning prove to be fine now, but fail after configuring the HA pair, you at least know the issue is specific to the HA pair.
During Sensor boot up, there is a small time difference between when an inline fail-open port pair is enabled (port status LED is green) and actually put inline (activity LED starts blinking). This causes a minor traffic loss.
Ideally, you should test each Sensor individually. This includes, if need be, manually failing over the Primary path, so traffic will flow across the Secondary path.
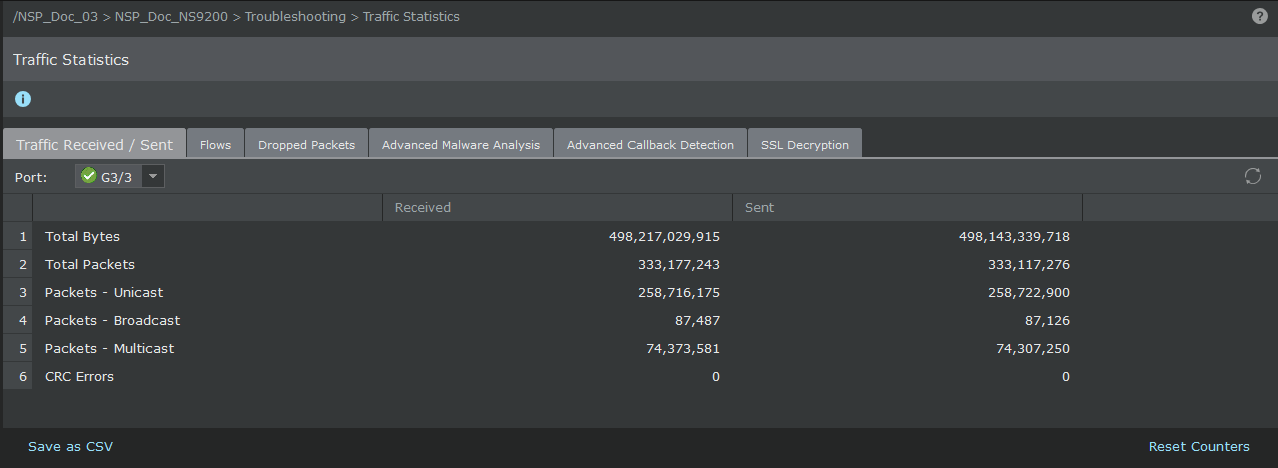
You can use common utilities like Ping and Traceroute (tracert.exe on Windows) to test basic connectivity. You can also look at the statistics from the Traffic Statistics page for each Sensor port to confirm that traffic is properly flowing through it.
Note
For step-by-step procedures on verifying how to verify traffic is flowing through the Sensor, see the Trellix Intrusion Prevention System Product Guide.
An easy and benign way to confirm that Trellix IPS is scanning for exploits is to trigger a FTP directory traversal signature.
The "attack" looks as follows:
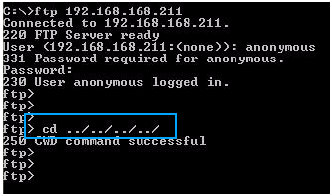
The highlighted section is the command that actually trips the signature.
If you are interested in HTTP tests, you can instead try the following URLs from your favorite browser:
http://serveraddress/inetpub/scripts/root.exe
http://serveraddress/inetpub/scripts/cmd.exe
Note
These exploits are specific to IIS.
Caution
These URLs are synonymous with Code Red and Nimda exploits, so they may trigger anti-virus software on the web server as well.
Caution
Use these tools for Trellix IPS testing purposes only. Trellix in no way condones use of attack traffic for any reason other than testing product connectivity and communication.