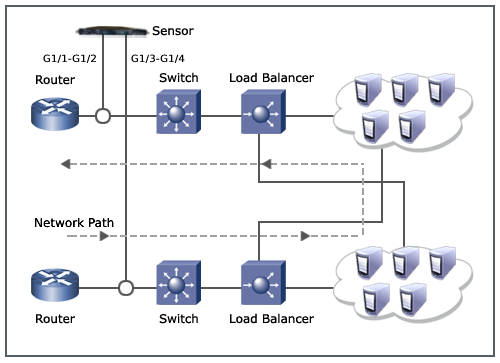
An interface group, also known as port clustering in networking parlance, combines the traffic processed on separate Sensor interfaces—or, in the case of a HA pair, on separate Sensors—into a single logical interface for state and intrusion analysis. Asymmetric routing is a good example of where an interface group is recommended. In asymmetric routing, a TCP connection does not always send and receive along the same network path. Therefore, a single-interface Sensor monitoring this transmission may only see the traffic received, not the traffic sent in response; thus not seeing all data from a transmission.
Sensors' multiple interfaces make the monitoring of asymmetric traffic possible. For example, consider an NS9500's G1 interface module that has 4 ports. The ports are wired in pairs by default. Peer ports G1/1 and G1/2 can monitor one direction of an asymmetric transmission, while peer ports G1/3 and G1/4 can monitor the other direction. By making an interface group of G1/1-G1/2 and G1/3-G1/4, the Sensor is able to see all the traffic for all sessions in the asymmetrically routed network and still is able to maintain state and accurately detect all attacks.