To access the Edit Snort Attack interface, click a Snort Custom Attack .
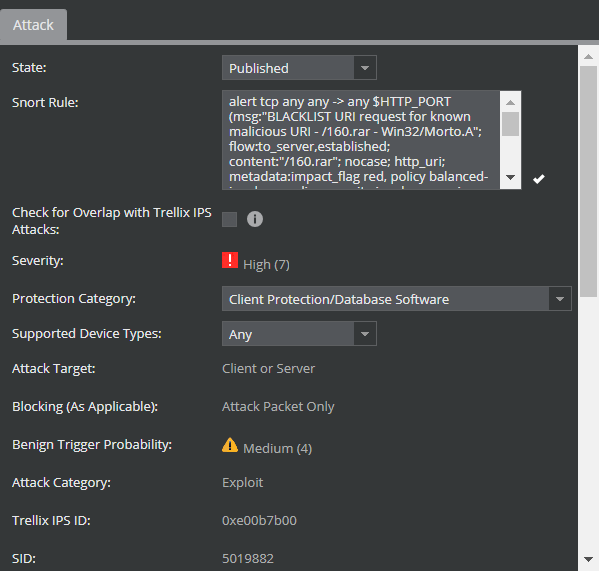
When you create a Snort rule in the Manager, based on the elements of the rule, the Manager assigns values to some of the fields. If you modify the rule in the Raw Snort Rule Text section, the Manager modifies the field values accordingly. For example, if you change the msg in the rule, the attack and signature names also change because the Manager assigns the attack and rule names as per the msg keyword in the rule.
Note
Every time you modify the rule in the Raw Snort Rule Text section, you need to check if the rule is conforming to Snort rules syntax by clicking
. After the Manager translates the rule to Trellix IPS's format, click Save to save the changes in the Manager client. The changes are saved in the Manager server only when you click Save in the Custom Attack Editor.
The following the fields displayed on the General tab for a Snort Custom Attack:
Option | Definition |
|---|---|
Editable Fields | |
State | Select the state of the custom attack. the choices are Published and Staged.
|
Snort Rule | You can modify the rule in this section. |
Check for Overlap with Trellix IPS Attacks | Verifies if the rule matches an existing Trellix IPS attack definition. If the rule matches then the Snort Rule will be Staged. |
Protection Category | Displays the Protection Category assigned to the attack. The Protection Category indicates the intent of the attack and the intended target. The list of Protection Categories is pre-defined and provided by Trellix Advanced Research Center. You cannot modify it. This list is updated when you update the Signature Set. |
Attack Target | Indicates the target that is being exploited |
Supported Device Types | You can apply a Snort Custom Attack signature for just the NS-series Sensors or Virtual IPS Sensors, or for both of them. The value for this field depends on what you select for the corresponding rule. You cannot edit this field at the attack level, but the Manager modifies it accordingly when you change it for the corresponding rule. By default, you can apply up to 5000 per NS-series and Virtual IPS Sensors. |
Non-editable Fields | |
Severity | This priority is derived from the classtype or the priority tag. |
Attack Target | This column indicates the target that is being exploited. |
Blocking (As Applicable) | In case of Snort Custom Attacks, the Sensor drops just the packet that matches the rule. You cannot edit this field. |
Benign Trigger Probability | This is an indication of the probability that the Snort Custom Attack will alert on traffic that may not be an attack. The default value is Medium. |
Attack Category | This column indicates the type of attack. |
Trellix IPS ID | The numeric ID assigned for the attack by the Manager for database archival. The Manager assigns the ID after you save it in the Manager server. For Snort Custom Attacks, the IDs begin with 0xe. For Snort Custom Attacks created in the Central Manager, the IDs begin with 0xee. |
SID | Snort rule ID (SID) is the ID assigned to a Snort rule by you or the party that provided the rule. The Snort attack definitions that you want to save in the Trellix IPS database must have a unique SID. Make sure that the SIDs of the attacks that you are writing or importing have not been used by the definitions that are already in the database. For attack definitions that failed to import, SID is set to -1. |
Trellix IPS Snort Engine | The Validation field displays status of attack validation from the Trellix IPS Snort Engine. The Test Compile field displays the status of test compilation. |
Suricata Snort Engine | The Validation field displays status of attack validation from the Suricata Snort Engine. |
Last Updated | This is the time stamp when a rule was imported or modified. |
To access the Bulk Edit Snort Rules interface, select multiple snort rules by pressing the Ctrl key.
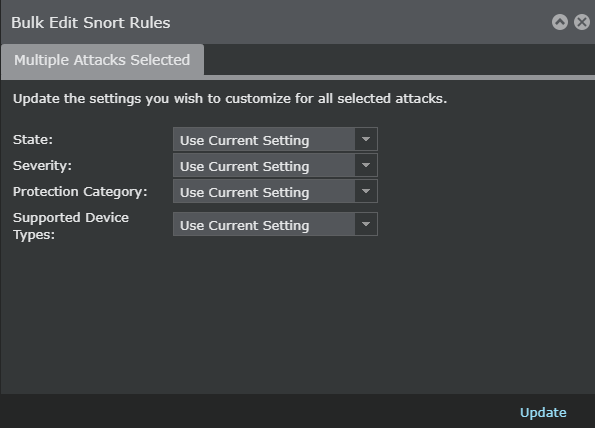
The following the fields displayed on the General tab for a Snort Custom Attack:
Option | Definition |
|---|---|
State | This column indicates whether a custom attack is published in the Trellix IPS policies. This column can have one of the following values:
|
Severity | Select a severity from the drop-down list. This column can have one of the following values:
|
Protection Category | You must choose a Protection Category from the available options. The Protection Category indicates the intent of the attack and the intended target. For example, you can choose Client Protection/Operating Systems for an attack targeting vulnerabilities in client operating systems. In this example, Client Protection is the category and Operating Systems is a subcategory. The list of Protection Categories is pre-defined and is provided by Trellix ARC. You cannot modify it. This list is updated when you update the Signature Set. |
Supported Device Types | You can apply a Snort Custom Attack signature for just NS-series Sensors or Virtual IPS Sensors, or for both of them. The value for this field depends on what you select for the corresponding rule. By default, you can apply up to 5000 Snort signatures per NS-series Sensors and Virtual IPS Sensors. This column can have one of the following values:
|