The Gateway Load Balancer (GWLB) enables you to deploy, scale, and manage virtual appliances, such as firewall, intrusion prevention systems, and deep packet inspection systems. It combines a transparent network gateway (i.e., a single entry and exit point for all traffic) and distributes traffic while scaling your Trellix vIPS appliances with the demand.
GWLB listens for all IP packets across all ports and forwards traffic to the target group that's specified in the listener rule. It maintains stickiness of flows to a specific target appliance using 5-tuple (default) or 3-tuple (customized). The GWLB and its registered Trellix vIPS instances exchange application traffic using the GENEVE protocol on UDP port 6081.
GWLB uses Gateway Load Balancer endpoint (GWLBe) to securely exchange traffic across VPC boundaries. A GWLBe is a VPC endpoint that provides private connectivity between Trellix vIPS VPC in the service provider VPC and application servers in the workload VPC. You can deploy the GWLB in the same VPC as the Trellix vIPS appliances. You must register the Trellix vIPS appliances with a target group for the GWLB.
Traffic flows from the service consumer VPC over the GWLBe to the GWLB in the service provider VPC, and then returns to the service consumer VPC. You must create the GWLBe and the application servers in different subnets. This enables you to configure the GWLBe as the next hop in the route table for the application subnet.
For more information, refer to Access virtual appliances through AWS PrivateLink.
How does GWLB work?
A GWLB is connected to GWLBe in another VPC. GWLBe is a type of VPC Endpoint (VPCE). One GWLB can be connected to many GWLBe.
GWLB has two sides. The side that connects to GWBLE is called GWLB Frontend. The side that is connected to Trellix vIPS appliances is called GWLB Backend. In the backend, GWLB operates as a load-balancer for routing traffic flows through one out of multiple equivalent Trellix vIPS appliances. GWLB ensures stickiness of flows in both directions to Trellix vIPS appliances and also reroutes flows if the selected appliance becomes unhealthy.
Packets sent from source to destination do not contain the GWLB IP as the destination IP address, but they will be routed to GWLB due to route table configurations. To achieve transparent forwarding behavior (i.e., to keep the original packet contents), GWLB encapsulates the original packet using Geneve encapsulation and sends/receives packets to/from) appliances. Trellix vIPS appliances also need to decapsulate Geneve type-length-value (TLV) pairs to process original packet.
GWLB is a packet-in/packet-out service. It does not maintain any application states and does not perform TLS/SSL decryption/encryption. These functions are performed by the appliances themselves.
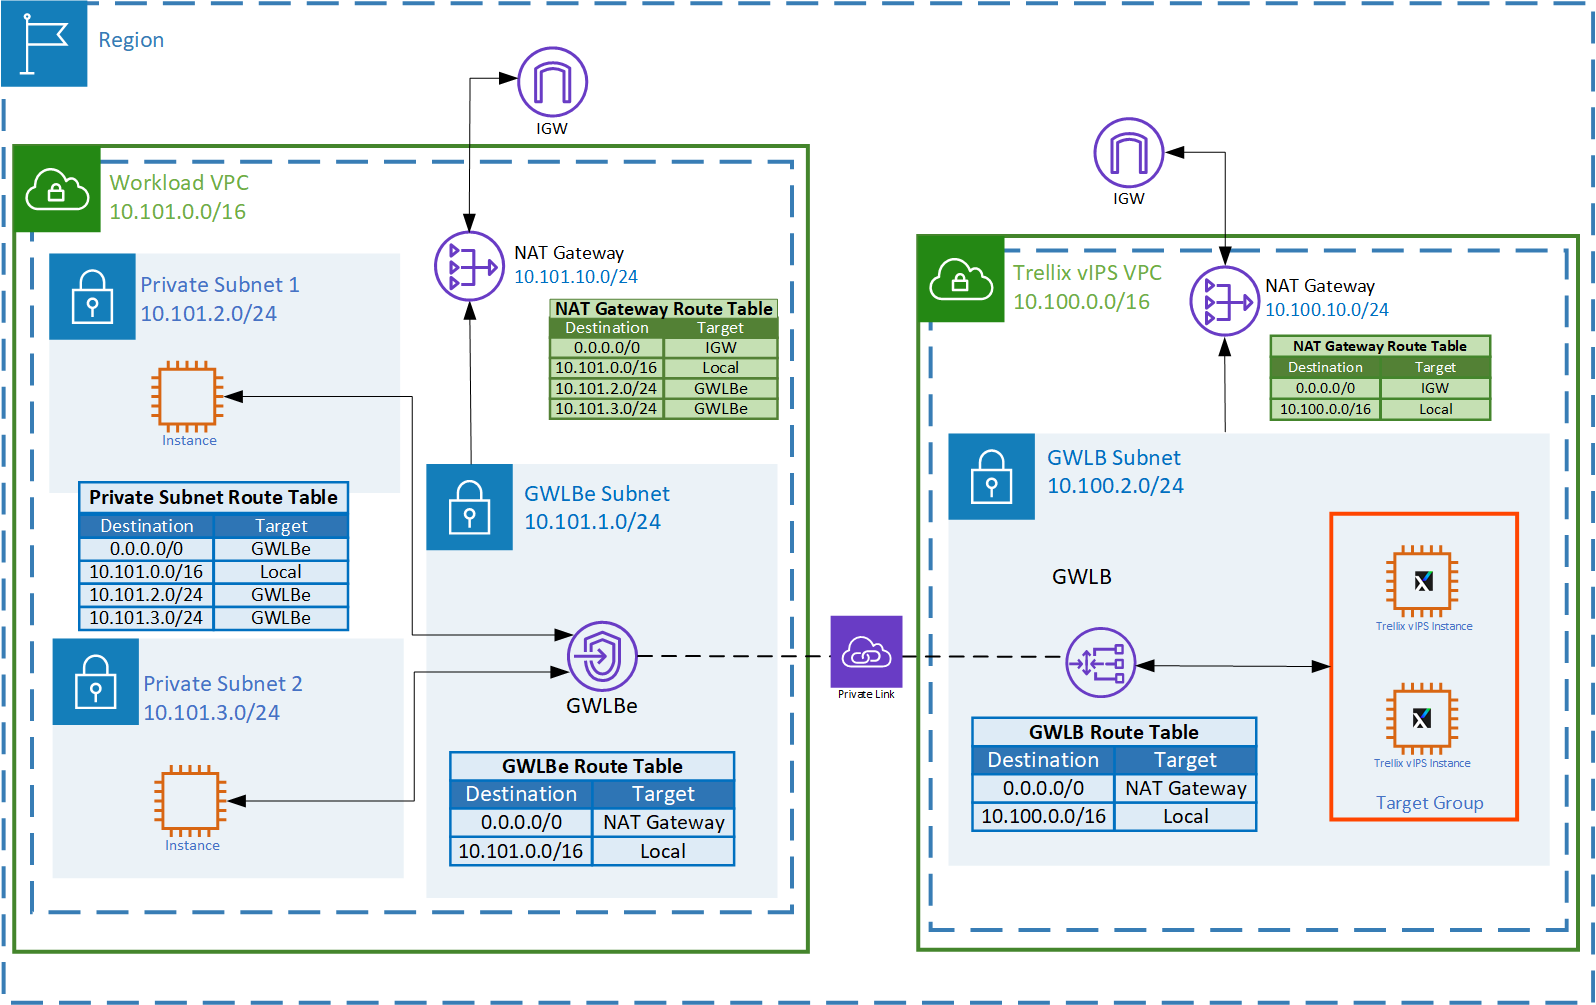
Key features of Gateway Load Balancer are as follows:
Scale your vIPS Sensor instances automatically
Bring higher availability to your Trellix vIPS appliances
Monitor continuous health and performance metrics
Ensure private connectivity over the AWS network using Gateway Load Balancer Endpoints