Trellix IPS provides protection from DoS attacks at various TCP/IP levels, including DoS protection at layer 3, connection-limiting policies at layer 4, and web server protection at layer 7.
A layer 7 DoS attack is difficult to detect when compared to DoS attacks at other layers because such an attack is often perpetrated through the use of an upsurge of HTTP requests, where the attacker looks like a legitimate connection, and is therefore passed on to the web server. There are multiple HTTP requests at the same time, and these legitimate HTTP requests are mixed in with the attack.
With the growth in bots, HTTP application-level DoS attacks have become more common and even more difficult to detect. bots can be programmed to launch DoS attacks against a particular domain or URL, and these requests appear as normal HTTP requests originating from a browser, thereby making it difficult to differentiate bot traffic from normal traffic.
Multiple types of DoS attacks range from attacking web server infrastructures to targeting a particular URL/path resulting in huge file downloads and slowing down the web servers. Since bot traffic pattern is different depending on the botnet technology and the attack classes, Trellix IPS aims at allowing users to customize different response actions based on configured thresholds.
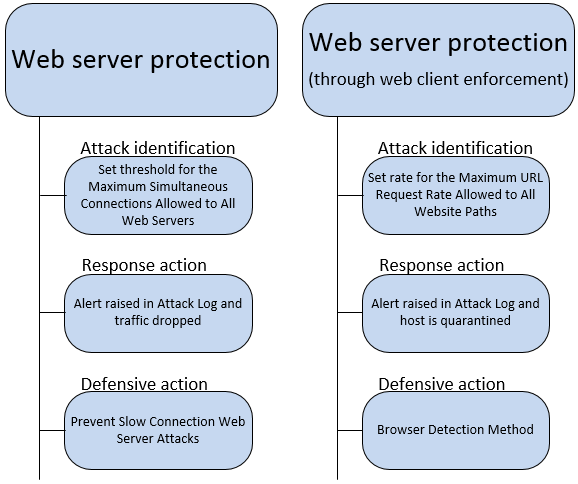
Defending against Layer 7 DoS attacks usually involves a mechanism to configure different HTTP response actions based on traffic volume anomaly. Trellix IPS deals with DoS attacks in layer 7 by employing the HTTP challenge-response approach based on the traffic volume anomaly with different threshold methods. A three-pronged protection approach is used consisting of attack identification, response action, and the defensive action.
You can view the status of L7 DoS using the show l7ddosstat command.
Using the Manager, the layer 7 DoS protection for web servers allows you to configure inspection options on the web server side as well as the web client side.
This feature is available on the following Sensor models:
NS9600 standalone, NS9500, NS9300, NS9200, and NS9100
NS7600, NS7500, NS7350, NS7250, and NS7150
NS7300, NS7200, and NS7100
NS5200 and NS5100
NS3600, NS3500, NS3200 and NS3100