After a new Sensor is installed, a policy is inherited from the admin domain and enforced on all Sensor interfaces. In large deployments or ones that have a significant number of policies configured in the Manager, it can take a long time to download the signature sets and apply the policy changes to the Sensors. You define policies at the admin domain level. This becomes your Baseline Policy. When two or more Sensor interfaces protect similar types of traffic, you can assign the same baseline policy to each of these interfaces, and optionally customize specific attack settings per interface, as required. This helps in minimizing scalability issues, and enhances the overall policy management process in the Manager. The baseline policy is assigned to the interface and now functions as a starting point for the local attack settings.
Each subinterface created within an interface can have a specific IPS policy applied. For example, if you have created three subinterfaces using VLAN tags, you can apply individual policies different from that of the parent interface to each of the three subinterfaces, respectively. When you create a subinterface, you can specify an IPS policy or simply inherit the IPS policy of the parent interface. This policy can be changed at any time per subinterface. The procedure to apply IPS policies to subinterfaces is similar to that of interface. However, note this important point regarding how the policies are enforced. If you apply a policy to a subinterface that is different than the inherited policy, the policy enforced at the interface level protects all traffic not specific to the subinterface. That is, the IPS policy of the subinterface exclusively protects all of the traffic that meets the criteria of the subinterface, which is typically any specified CIDR-based network or VLAN-tagged traffic flowing through the parent interface. All other traffic monitored by the interface is thus subject to the applied policy of the interface.
In the Manager, click Policy and then select the required Domain.
Go to Intrusion Prevention → Policy Manager.
The Policy Manager page is displayed.
Policy Manager page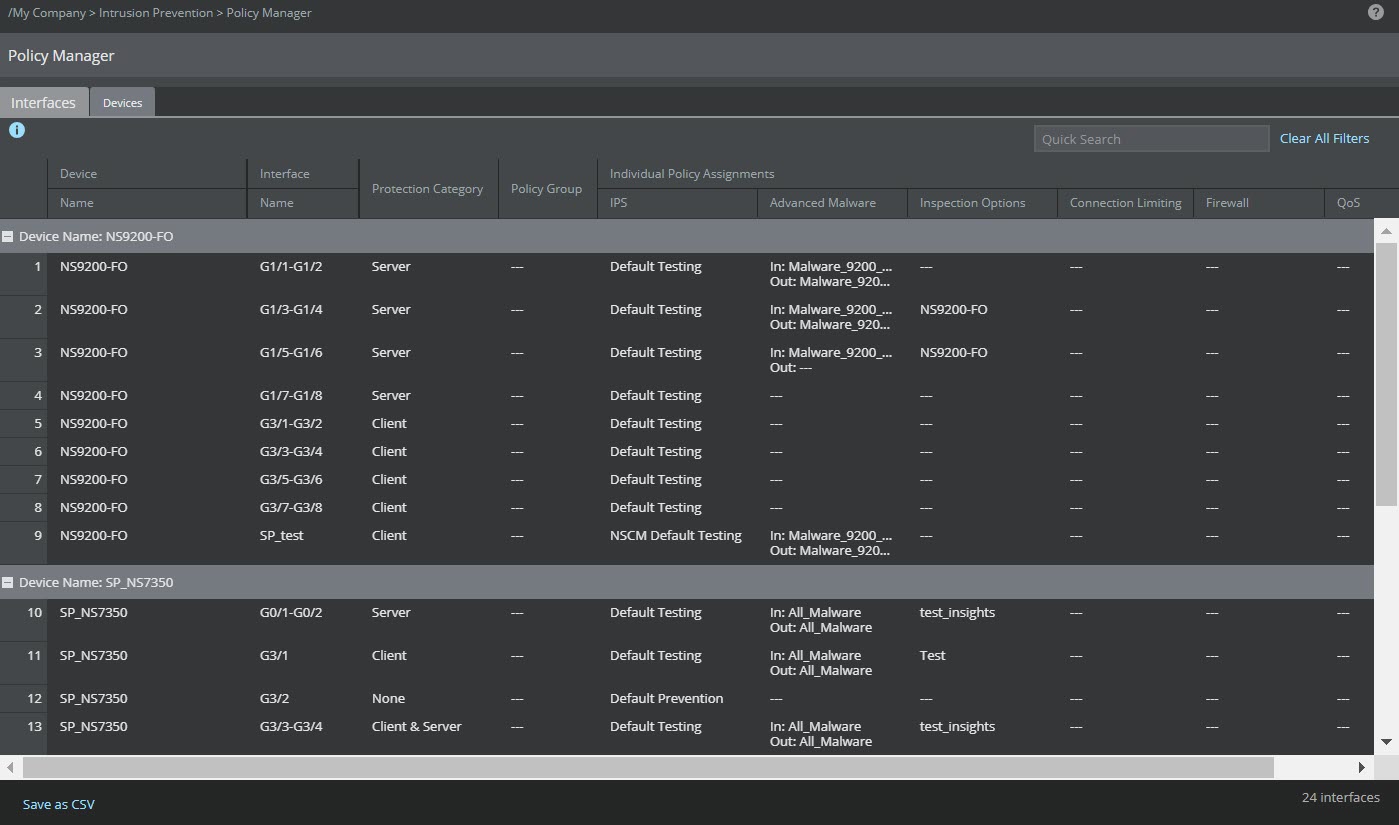
The Policy Manager page has the following tabs:
Interfaces tab
Devices tab