For managing the assignment of policies, a new page is created under Policy → Intrusion Prevention → Objects → Policy Groups.
In the Policy Groups page, you can create and manage a group of policies. After creating a policy group, it is assigned to the corresponding Sensor interfaces and sub-interfaces to manage the inbound and outbound traffic. The following columns are displayed in the Policy Groups page:
Name
Description
Individual Policy Assignments
Search
In the column header an option can be selected to sort based on ascending or descending order. The options are Sort Ascending and Sort Descending. The column based on which the list is sorted is indicated in the column header by an up arrow icon for ascending order and down arrow icon for descending order.
In the Policy Group page, a new policy group can be created by clicking on the Add button. It displays the Policy Group Details panel. The Policy Group Details panel has the following fields:
Name
Description
Owner Domain
Visibility
Editable here
IPS: Policy
Advanced Malware: Inbound Policy and Outbound Policy
Inspection Options: Policy
Connection Limiting: Policy
Firewall: Interface Policy
Quality of service: Inbound Policy and Outbound Policy
In the Assignments page, the assignments of policy groups are displayed:
Available Interfaces — Lists the interfaces and sub interfaces of the Sensors in the admin domain
Selected Interfaces — The policy group that is currently assigned to an interface
Search Interfaces — To filter the list of available interfaces, enter a string that is part of the Available Interfaces
You can create and manage policy groups and assign them to the corresponding Sensor interfaces and sub-interfaces to manage the inbound and outbound traffic.
To access and manage policy groups:
Click the Policy tab, and select the admin domain from the Domain drop-down list.
Select Intrusion Prevention → Objects → Policy Groups. The Policy Groups page is displayed.
Policy Groups page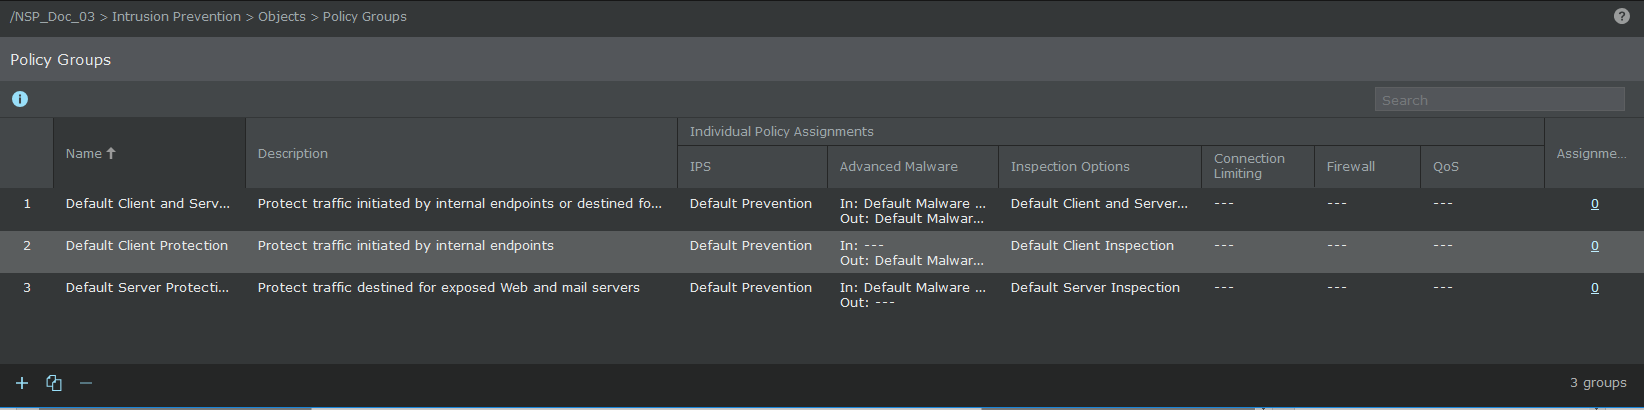
The Policy Groups page displays the following details :
Option
Definition
Name
Displays the name of the policy group
Description
Displays the description of the policy group
Individual Policy Assignments
IPS — Specifies the type of IPS policy. Example: Default Prevention.
Advanced Malware — Specifies the inbound and outbound type of advanced malware policy
Inspection Options — Specifies the type of Inspection Options policy
Connection Limiting — Specifies the type of connection limiting policy
Firewall — Specifies the type of Firewall policy
QoS — Specifies the type of inbound and outbound QoS policy
Ownership and Visibility
Owner Domain — Specifies the ownership of the domain
Visibility — Specifies the visibility level of the domain
Editable Here — The status Yes indicates that the policy is owned by the current admin domain.
Last Updated
Time — Displays the time when the firewall policy was last updated
By — Displays the user who modified the policy
Assignments
Indicates the number of Sensor resources to which the policy is assigned
Search
Type your search criteria in the field to find policy groups with matching elements.
 icon
Click here to create a policy group.
 icon
Clones a policy group
 icon
Deletes the selected policy group
To view or edit a policy group
Double-click the row of the specific policy group.
You can filter the display of columns by clicking a column header and selecting or unselecting the check-box for the list of columns you wish to view in the Policy Groups page.
Column filter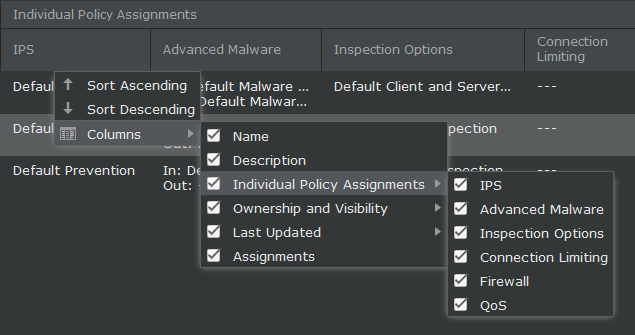
Click a column header and select the option to sort based on ascending or descending order. The options are Sort Ascending and Sort Descending.The column based on which the list is sorted is indicated in the column header by an up arrow icon for ascending order and down arrow icon for descending order.