A default Custom Report called Top 10 Malware Detections provides details of the detected malware. For a given time period, this report shows the alerts raised for the top 10 most frequently downloaded malware in your network. Therefore, for a given file, you can view the results from various malware engines. However, these results are dependent on the Advanced Malware policy configuration for the period of the report.
In the Manager, select Analysis → Event Reporting → Custom Reports.
From the list of Saved Reports, select Default - Top 10 Malware Detections and then click Run.
Specify the time period for which you want to generate the report in the Date Options section.
Select the output format of the report from the Report Format list.
Click Run.
The default Top 10 Malware Detections report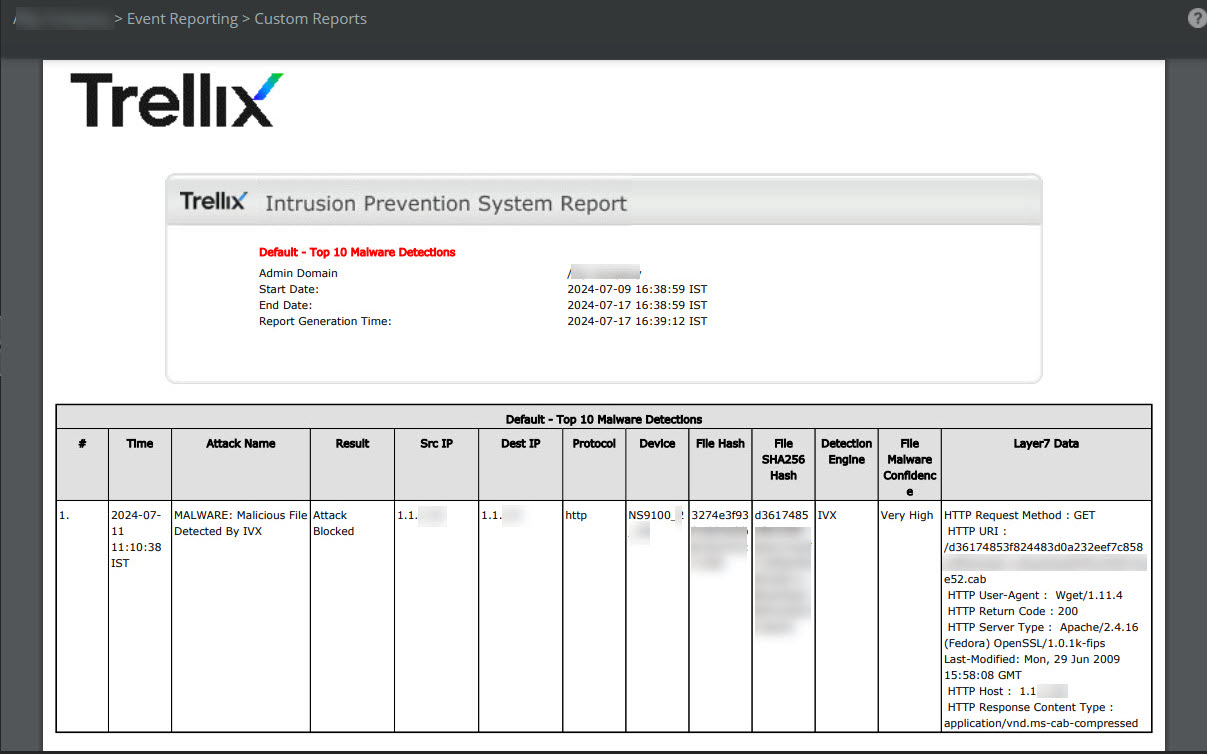
The generated report is displayed.
Column definitionsColumn
Definition
Time
The time stamp when a malware engine determined the file to be malicious
Attack Name
The alert raised by the Sensor for the file
Result
The response action taken by the Sensor for the file. For example, the Sensor could have blocked the file download.
Src IP
The source IP address as seen in the traffic for the malware traffic
Dest IP
The target host that is downloading the file
Protocol
The L7 protocol involved. This could be HTTP or SMTP.
Device
The Sensor that detected the file download
File Hash
The MD5 hash value of the file as calculated by the Sensor
Detection Engine
The malware engine that reported the malware
File Malware Confidence
The malware score reported by the malware engine
Layer7 Data
The L7 data associated with the file
Note
The admin domain filter on the main Analysis tab (provided in the left pane) has no impact on the reports generated. The admin domain filter criteria selected for the reports show data specific to the admin domain selected.
For information how to use the custom reports, see the section Custom reports in Trellix Intrusion Prevention System Product Guide.
You can also generate a Custom user defined report using all of the above columns. For example, you can generate a user defined report that reports only very-high severity malware detected by Sensors of a particular domain. You must use Alert Data as the Data Sourcewhen you define the report. For more information on how to generate a user defined report, see the section Generate Custom user defined reports in Trellix Intrusion Prevention System Product Guide.