The Manager and Sensor can also use a CA-signed certificate to establish trusted connection. By default, the Manager and Sensor use a self-signed certificate to establish trust. You can also use a CA-signed certificate chain issued by trusted CAs, such as Verisign, GeoTrust, and others, to establish trust between the Manager and the Sensor.
Note
- For non-certification, the CA-signed certificates can be assigned only when the Manager and Sensor are on version 10.1.
- For certification, the CA-signed certificates can be assigned when the Manager and the Sensor are on version 9.1 or later.
To manage the certificates for the Manager, go to Manager → <Root Admin Domain> → Setup → Certificates.
The Certificates page opens. It consists of following tabs:
- Trust Establishment
- GUI Certificate
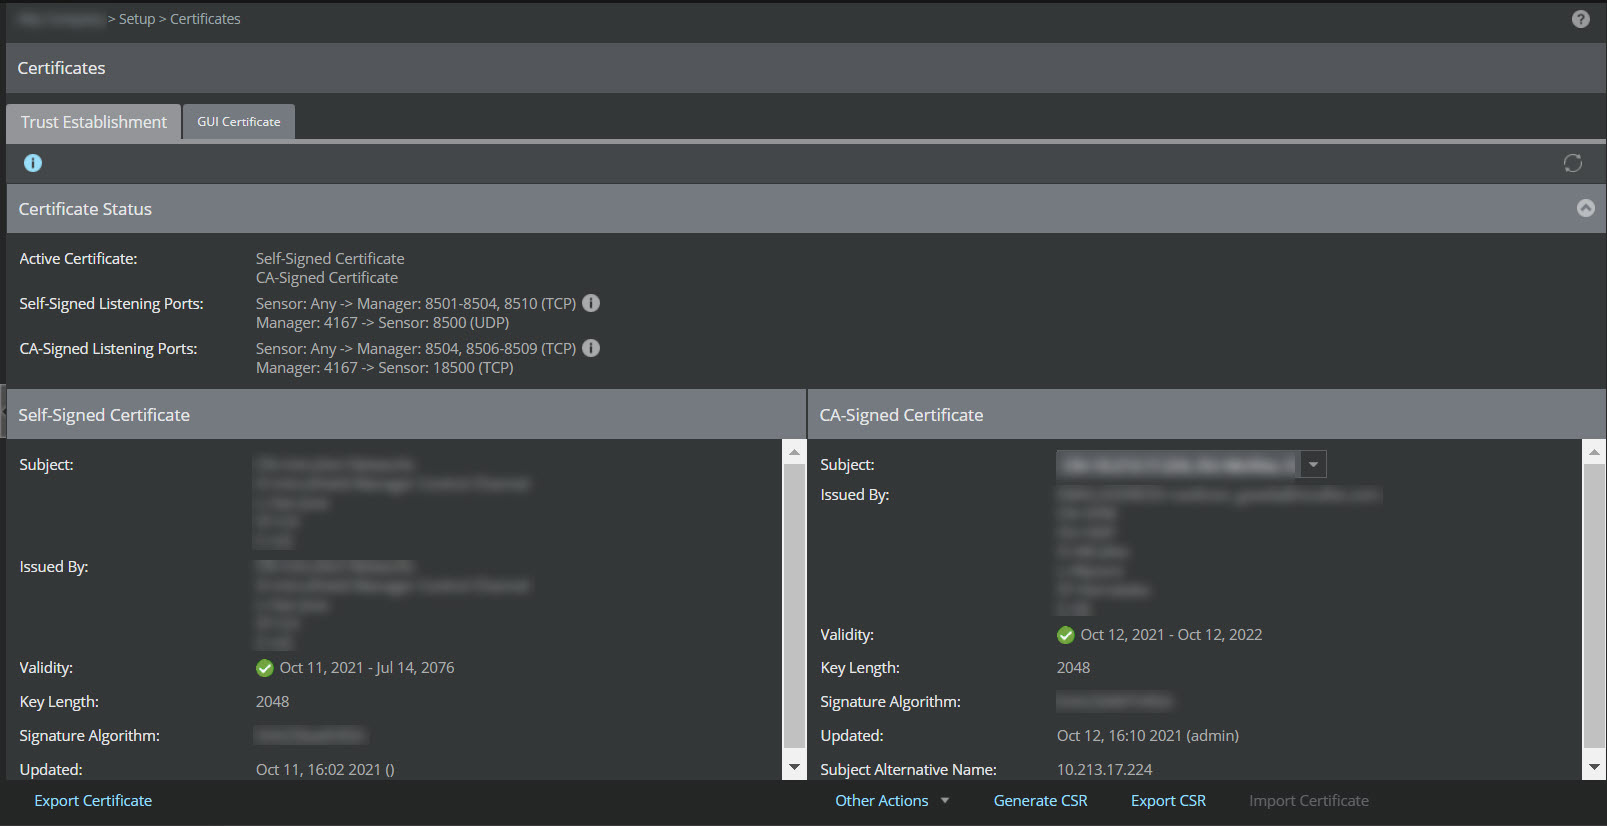
To manage the certificates for the Sensor, go to Devices → <Root Admin Domain> → Devices → <Device Name> → Setup → Trust Certificate.
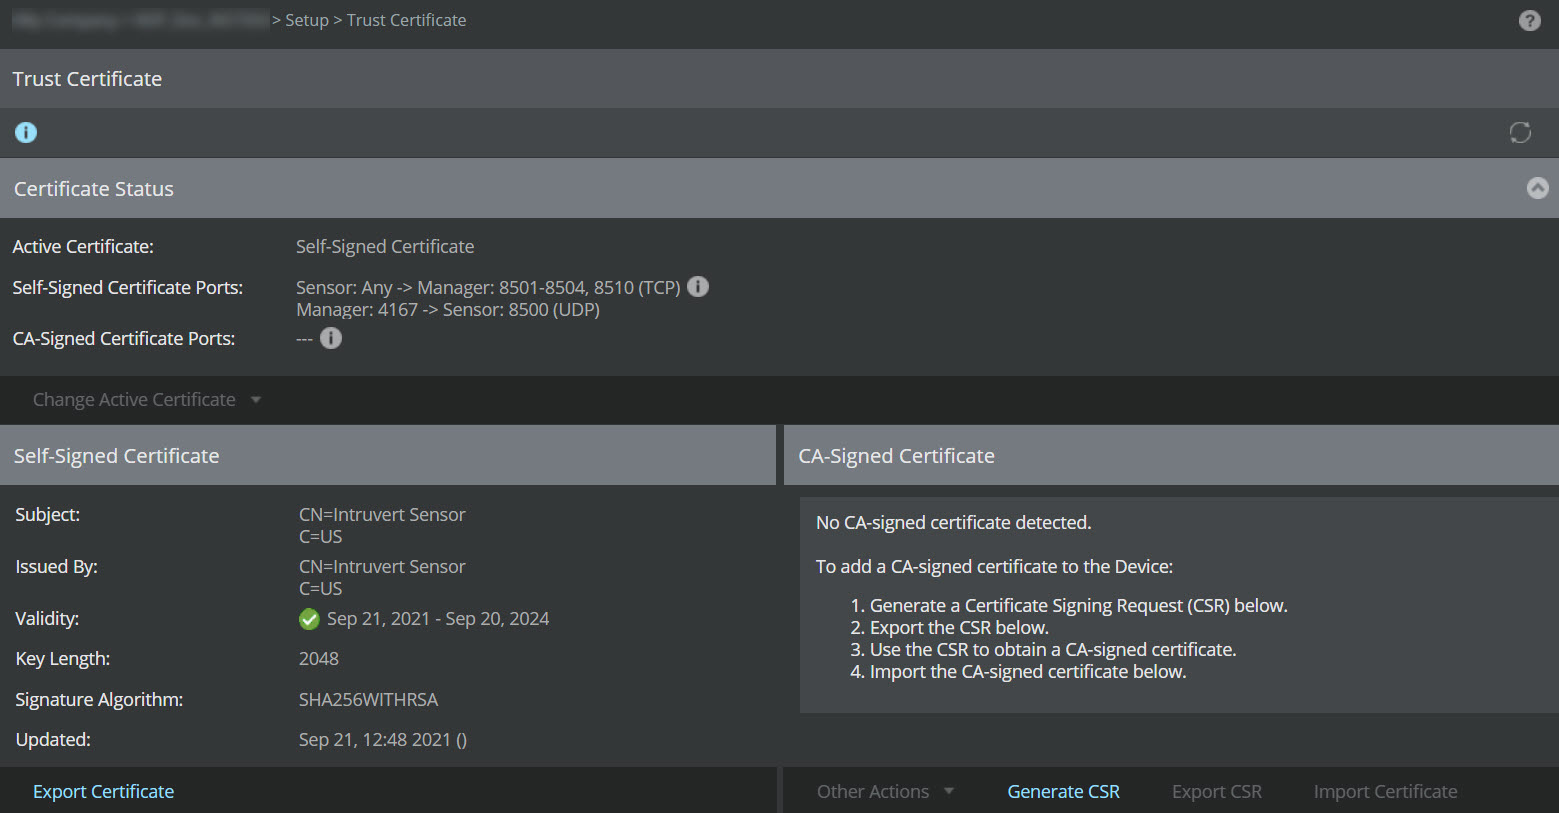
The Trust Certificate page contains the following details:
Certificate Status
This section displays the following information:
| Option | Definition |
|---|---|
| Active Certificate | Displays the type of the active certificate as either self-signed or CA-signed |
| Self-Signed Listening Ports | Ports used by the Manager to establish trust with Sensor when both use self-signed certificates |
| CA-Signed Listening Ports | Ports used by the Manager to establish trust with Sensor when both use CA-signed certificates |
The action supported for Sensor in this section is:
| Option | Definition |
|---|---|
| Change Active Certificate | Changes the active certificate of the Sensor from self-signed to CA-signed or CA-signed to self-signed |
Self-Signed Certificate
This section displays the following information regarding the self-signed certificate issued by Trellix:
| Option | Definition |
|---|---|
| Subject | Displays the following information about the certificate:
|
| Issued By | Name of the signing authority for the certificate |
| Validity | Duration for which the certificate is valid |
| Key Length | Number of bits used in the cryptographic algorithm |
| Signature Algorithm | Signature Algorithm used for the certificate |
| Updated | Date when the certificate was last updated |
The action supported for Manager and Sensor in this section is:
| Option | Definition |
|---|---|
| Export Certificate | Exports the self-signed certificate to the remote machine accessing the Manager |
CA-Signed Certificate
This section displays the following information regarding the CA-signed certificate:
| Option | Definition |
|---|---|
| Subject | Displays the following information about the certificate:
The drop-down list displays all certificates in the certificate chain. |
| Issued By | Name of the signing authority for the certificate |
| Validity | Duration for which the certificate is valid |
| Key Length | Number of bits used in the cryptographic algorithm |
| Signature Algorithm | Signature Algorithm used for the certificate |
| Updated | Date when the certificate was last updated |
The actions supported for Manager and Sensor in this section are:
| Option | Definition |
|---|---|
| Generate CSR | Generates the Certificate Signing Request (CSR).
|
| Export CSR | Exports the Certificate Signing Request (CSR) to the remote machine accessing the Manager |
| Import Certificate | Imports the CA-signed certificate from the remote machine accessing the Manager |
| Other Actions | |
| Remove Certificate | Removes the CA-signed certificate |
| Export Certificate | Exports the CA-signed certificate |
For more information about GUI Certificate, refer to GUI Certificate.