The Manager and Sensor can also use a CA-signed certificate to establish the trusted connection. By default, the Manager and Sensor use a self-signed certificate to establish trust. You can also use a CA-signed certificate chain issued by trusted CAs, such as Verisign, GeoTrust, and others, to establish trust between the Manager and the Sensor.
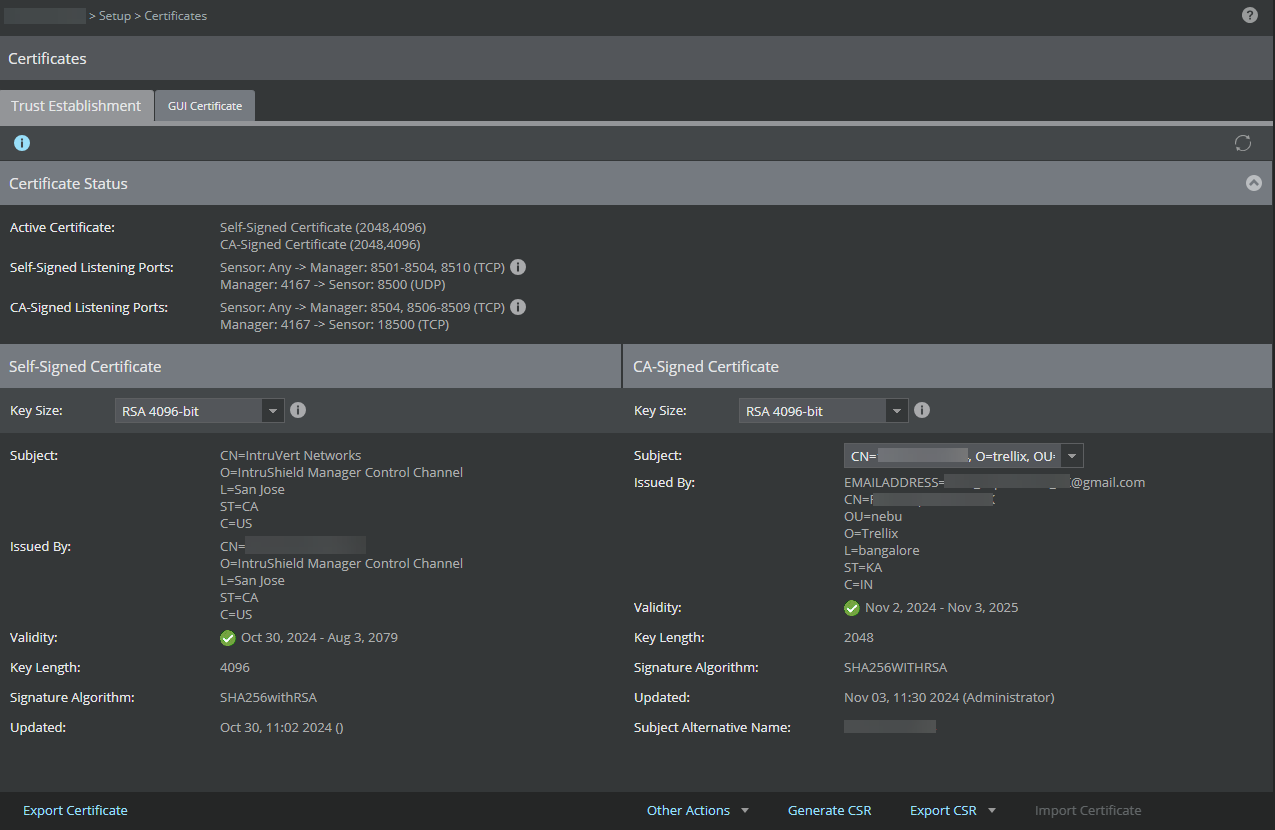
To manage the certificates for the Manager, go to Manager → <Root Admin Domain> → Setup → Certificates.
The Certificates page opens. It consists of the following tabs:
Trust Establishment
GUI Certificate
To manage the certificates for the Sensor, go to Devices → <Root Admin Domain> → Devices → <Device Name> → Setup → Trust Certificate.
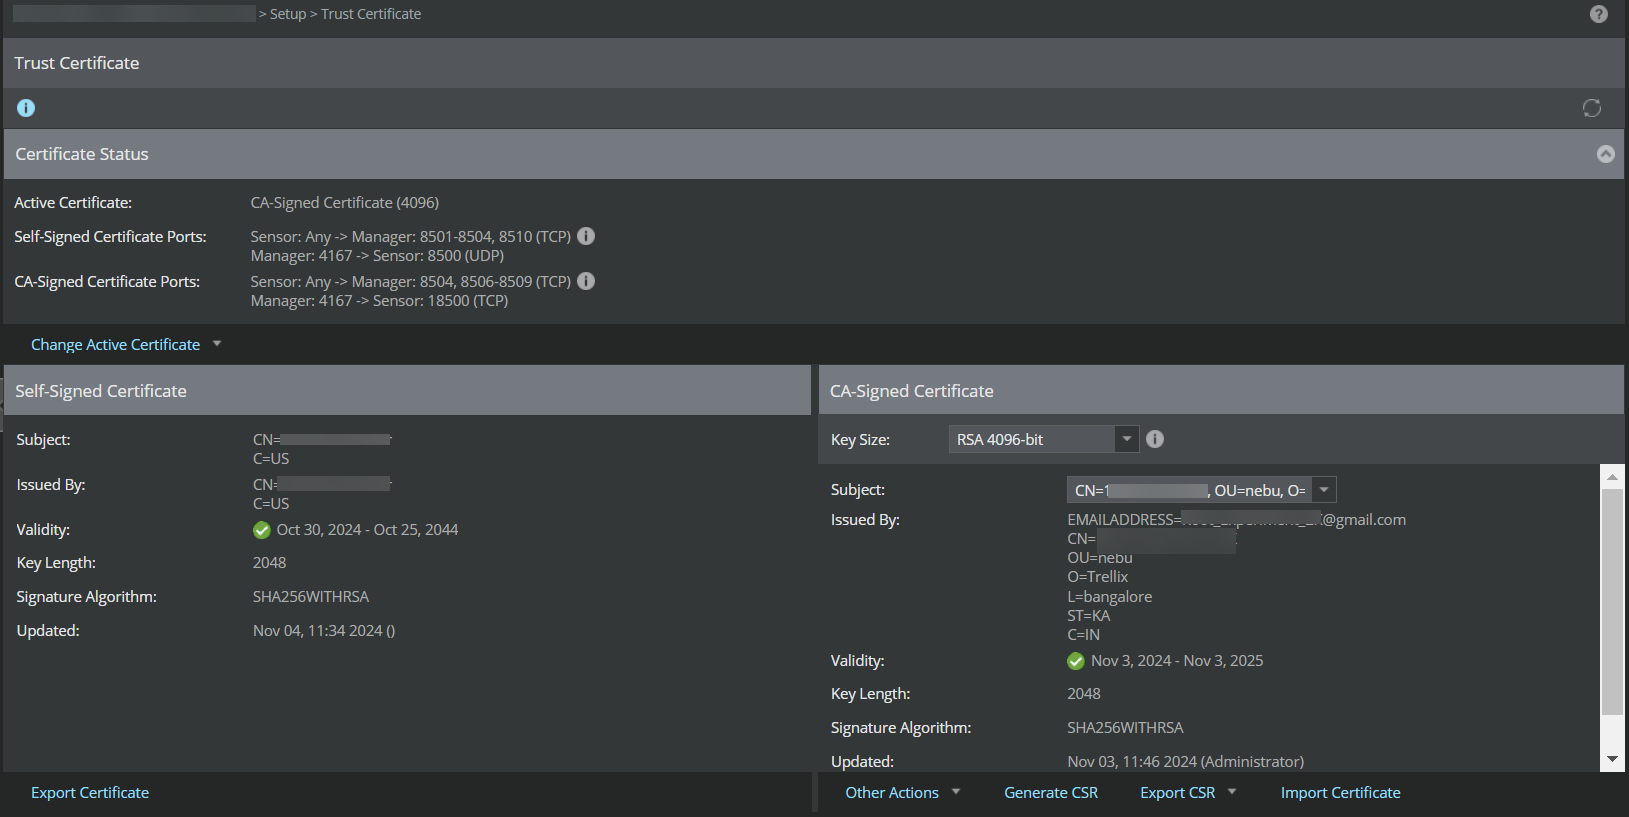
The Trust Certificate page contains the following details:
Certificate Status
This section displays the following information:
Option | Definition |
|---|---|
Active Certificate | Displays the type of the active certificate as either 2048-bit/4096-bit Self-Signed or 2048-bit/4096-bit CA-Signed |
Self-Signed Listening Ports | Ports used by the Manager to establish trust with Sensor when both use Self-Signed certificates |
CA-Signed Listening Ports | Ports used by the Manager to establish trust with Sensor when both use CA-Signed certificates |
The action supported for Sensor in this section is:
Option | Definition |
|---|---|
Change Active Certificate | Changes the active certificate of the Sensor from 2048-bit Self-Signed to 4096-bit Self-Signed, 2048-bit CA-Signed, or 4096-bit CA-Signed |
Self-Signed Certificate
This section displays the following information regarding the Self-Signed certificate issued by Trellix:
Option | Definition |
|---|---|
Key Size | Number of bits used in the RSA encryption |
Subject | Displays the following information about the certificate:
|
Issued By | Name of the signing authority for the certificate |
Validity | Duration for which the certificate is valid |
Key Length | Number of bits used in the cryptographic algorithm |
Signature Algorithm | Signature Algorithm used for the certificate |
Updated | Date when the certificate was last updated |
The action supported for Manager and Sensor in this section is:
Option | Definition |
|---|---|
Export Certificate | Exports the self-signed certificate to the remote machine accessing the Manager |
CA-Signed Certificate
This section displays the following information regarding the CA-signed certificate:
Option | Definition |
|---|---|
Key Size | Number of bits used in the RSA encryption |
Subject | Displays the following information about the certificate:
The drop-down list displays all certificates in the certificate chain. |
Issued By | Name of the signing authority for the certificate |
Validity | Duration for which the certificate is valid |
Key Length | Number of bits used in the cryptographic algorithm |
Signature Algorithm | Signature Algorithm used for the certificate |
Updated | Date when the certificate was last updated |
The Sensor and Manager will connect with 2048-bit RSA self-signed certificates by default once trust is established. If the Manager and Sensor support 4096-bit RSA certificates, you can migrate to the required certificate from Change Active Certificate. Go to Devices → <Root Admin Domain> → Devices → <Device Name> → Setup → Certificates. In the Certificate Status section, click the Change Active Certificate drop-down and select the required certificate.
The Sensor and Manager will connect with 2048-bit/4096-bit RSA CA-signed based certificates after importing valid 2048-bit/4096-bit RSA CA-signed certificates in the Manager. You can migrate to any required certificate from Change Active Certificate. Go to Devices → <Root Admin Domain> → Devices → <Device Name> → Setup → Certificates. In the Certificate Status section, click the Change Active Certificate drop-down and select the CA-signed certificate.
Note
When deploying the device in a CC configuration, the administrator must use only the RSA 2048-bit key.
The actions supported for Manager and Sensor in this section are:
Option | Definition |
|---|---|
Generate CSR | Generates the Certificate Signing Request (CSR).
|
Export CSR | Exports the Certificate Signing Request (CSR) to the remote machine accessing the Manager |
Import Certificate | Imports the CA-signed certificate from the remote machine accessing the Manager |
Other Actions | |
Remove Certificate | Removes the CA-signed certificate |
Export Certificate | Exports the CA-signed certificate |
For more information about GUI Certificate, refer to CA-signed certificate for the Web Server Authentication.