Trellix supplies a set of preconfigured policies for immediate application in a number of different network environments. These policies are available under IPS in the Manager.
These policies are "starting points," designed to help you get your system up and running quickly. You can use any of the default scenarios initially, or you can clone and modify these and apply your new policies. In fact, the Default Prevention policy, applied by default when you add your first Sensor, enables you to begin monitoring your network immediately, and actually begin blocking attacks right out of the box (if you deployed your Sensor in inline mode). As you tune your IPS, you will modify these policies to best suit your particular environment.
Each preconfigured policy is designed to address the most common attacks targeting specific network environments. To provide the most efficient attack detection options, these policies take into account distinct factors such as protocols (HTTP, SMTP), services (email, FTP, Web), and implementations (Apache, IIS).
Attacks are classified into four general categories:
Denial of Service (DoS) and Distributed Denial of Service (DDoS) — All of the conditions indicative of activities that lead to service disruption, including the slowing down or crashing of applications, servers, or networks.
Exploit — All malicious activities, other than DoS and Reconnaissance, carried out through specific traffic content. This includes buffer overflows, viruses, and worms.
Reconnaissance — All of the conditions indicative of probing, scanning, and OS fingerprinting activities. These activities are generally in preparation for more targeted attacks.
Policy Violation — All activities for which the underlying traffic content may not be malicious by itself, but are explicitly forbidden by the usage policies of the administrative domain. This includes application protocol behaviors that violate common usage practices.
The following are pre-formatted policies and their descriptions.
Note
All provided policies, except the Default Testing and Default Exclude Informational policies, enable attacks with a minimum Severity of 2 (Low) and a maximum Benign Trigger Probability of 4 (Medium). The Severity and Benign Trigger Probability settings exclude known noisy signatures in an effort to limit spurious alerts.
Policy | Designed to Protect Against |
|---|---|
Default Prevention | All attacks of Low severity or greater, below a Medium benign trigger probability, with a blocking Sensor action enabled for all Trellix Recommended for Blocking (RFB) attacks. |
Default Detection | All attacks of Low severity or greater, below a Medium benign trigger probability. |
Outside Firewall | All attacks except for Reconnaissance category. |
DMZ | All attack types except for those Exploits using TFTP, Telnet, RIP, NETBIOS, NFS, and WINS. |
Inside Firewall | All attack types except for those Exploits using TFTP, Telnet, and RIP. |
Internal Segment | All attacks except for Exploits using RIP and routing protocol attacks. |
Web Server | All Reconnaissance and DoS attacks, generic backdoors, and Exploits using DNS, HTTP, and FTP protocols. |
Mail Server | All Reconnaissance and DoS attacks, generic backdoors, and Exploits using DNS, SMTP, POP3, and IMAP protocols. |
DNS Server | All Reconnaissance and DoS attacks, generic backdoors, and Exploits using the DNS protocol. |
File Server | All Reconnaissance and DoS attacks, generic backdoors, and Exploits using DNS, NFS/RPC, and NETBIOS/SMB protocols. |
Windows Server | All attacks where the impacted OS includes Windows. |
Solaris Server | All attacks where the impacted OS includes Solaris. |
UNIX Server | All attacks where the impacted OS includes UNIX. |
Linux Server | All attacks where the impacted OS includes Linux. |
Windows and UNIX Server | All attacks where the impacted OS includes Windows or UNIX. |
Windows and Solaris Server | All attacks where the impacted OS includes Windows or Solaris. |
Windows, Linux, and Solaris Server | All attacks where the impacted OS includes Windows, Linux, or Solaris. |
Default Exclude Informational | All attacks, including those with known noisy signatures, but omitting Informational severity attacks. This policy differs from Default as it alerts for every attack in the Trellix IPS database, including those with noisy signatures. This enables expert security personnel to fully analyze their network traffic. Informational "attacks" are not enabled. |
Default Testing | Similar to Default Exclude Informational, with the exception that Informational-level alerts are included. |
Default DoS and Reconnaissance Only | All signatures are disabled by default. This policy is provided for the scenario where a substream of traffic needs to be ignored by the IPS. Alternatively, you can use Firewall Access Rules to exempt this traffic from IPS. |
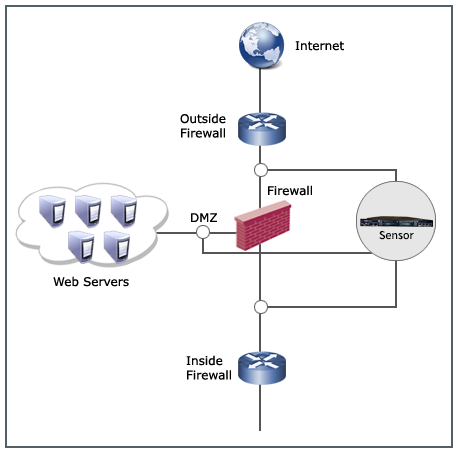
For example, in the following figure, an NS-series Sensor protects three network areas: outside the firewall, inside the firewall, and the DMZ. You can enforce a single policy across all three areas, or you can configure individual policies specifically for each zone.
In this example, the area outside the firewall is best protected by the default Outside Firewall policy (or one similar to it created by an admin) provided with Trellix IPS. For the DMZ area, the provided DMZ policy is the most efficient for that segment. Similarly, for the area inside the firewall, the provided Inside Firewall policy is best suited for the traffic in that zone.