In Trellix IPS, attacks are traditionally classified based on their type. For example, an attack can be an exploit attack, reconnaissance attack, DoS attack, or a policy violation. These categories are referred to as attack categories. Attacks are also classified based on the intent of the attack and the intended target. For example, an attack targeting vulnerabilities in client operating systems is classified under Client Protection/Operating System. These are referred to as protection categories.
There are two levels in protection categories. The first-level classification is at a broader level and can indicate whether an attack is a malware or whether it is targeted at clients or servers. Each of these categories has subcategories that can indicate the specifics of an attack. See the examples shown in the following diagram.
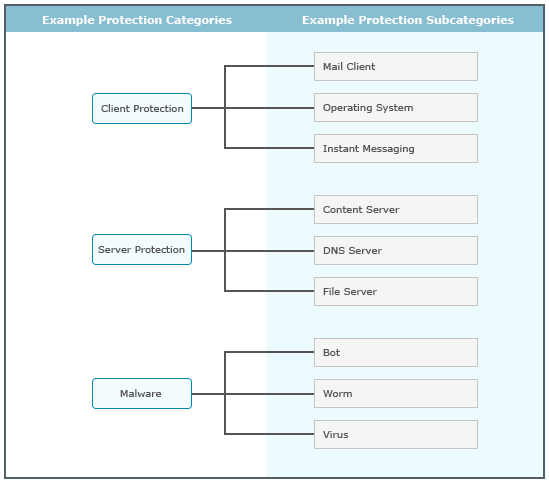
For Trellix-defined attacks, Trellix ARC classifies the attacks into one or more protection categories. In case of Trellix custom attacks, you can specify a relevant protection category for each attack definition.
Protection categories help you to relate attacks better. For example, an attack classified as an exploit that targets client operating systems is more informative than just being classified as an exploit attack. You can also view the attack definitions related to a specific category in a policy. For example, you can check what are the attack definitions you have in your policy to protect your DNS servers. Thus, you can map attack definitions to the network resources you want to protect.
In the Attack Log, the protection category feature facilitates analysis that is more granular. For, example you can analyze whether it is the clients or servers that are being attacked. Similarly, you can generate reports based on protection categories.
Notes:
Currently you can only filter based on protection categories when you view exploit attack definitions. This display filter is only available in the IPS page and not in the Master Attack Repository page (formerly Global Attack Response Editor or GARE).
In the Recon Policy Editor, you cannot filter attack definitions based on protection categories. However, in the Attack Log, protection category detail is displayed for recon attacks as well.
In the Custom Attack Editor, when you create an exploit or recon Trellix custom attack, you can specify the protection category. This is not relevant for Snort Custom Attacks.
Protection category details in the Attack Log and reports
In the Attack Log, the protection category is available for every alert in the alert details panel, if available. The number of protection categories, to which the corresponding attack belongs, is displayed. For example, if the displayed number is 2, it means the attack belongs to two protection categories. For information regarding the Attack Log, see the topic Attack Log.
When you create a Custom user defined report based on Alert Data, you can include protection category as one of the columns in the report. You can also use it as a Data Filterfor the report. For more information, see the topic Generate Custom user defined reports.