After you have created an S3 on-prem storage, you can scan it for malicious files.
Use the File Protect appliance to create, configure, and run scans on S3 on-prem storages. You can configure filters to scans and scan results to optimize scanning.
In S3 on-prem storage, the files are stored in buckets. The File Protect appliance lists all the files available in the bucket and scans them in batches. If a file is found to be malicious, it is moved to the quarantine location. You need to set the target quarantine and good locations for the corresponding files so that the File Protect appliance do not scan the same files more than once.
Note
S3 on-prem only supports continuous scan.
For S3 on-prem storage scans, the comfort file will have the ".tx-quarantined" suffix, indicating that the relevant file has been moved to the quarantine bucket.
Prerequisites
Administrator access to the File Protect appliance.
An S3 on-prem storage has been created and configured.
Follow the steps below to create a scan for S3 on-prem storage via the CLI:
Enable the CLI configuration mode:
hostname > enable hostname # configure terminalCreate an S3 on-prem continuous scan.
hostname (config) # fmps scan create from share <S3Storage>S3Storage is the storage on which the scan will run. The scan is created and a scan ID is displayed.
<scanID> configured.Save your changes.
hostname (config) # write memory
Follow the steps below to configure an S3 on-prem scan via the Web UI:
For S3 on-prem scan, in Select storage to scan select the newly added S3 on-prem storage from the drop-down menu.
When you reach Scan Type, you can only select Continuous which performs a scan at regular intervals.
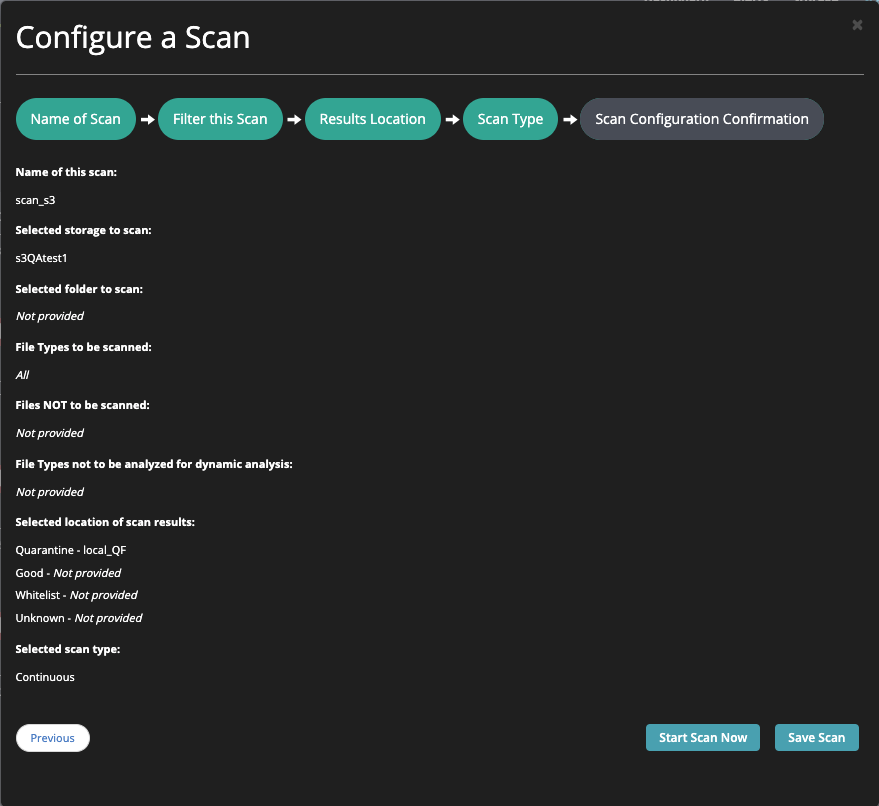
Follow the steps below to configure an S3 on-prem scan via the CLI:
Enable the CLI configuration mode:
hostname > enable hostname # configure terminalConfigure the scan name:
hostname (config) # fmps scan configure <scanId> scan-name <ScanName>Configure the filetype to scan:
hostname (config) # fmps scan configure <scanId> filetypes <FileType>Configure the start from time:
hostname (config) # fmps scan configure <scanId> start-time <StartFromTime>Save your changes.
hostname (config) # write memory
Follow the steps below to start a scan:
Enable the CLI configuration mode:
hostname > enable hostname # configure terminalStart a scan by specifying its scan ID.
hostname (config) # fmps scan start <scanID> continuous<scanID> is the ID of the scan.
Save your changes.
hostname (config) # write memory