This scenario involves inspecting the traffic going to and coming out of virtual servers installed on an ESX. In this deployment, the Sensor monitoring port acts as a gateway to the protected servers.
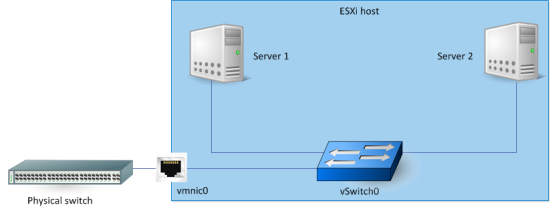
Scenario description before Virtual Sensor deployment
The servers are installed on guest VMs on the ESX.
These servers are connected to a standard vSwitch — vSwitch0.
vSwitch0 has a physical adapter, which is connected to networks outside the ESX.
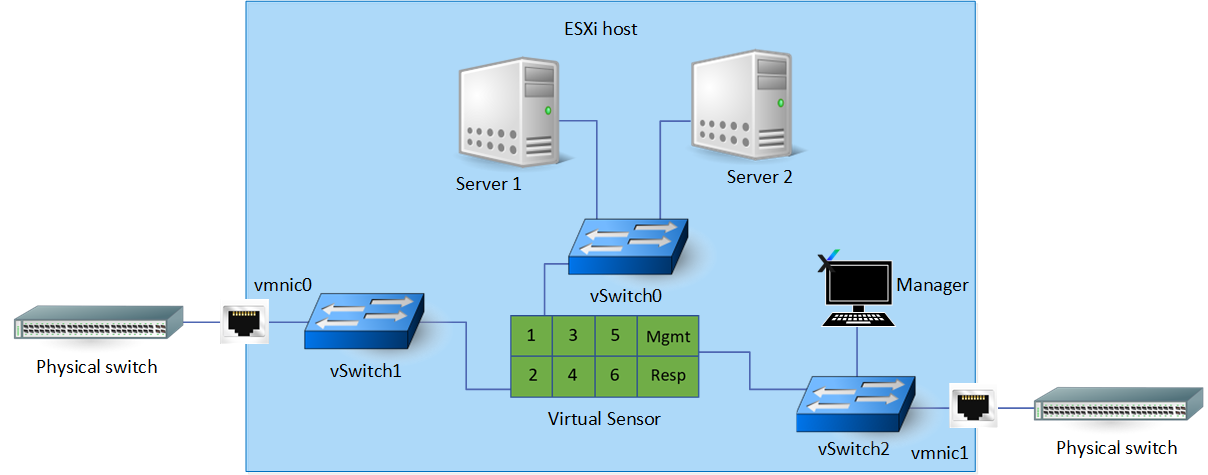
Scenario description after Virtual Sensor deployment
Two more standard vSwitches (vSwitch1 and vSwitch2) are now added.
The Virtual Sensor is deployed on the ESX.
The Manager is installed on a VM connected to vSwitch2.
The management port of the Virtual Sensor is connected to vSwitch2. This virtual switch has a physical adapter. So, you can access the Manager and the Sensor from outside the ESX.
The monitoring port pair 1-2 of the Virtual Sensor is inline between external network through vmnic0 and the server farm on the ESX.
The servers and the monitoring port 1 are connected to two different port groups in vSwitch0. The port group to which the monitoring port is connected is set to promiscuous mode.
Monitoring port 2 is connected to vSwitch1, which is in turn connected to external network through vmnic0. Therefore, any traffic to the servers from the outside network is inspected by the port pair 1-2.
Note
Note that the monitoring port 1 is connected to a promiscuous switch port group on vSwitch0. Therefore, the Sensor will inspect traffic between Server 1 and Server 2 as well though it is not inline. Effectively, this acts as if monitoring port 1 is in SPAN mode. To avoid the Sensor from inspecting the traffic between the servers, define ACLs on the Sensor accordingly.