Consider this scenario for double VLAN tagging.
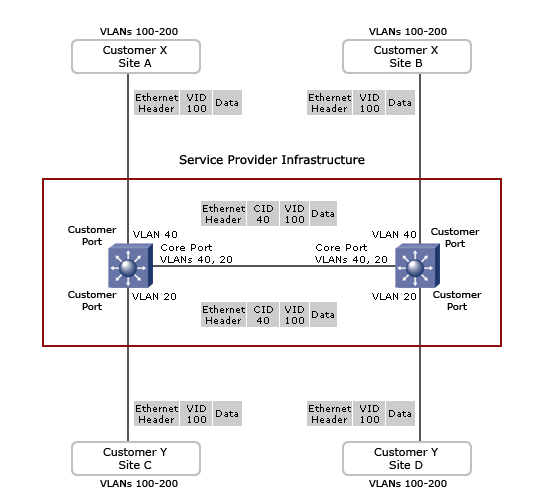
Packets entering the customer port of the service provider switch are VLAN tagged packets with original VLAN identifiers (VID) from the customer network. When the VLAN tagged packets exit the core port of the switch into the service provider network, an additional CID or outer VLAN tag is added on top of the inner VLAN tag. Within the service provider infrastructure, the VID is ignored and bridging is based on the value of the CID. When the double tagged packets enter another core port of the service provider switch, the CID tag is removed and the packets are transmitted to the appropriate customer ports associated with the CID. Therefore, when the packets exit the customer port, the original VLAN tags are preserved.