The NSM REST SDK user must authenticate with the Trellix IPS Manager by creating a unique "session" resource URL first to make API calls. The session information is then embedded in subsequent API calls to authenticate them.
The steps below walk you through downloading a REST client, creating an API session in the IPS Manager and using the session information to make an API call.
To download the Advanced REST client (ARC), which is a free, browser-based REST client, go to https://install.advancedrestclient.com/#/install.
Click Download.
Once the setup file is downloaded, install it like any setup file installation.
Once installed, go to the folder location where the file is downloaded and open ARC (Advanced REST client).
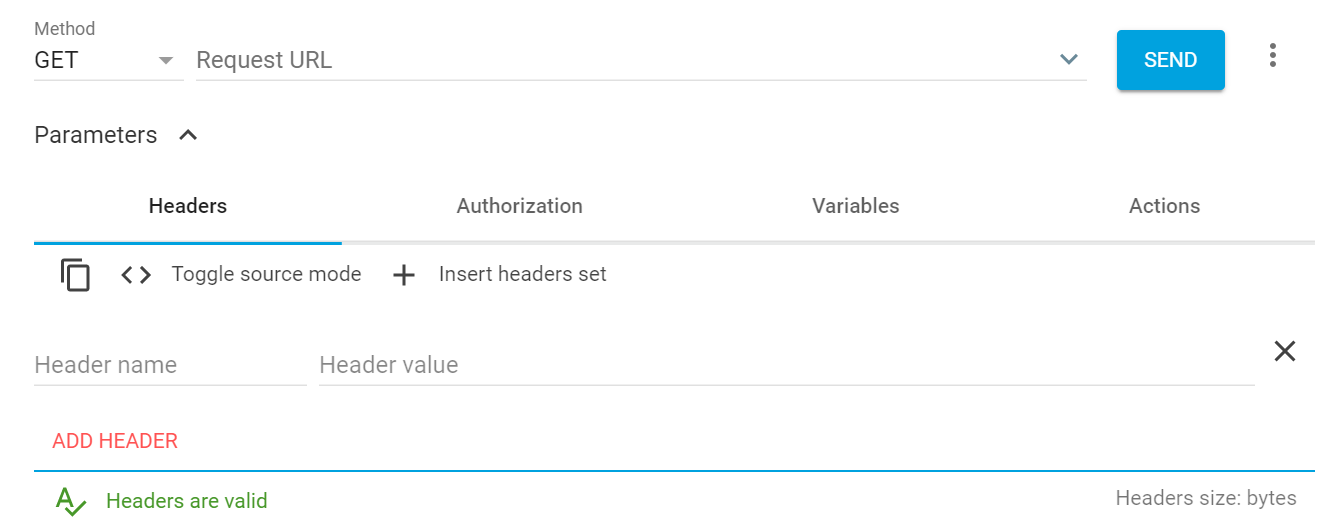
Select
GETfrom the Method drop-down list.In Request URL, type
https://<manager_ip>/sdkapi/session.Note
The Manager IP address can be IPv4 or IPv6.
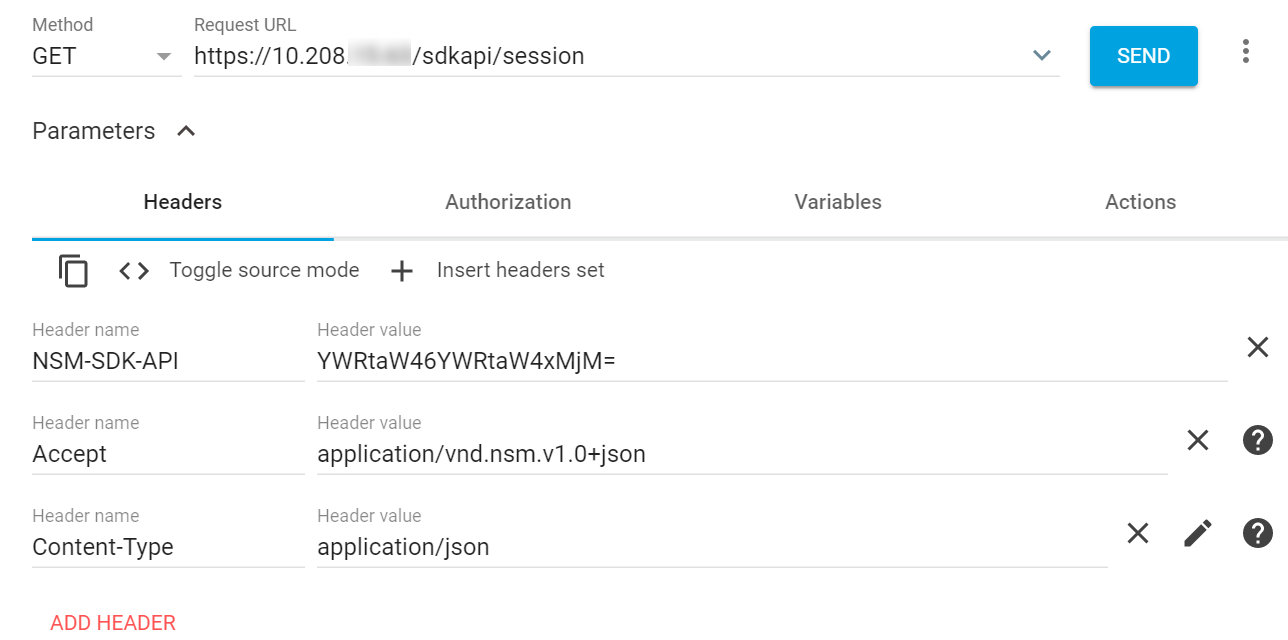
For Session resource URL, add the following three headers:
Note
For more headers, select ADD HEADER.
Header Name
Header Value
NSM-SDK-API
<base64 encoded value of Manager credentials, that is
username:userpassword>Note
Base 64 encoded values can be generated at https://www.base64encoder.io. For example, the base 64 encoded value of
admin:admin123isYWRtaW46YWRtaW4xMjM=Note
To make API calls, the user should have the role of a super user in the Manager.
Accept
application/vnd.nsm.v1.0+json
Content-Type
application/json
Click Send.
Response
{ "session": <ABC3AC9AB39EE322C261B733272FC49F> "userId": "1" }For other resource urls, In Request URL, type
https://<nsm_ip>/sdkapi/<Resource URL>.Add the following three headers:
Note
For more headers, select "ADD HEADER."
Header Name
Header Value
NSM-SDK-API
Use the response details obtained in step 7 in https://www.base64encoder.io to change the header value of the NSM-SDK-API and access other Manager API resources. For example, the base 64 encoded value of
ABC3AC9AB39EE322C261B733272FC49F:1> isQUJDM0FDOUFCMzlFRTMyMkMyNjFCNzMzMjcyRkM0OUY6MQ==Note
To make API calls, the user should have the role of a super user in the Manager.
Accept
application/vnd.nsm.v1.0+json
Note
For a few resource URLs, the parameter value changes. Refer to the table below for different Accept values.
Content-Type
application/json
Note
For a few resource URLs, the parameter value changes. Refer to the table below for different Content-Type values.
For a few resource URLs, the Accept and Content-Type values also change with the NSM-SDK-API value. Hence, use the table given below for the URLs with different Accept and Content-Type values:
Resource
Resource URL
Method
Content-type value
Accept value
Import the Domain Name Exceptions to the Manager
POST /domainnameexceptions/import
POST
multipart/form-data; boundary=<x>
Import custom internal Web Server certificate
PUT /domain/sslconfiguration/importinternalwebservercerts
PUT
multipart/form-data; boundary=<x>
Get the list of importable IPS and Reconnaissance policies
PUT /domain/<domain_id>/ipsreconpolicy/import
PUT
multipart/form-data; boundary=<x>
Import a custom re-sign certificate
PUT /domain/sslconfiguration/importresigncert
PUT
multipart/form-data; boundary=<x>
Nessus Scan Report Import
PUT domain/<domain_id>/integration/vulnerability/importscanreport
PUT
multipart/form-data; boundary=<x>
Import a custom trusted CA certificate
PUT /domain/sslconfiguration/importtrustedcert
PUT
multipart/form-data; boundary=<x>
Import the Exceptions
POST /domain/<domain_id>/ exceptions/import
POST
multipart/form-data; boundary=<x>
Import the Firewall policies
POST /domain/<domain_id>/ firewallpolicy/import
POST
multipart/form-data; boundary=<x>
Import the IPS and Reconnaissance policies
POST /domain/<domain_id>/ipsreconpolicy/import
POST
multipart/form-data; boundary=<x>
Import the Malware policies
POST /domain/<domain_id>/malwarepolicy/import
POST
multipart/form-data; boundary=<x>
Import Custom Fingerprints
PUT /domain/<domain_id>/filereputation/customfingerprints
PUT
multipart/form-data; boundary=<x>
Import Allowed Fingerprints
PUT /domain/<domain_id>/filereputation/allowedfingerprints
PUT
multipart/form-data; boundary=<x>
Manual Device Software Import to Manager
PUT /devicesoftware/import/manual
PUT
multipart/form-data; boundary=<x>
Manual Botnet File Import to Manager
PUT /botnetdetectors/import/manual
PUT
multipart/form-data; boundary=<x>
Manual Gateway Anti-Malware File Import to Manager
PUT /gam/import/manual
PUT
multipart/form-data; boundary=<x>
Manual Signature Set Import to Manager
PUT /signatureset/import/manual
PUT
multipart/form-data; boundary=<x>
Import the Sensor Configuration
PUT /sensor/<sensor_id>/importconfiguration
PUT
multipart/form-data; boundary=<x>
Import SSL Key to the Manager
POST /sensor/<sensor_id>/action/sslkey
POST
multipart/form-data; boundary=<x>
Import License
PUT /vmips/license
PUT
multipart/form-data; boundary=<x>
Export the public key of the active re-sign certificate
GET /domain/sslconfiguration/exportresigncert
GET
application/octet-stream
Export the PCAP file captured
PUT /sensor/<sensor_id>/packetcapturepcapfile/export
PUT
application/octet-stream
Export the Diagnostic Trace file captured
PUT /sensor/<sensor_id>/diagnosticstrace/export
PUT
application/octet-stream
Get Packet Capture of an Alert
GET /domain/<domainId>/threatanalysis/packetlog?alertId=<alertId>&device=<deviceName>
GET
application/octet-stream
For example consider heartbeat resource, in Request URL give
https://<nsm_ip>/sdkapi/heartbeatand NSM-SDK-API withQUJDM0FDOUFCMzlFRTMyMkMyNjFCNzMzMjcyRkM0OUY6MQ==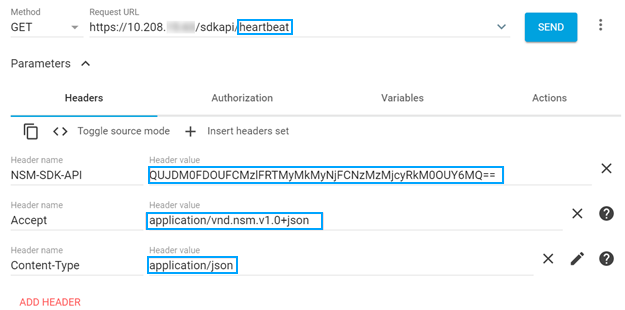
Click Send.
The response of the resource URL is displayed.
Starting release 9.1, only SSL protocol TLS 1.2 is supported for connection with the Manager. All requests to API use TLS 1.2. On successful authentication, 'Session' resource URL returns the user ID and session ID in the response body. Every resource URL in the SDK is required to pass these credentials for validation and authorization in NSM-SDK-API custom header.