After you define the details for a Trellix IPS Custom Attack, you need to define one or more signatures for that attack. To access the signature creation interface, in the New Custom Attack interface, click on the Signature-<signature name> tab.
The signature creation interface presents the details related to the signature you are creating. These details are used to provide further information about the suspicious activity for which you are attempting to capture and analyze through Custom Attacks. By configuring each field, you are further refining the signature's search, which raises the probability your attack will successfully detect the desired activity, thus preventing false positives.
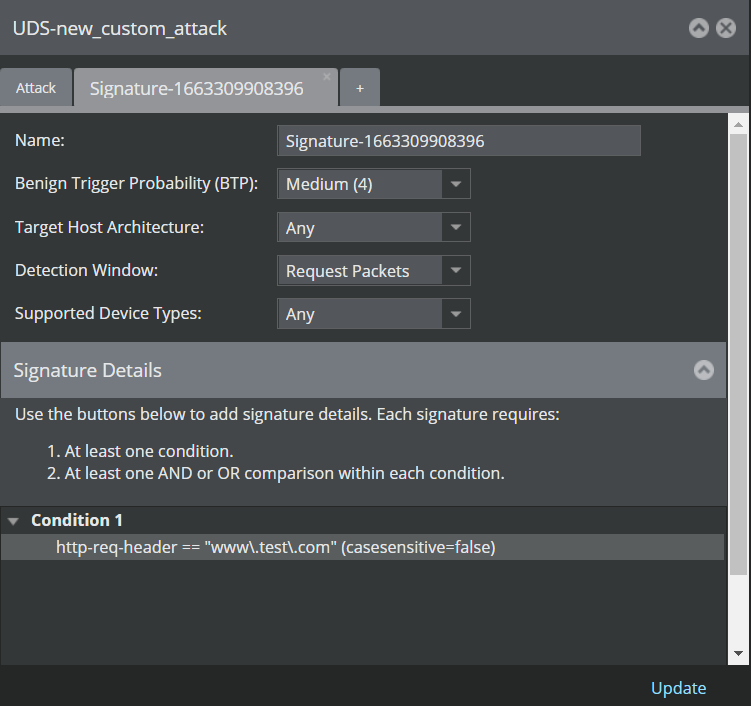
The signature detail fields are as follows:
Option | Definition |
|---|---|
Name | The name you give to the signature. If the attack is detected, the Attack Log displays the detecting signature in the attack's details window. |
Benign Trigger Probability (BTP) | This is an indication of the probability that your signature will alert on traffic that may not be an attack. The choices are High, Medium, and Low, with Low representing approximately a 0% to 33% chance of your signature raising a false positive. For example, your signature may be a generic string search, such as "Confidential", thus the BTP would be best graded as High. If you know a specific file name that is infected or sensitive, such as "program.exe", you could set your BTP to Low to reflect your confidence in your signature. |
Target Host Architecture | You can define a specific machine architecture targeted by an attack with shellcode. For example, to detect a Intel-specific shellcode, you can select i386 as the architecture. The default is any. |
Detection Window | This field describes where in a flow you want your signature to actively check traffic. The choices are as follows:
|
Supported Device Types | You can apply a Trellix IPS Custom Attack signature for any of the following device type options:
The value for this field depends on what you select for the constituent signatures. For example, if the attack contains signatures with Supported Device Types set only to NS-series, then the value displayed here is NS‑series Only. You cannot edit this field at the attack level, but the Manager modifies it accordingly when you change it for the corresponding signatures. |
Conditions | A condition is the test or group of tests that, if met, raises an alert. Conditions are made up of protocol field tests, or comparisons. A signature may have multiple conditions, each with multiple comparison tests. If you configure multiple conditions for a signature, each condition must be met in order (ANDTHEN logic) before an alert is raised.
|
Comparisons | Within a condition, you add one or more comparison tests. Comparisons can be AND or OR in nature. AND comparisons must be met for an alert to be generated for malicious traffic. OR comparisons allow for multiple comparisons within a condition, of which only one of the OR tests must be met to raise an alert. You must start a condition with an AND comparison. You may have up to 32 comparisons per condition.
|


