This section discusses the basic structure of a Snort rule and the Snort rule elements that are supported in Trellix IPS. This section contains information on the syntax that you should use in Trellix IPS for each element. You can also find an example rule for each element, wherever applicable.
How you combine various Snort rule elements to form a rule depends on your security requirements. This information is out of scope of this document because the requirements can vary from network to network.
Note
The Snort rules that you plan to use in Trellix IPS should conform to Snort rules language.
A Snort rule in Trellix IPS can run into multiple lines. A typical Snort rule has two logical sections — rule header and rule options.
The following is an example of a simple but valid Snort rule.
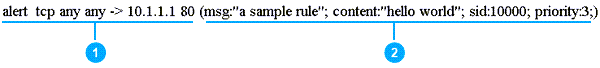
Item | Description |
|---|---|
1 | Rule header section |
2 | Rule options section |
As shown above, the rule header section starts at the beginning of the rule and ends at the opening parenthesis. This section contains the following:
Action — In the sample above, it is alert.
Protocol — In the sample above, it is TCP.
Source and destination IP addresses — In this case, the source is any and the destination is 10.1.1.1
Source and destination ports — In this case, the source port is "any" and the destination port is 80.
The rule options section is enclosed within the parentheses. This section contains alert messages and information on which parts of the packet should be inspected to determine if the rule action should be taken. In the rules options section, the words ending in a colon are option keywords.
Note
In Trellix IPS, the rule options section should have at least the msg and the sid keywords with values. Rule options enable you accurately define the attack traffic that the Sensor should look for.
All the elements that make up a rule must be true for the Sensor to raise an alert and take the defined response action. You specify the response action for the Snort Custom Attack in the IPS Policy Editor.