The terms VIDS and VIPS reinforce the idea that virtualization allows you to tailor a single Sensor solution as if it were a multiple-Sensor solution. The Trellix IPS user interface uses the term sub-interface, and this term better describes the process by which virtualization is implemented.
Sensors take port monitoring deeper than the interface-level: you can segment the security management of an interface and apply policies at a traffic sub-flow level within the interface. A sub-flow, or sub-interface, is a segment of data within a traffic flow. This sub-interface is also a VIPS. A VIPS can be defined based one or more blocks of CIDR-based IP addresses or one or more VLAN tags. Sensors can process these data segments and apply multiple traffic policies for the multiple subnets transmitting across a single wire, right down to policies protecting individual hosts.
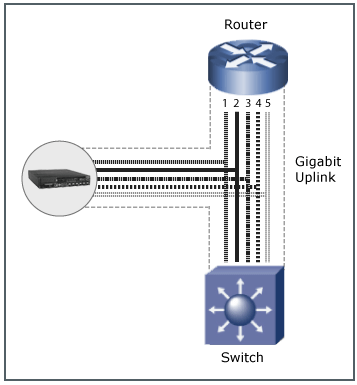
In the above figure, a gigabit uplink between a router and a switch is monitored in external tap mode by an NS9300. Behind the switch is a corporate network with five departments: HR, Sales, Payroll, Engineering, and Marketing. The traffic for each of these departments has been segmented using VLANs with each department's traffic tagged with a distinct VLAN ID, represented by the numbers 1-5 in the illustration.
Using peer ports G0/1 and G0/2 to tap the full-duplex uplink, the NS9300 can analyze and process the VLAN IDs in the traffic transmitted between the router and switch. The security administrator can configure unique policies for each VLAN ID (representing traffic from the different departments) within the uplink, rather than apply a single policy across the entire interface. In this scenario, each of the five VLAN IDs from each of the five departments can have a distinct policy assigned to it, or different combinations of the VLAN IDs within the uplink can have the same policy applied. Policy application simply depends on assigning a policy to an interface or sub-interface resource as you see fit.