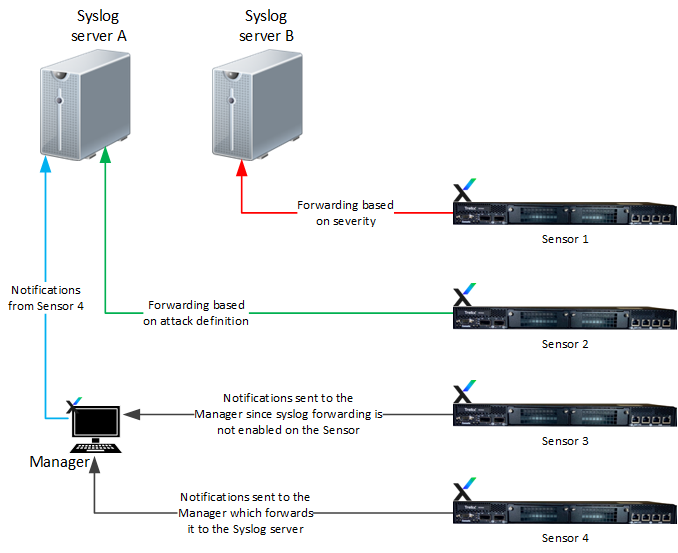
The Sensor and Manager can independently be configured to forward alert information to a syslog server. By default, the Sensor forwards alert information to the Manager, and if configured, the Manager forwards this information to the syslog server.
However, consider an organization that has more than one Sensor associated with a single Manager. Let's assume that each Sensor represents a business unit. Security analysts for each business unit might ask to receive alert information associated only with their business unit. To accommodate such environments, provision is made to configure those Sensors to forward notifications to a specific syslog server.
Summarizing the steps that needs to be followed to forward alert notifications to a syslog server:
Configure a syslog server to make sure it is accessible to the Sensor or the Manager.
Either configure the Sensor to directly send notifications to the syslog server or configure the Manager to send such notifications after consolidating alert information from all devices where syslog notification is enabled.
Enable syslog fowarding in the Manager – at the Manager level, global level, or device level.
Determine whether you want to receive all alert notifications or only some depending on the attacks or the attack severity.
If you have chosen to receive syslog notifications based on the attack definition, configure those attacks.
If you have chosen to receive alert notification based on both attack severity and definition, the Sensor will give preference to the severity of the attack when deciding whether to forward the notification or not.
This illustration represents a sample syslog forwarding scenario.