A tagging endpoint is quarantined which helps in the analysis of the source endpoint or the destination endpoint. ePO - On-prem and ISC enables tagging of endpoints and provides analysis information in case of suspicious activities. In case of ePO tagging, only managed endpoints can be tagged. The tagged endpoint is quarantined and a response action can be configured for the endpoint from the ePO server. In case of ISC, the tagged VMs are quarantined. Response action for the tagged endpoint can be configured, which either allows the traffic to flow through the VM or completely blocks the traffic.
Note
Tagging an endpoint to ePO is not applicable for the Central Manager.
ePO
To tag an endpoint to the ePO server, complete the following steps:
Navigate to Analysis → <Admin Domain Name> → Attack Log.
Select the alert whose endpoint you wish to tag. It can either be the source IP or the destination IP.
Select Other Actions → Tag Endpoint → in ePO, and click the source or destination IP to be tagged.
The Tag Endpoint pop-up opens.
Tag an endpoint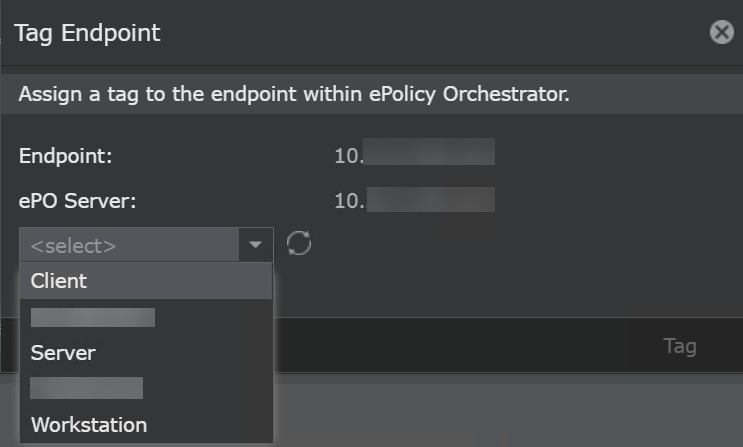
The ePO server is selected by default depending on the admin domain from which the endpoint is being tagged.
Select the tag from the Tag to Assign drop-down list.
Click Tag.
A successfully tagged message is displayed.
Note
You can create your own tags in ePO other than the default tags that exist. To retrieve the latest set of tags, click the refresh icon. To avoid errors, make sure that the endpoint being tagged is a managed endpoint and the tags exists in the ePO server.
For more details, refer to the chapter Integration with Trellix ePolicy Orchestrator - On-premises in Trellix Intrusion Prevention System Integration Guide.
ISC
To tag an endpoint to ISC, complete the following steps:
Navigate to Analysis → <Admin Domain Name> → Attack Log.
Select the alert whose endpoint you wish to tag.
Select Other Actions → Tag Endpoint → via ISC, and click the source or destination IP to be tagged.
The Tag Virtual Endpoint via ISC pop-up opens.
The endpoint and VSS server are detected by default.
Select the tag from the Tag to Assign drop-down list.
Click Tag.
A successfully tagged message is displayed.
Note
Only the default tags are available for tagging the endpoint.
For more details, refer to the chapter IPS for virtual networks using Intel® Security Controller in Trellix Virtual Intrusion Prevention System Product Guide.