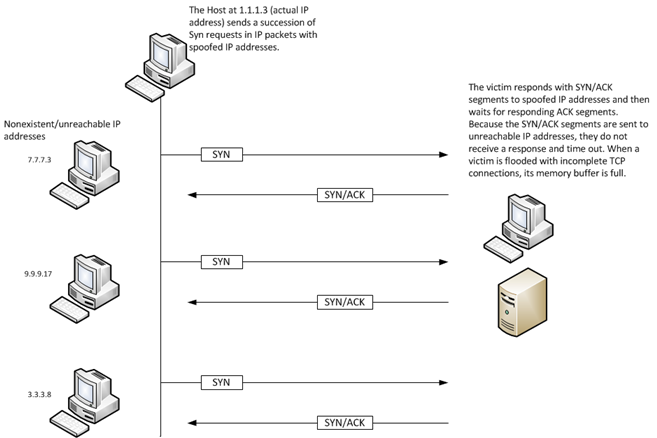
A TCP SYN attack takes place when the attacker sends a large volume of TCP SYN packets using spoofed IP addresses to the target host. This fills up data structures on servers and creates a DOS condition.
Consider the following example. Two hosts establish a TCP connection using the three-way handshake — A sends a SYN segment to B; B responds with a SYN/ACK segment; A responds with an ACK segment. A SYN flood attack occurs when a site is inundated with SYN segments containing spoofed IP source addresses such as nonexistent or unreachable addresses. B responds with SYN/ACK segments to these addresses and then waits for responding ACK segments. Because the SYN/ACK segments are sent to nonexistent or unreachable IP addresses, they never elicit responses and eventually time out. When a host is flooded with incomplete TCP connections, a DoS condition is created.
Once this buffer is full, the host can no longer process new TCP connection requests, even the legitimate ones. The attack disables the victim and its normal operations.