Common Platform Enumeration to identify vulnerable systems
If the operating system does not completely match, the result of the attack is inconclusive. In such circumstances, the Manager assigns a partial relevance score by way of a scoring algorithm. Scoring relies on the matching each component of the Common Platform Enumeration (CPE) name of attack signature with CPE name of the target system. CPE™ is a standardized method of describing and identifying classes of applications, operating systems, and hardware devices present among an enterprise's computing assets. CPE can be used as a source of information for enforcing and verifying IT management policies relating to these assets, such as the vulnerability of a target system to a malicious attack. Trellix IPS collects information about servers, workstations and other devices on the network, identifies these products using their CPE names, and uses this standardized information when matching the CPE of the attack signature to the CPE of each device. For more information on CPE, you can go to http://cpe.mitre.org.
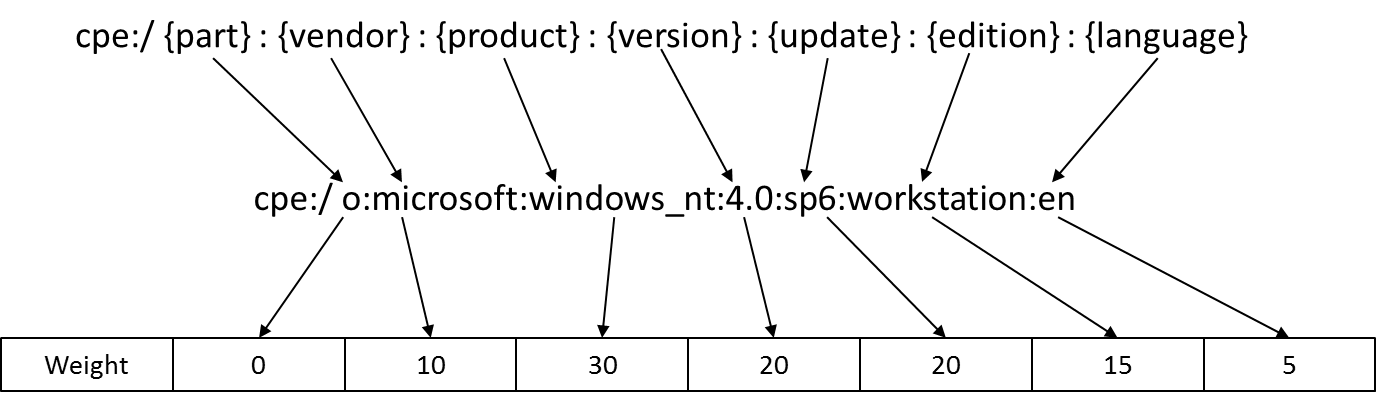
CPEs are represented in a certain order and with a specific syntax. The universal CPE format is represented in the following figure.

How CPE influences the relevance score
Each component in the CPE is given a specific weight depending on the potential of that component to contribute to the vulnerability of the system. The table below presents the various components in the CPE that are used to compute the relevance score:
Component | What it signifies | Carries a weight of |
|---|---|---|
Part | First component in the CPE, which is a single letter code that designates the particular platform part that is being identified. The following codes are defined for the part:
| 0 |
Vendor | Second component in the CPE name, which refers supplier or vendor of the platform part. Example: Microsoft, Redhat, etc. | 10 |
Product | Third component in the CPE name, which refers a specific product developed by the vendor. Example: Windows XP, Windows NT, Enterprise Linux, etc. | 30 |
Version | Fourth component in the CPE name, which refers to a specific version of the product. Example: 4.0 for Window NT, 4 for Enterprise Linux, etc. | 20 |
Update | Fifth component in the CPE name, which refers to a specific update of the version. Example: SP6 for Wndows NT, Update 4 for Enterprise Linux, etc. | 20 |
Edition | Sixth component in the CPE name, which refers to the edition of the product. Example: Workstation, Server, etc. | 15 |
Language | Seventh component of the CPE name, which refers to the language of the product. Example: English, Spanish, etc. | 5 |
The illustrative diagram below shows the format and correlates it with real world products and in turn with weights as displayed in the table above.
Following are a few examples of CPEs:
cpe:/o:microsoft:windows_xp:::procpe:/a:adobe:reader:8.1cpe:/o:redhat:enterprise_linux:4:update4
CPE name matching logic
To compute the relevance score, the CPE of the attack signature is matched with every component of the CPE of the target system. If any component is not mentioned in the attack signature CPE, it applies to all instances that can occupy that position. For example cpe:/o:microsoft:windows_xp applies to all versions, updates, editions, and languages of Microsoft Windows XP.
A CPE match is considered definitive.
A few more examples to illustrate the name matching logic are presented below:
Case 1 –
cpe:/o:microsoft:windows:xpwill match all the operating system variants mentioned below:cpe:/o:microsoft:windows:xp::sp1cpe:/o:microsoft:windows:xp::sp2cpe:/o:microsoft:windows:xpcpe:/o:microsoft:windows:xp::sp1:professionalcpe:/o:microsoft:windows:xp::sp1::en
Case 2 –
cpe:/o:microsoft:windows:xp::sp1will not matchcpe:/o:microsoft:windows:xp::sp2because not all parameters of the attack signature CPE match the target system CPE.
Scenarios to understand score computation
Refer to the table below to view some scenarios for alert relevance scoring.
Attack signature CPE | Description of the attack signature CPE | Target system CPE | How the two CPEs match up | Relevance score |
|---|---|---|---|---|
| This attack is relevant to all Microsoft Windows XP SP2 systems, irrespective of which version, edition, and language they use. |
| Since the CPE from the attack signature is considered definitive, and all components of the target system CPE match the components of the attack signature CPE, the alert generated is 100% relevant. | 100% |
| Since the CPE from the attack signature is considered definitive, and only the | 80% | ||
| Since the CPE from the attack signature is considered definitive, and the | 0% |
Special scenarios in which the relevance score is computed
In day-to-day operations, not every attack that is mounted and consequently every attack signature CPE that is extracted is as straightforward as those that are mentioned above. In some cases of device profiling, a thorough analysis might not be possible. As a result, device profiling does not isolate the operating system and presents a possibility of more than one operating system. The relevance score is calculated by as the average relevance score of all the matched CPEs.
Presented in the table below are some such scenarios where the relevance score is computed for a group of CPEs.
Representation of a group CPE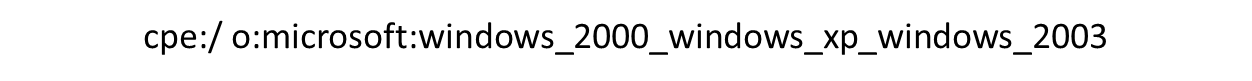 Illustrating relevance score calculation for group CPEs through examples
Host group CPE
Maps to individual CPEs
CPE match scenarios
Relevance score logic
Relevance score
cpe:/o:microsoft:windows_2000_windows_xp_windows_2003cpe:/o:microsoft:windows_xpcpe:/o:microsoft:windows_2000cpe:/o:microsoft:windows_server_2003Case 1: All CPEs match
cpe:/o:microsoft:windows_xpcpe:/o:microsoft:windows_2000cpe:/o:microsoft:windows_server_2003Since all the CPEs match, the relevance score is computed as the maximum.
100%
Case 2: Two CPEs match
cpe:/o:microsoft:windows_xpcpe:/o:microsoft:windows_server_2000Since only two of three CPEs match, the score will be computed as 200/3 = 66%.
66%
Case 3: One CPE matches
cpe:/o:microsoft:windows_xpcpe:/o:microsoft:windows_server_2008Since only one of three CPEs matches, the score will be computed as 100/3 = 33%.
33%
Case 4: Two CPEs match
cpe:/o:microsoft:windows_xpcpe:/o:microsoft:windows_server_2000cpe:/o:microsoft:windows_server_2008Since only two of three CPEs match, the score will be computed as 200/3 = 66%.
66%
There are also cases when conventional methods of calculating a relevance score are not able to provide a score. This is especially noticed when the exact details of the operating system are not available. It can also be noticed when the attack is being launched through an application and details of the application are not available. In such instances, the Manager relies on the attack signature to be able to provide you more clarity.
The Manager determines the vulnerable application and uses the signature to decipher the operating system it is compatible with. It then compares this operating system to the target operating system. If they match, a default score of 50% is displayed. If they do not match, a score of 0% is displayed. For example, if the application is one that runs only on a Linux-based operating system but the attack is directed at a system running Microsoft Windows, the attack will not be relevant. Or, assume that the attack is one that exploits a vulnerability in Microsoft Word (which is assumed to only be compatible with Microsoft Windows) and the target environment is running some Microsoft product, a default score of 50% will be displayed, prompting you to further investigate.