The Manager helps you easily view the top attacks, attackers, targets, and malware within a given period of time and a direction (optional) using the Threat Explorer. The Threat Explorer shows the attacks that have happened the most, the IP addresses responsible for most of the attacks, the IP addresses that are mostly attacked, the applications used to perform most of these attacks, and the most commonly downloaded or uploaded malware to perform these attacks.
To view the Threat Explorer page, perform any one of the following actions:
On the Analysis tab, click <Domain Name> → Threat Explorer.
On the Dashborad tab, click on any of the attack statistics. It will open the Threat Explorer page.
Also, for a given IP address, the integration with other Trellix point products helps you to view the host name, operating system, open ports, and known vulnerabilities, thus making the information readily available.
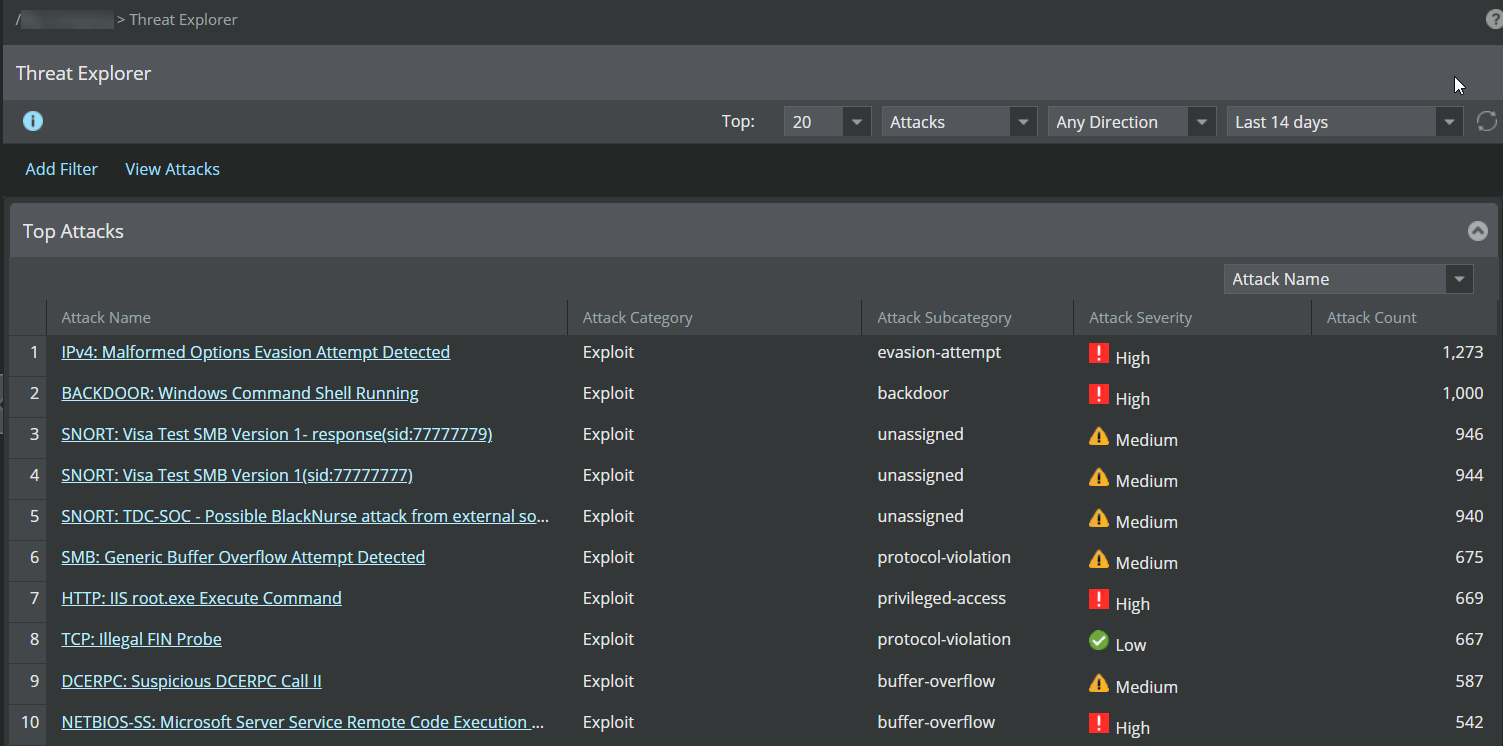
The Top option helps you to filter the data displayed in the tables on the basis of the following components:
The number of top N core attributes you want to view. The minimum and maximum values of N are 5 and 25, respectively. The default value of N is 5.
The Attacks filters the top attacks, attacker, target, and so on.
The inbound or outbound direction of the attack. The default is Any direction.
The time frame of the core attributes in the top N tables. The minimum time is last 5 minutes. The data can be filtered for the time period of your preference using the Custom Time Period option. The default value is last 12 hours.

You can use the following options to customize your Threat Explorer page view.
Name | Icon | Description |
|---|---|---|
Hide |  | Hide the top N table of your choice. |
Expand |  | Expand the top N table of your choice. |
Add filter |  | Add filter of your choice. |
Launch Attack Log |  | Go to Attack Log to view the alerts. |
Scenario: Ease of drill down from the Dashboard page
With a task-based design, the Manager user interface enables you to easily drill-down to locate root cause for an issue. Let us see an example here.
The Dashboard page allows you to investigate on the top applications under the Top Applications graph.
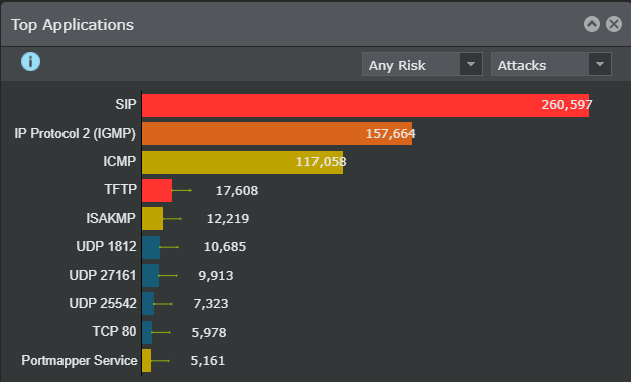
You can view the top applications bar chart based on the risk type. The available options in the drop-down list are Any Risk, High Risk and Medium+ Risk. The default option is Any Risk. You can further categorize the view of top applications based on the Attacks category.
To further investigate on a top application:
Hover over the top application bar chart. You can view details like the application name, connection count, risk and category.
Click on an application bar in the Top Applications monitor. This navigates to Threat Explorer page with the filter created for the corresponding application and the top N tables populated accordingly with the data.
Top applications in Threat Explorer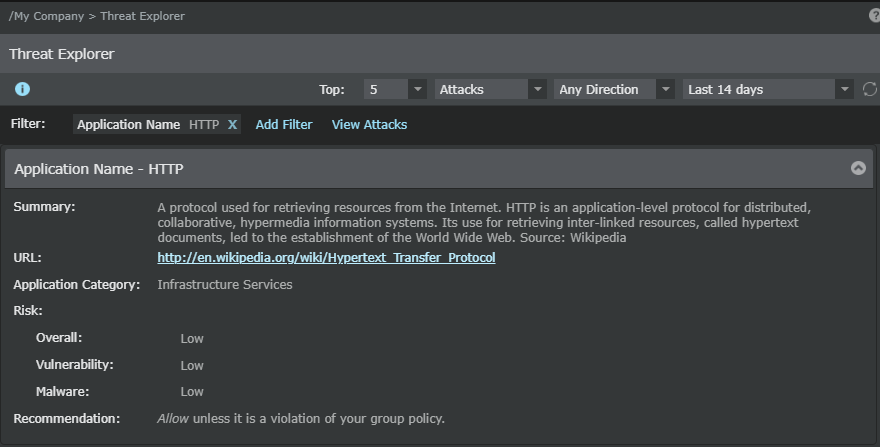
You can perform these actions based on your investigation needs.
Add multiple level filter criteria to view more specific details.
Click View Attacks to navigate to Attack Log and view all alerts pertaining to this application.
Attack log with filters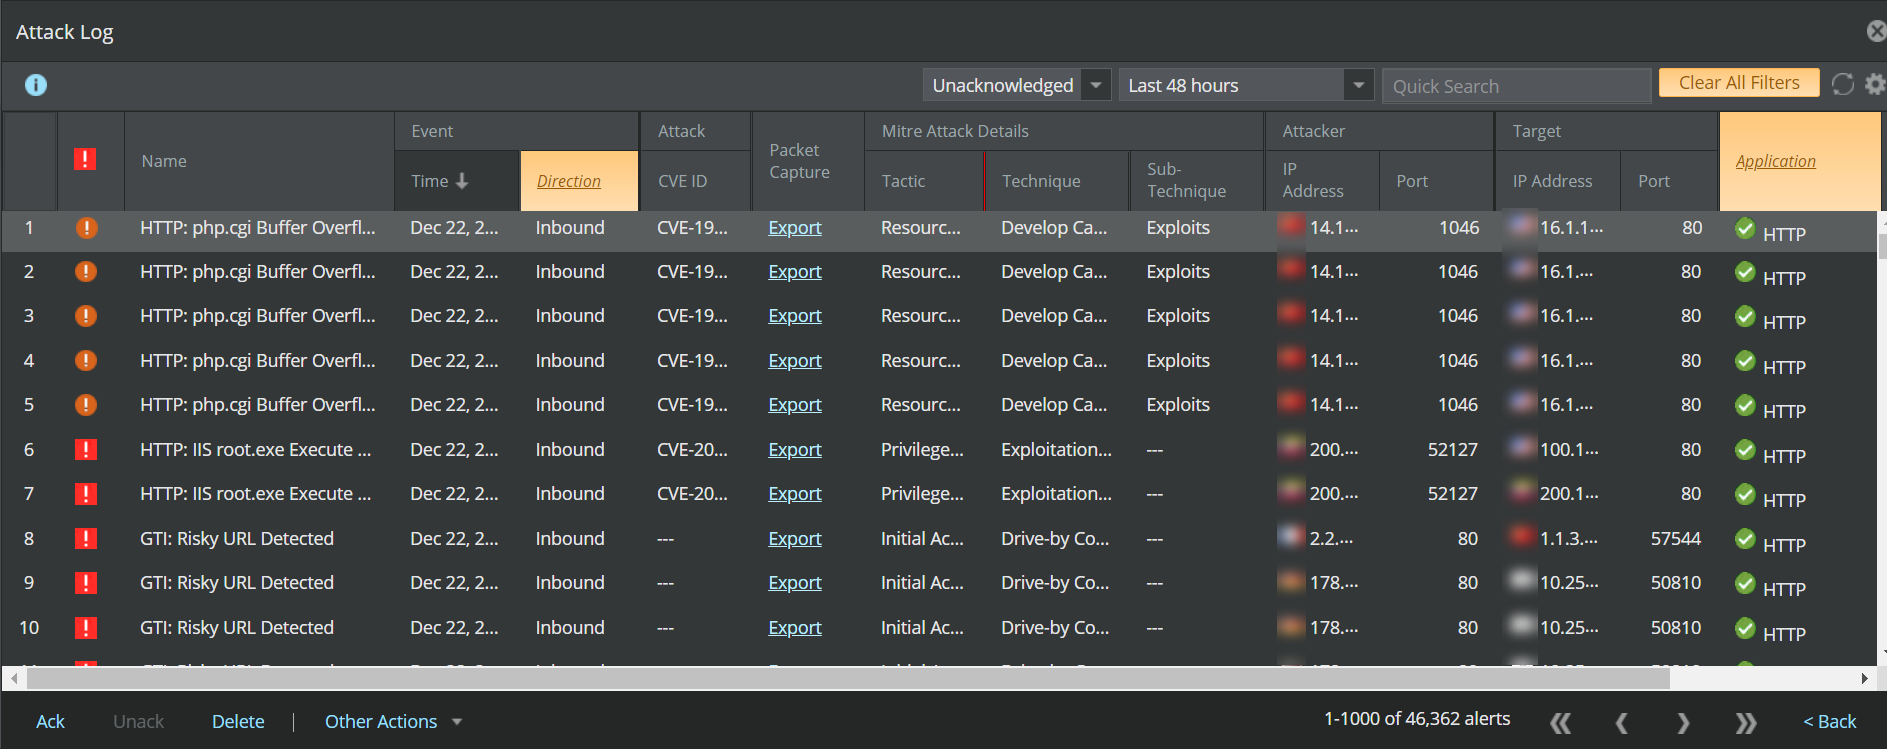
Note
The filter criteria is already applied when you are on Threat Explorer via the Dashboard page. If you navigate directly from Analysis tab, the Threat Explorer page does not have any filters.
For more details on filters, refer to section Add a filter.