IPv6 packets can pass through IPv4 networks when they are encapsulated in an IPv4 packet. By a similar way, IPv4 packets can also pass through IPv6 networks. This method of encapsulating a packet within another packet of a different protocol to enable the packet to pass through incompatible networks is called as tunneling.
NS-series Sensors support 4 types of tunneled traffic. That is, these 4 types are parsed for attacks:
IPv6 in IPv4
IPv6 in IPv6
IPv4 in IPv6
IPv4 in IPv4
Multi-level tunneled traffic is not supported. That is, the packets are allowed to pass through but are not parsed for attacks.
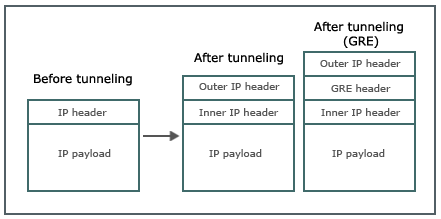
Note that an outer IP header is inserted after tunneling, and it contains the tunnel (that is, intermediate) source and destination IP addresses. In case of Generic Routing Encapsulation (GRE) tunneled traffic, an additional GRE header is inserted. The inner header contains the actual source and destination IP addresses.
The following are some key points regarding how the Sensors handle tunneled traffic:
The Sensor follows the traffic according to the inner header to detect attacks. Therefore, the alerts, dashboards, reports and so on display the details from the inner header. Also, the exception objects are applied on the inner header.
In case of CIDR subinterfaces, the Sensor uses only the IPv4 header to determine to which CIDR the traffic belongs to. In case of IPv4 in IPv6, it is determined based on the inner IPv4 header. In case of IPv4 in IPv4, it is based on the outer IPv4 header.
If you have configured Firewall, note that Firewall access rules are applied only to the outer header. Also, the destination IP protocol number should be set to 4 or 41 for tunneled traffic and 47 for GRE tunneled traffic in the Firewall access rules.
TCP resets to the source or destination host at the time of detection include the outer header as well as the inner header. TCP reset from an alert through SNMP is not supported for tunneled traffic. Reset unfinished three-way handshake option does not work for tunneled traffic.
Only IPv4 traffic is parsed for DoS attacks. For tunneled traffic, Sensors use the inner IP header to detect DoS attacks. Therefore, DoS attack detection for tunneled traffic is applicable only if the inner IP header is an IPv4 header.
All NS-series Sensor models can parse GRE tunneled traffic:
The other Sensors simply allow the GRE tunneled traffic to pass through.
Only GRE version 0 is supported.
GRE traffic with sequence number options is just forwarded without being parsed.
GRE traffic with routing headers is just forwarded without being parsed.
For Sensors in fail-over mode, you need to enable tunneling on both the member Sensors for GRE tunneled traffic to be parsed.
Note
Tunneling is disabled by default.
The following CLI command is available for tunneling:
show parsetunneledtraffic status:To know the current tunneling configuration status of a Sensor.
For details, see the CLI commands section.