Once you have verified that a custom attack is published in a rule set, you need to update the Sensors of the changes for the Sensors to look for traffic matching the attack definition. Since addition of a custom attack affects one or more rule sets, which in turn affects one or more policies, your policies may require updating across all of your Sensors in order for effective detection of your attack definition.
The Device Configuration Changes action sends configuration changes, signature updates, and policy changes to all of the devices under the Devices node.
Note
The Device Configuration Changes action updates multiple Sensors, but only transmits the update to one device at a time.
To update the configurations of multiple devices, perform the following steps:
Select Devices → <Admin Domain Name> → Global → Device Manager.
The Device Manager page is displayed.
Select the Sensors tab. Then, select the Sensor(s) to be updated from the list.
Note
You can also do it at the device level by selecting Devices → <Admin Domain Name> → Devices → <Device Name> → Deploy Pending Changes.
Click Sync. The Bulk Sync window is displayed. Select the required configurations and click Sync.
Bulk Sync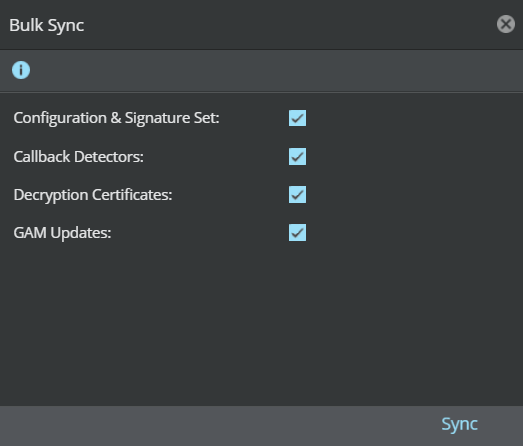
A Snort Custom Attack definition being applied to a Sensor port depends on the following:
The attack definition should be published in the corresponding policy.
The attack definition type that you have specified.
You should have specified the corresponding Target Device for the attack definition. That is, if it is an NS-series Sensor port, you should have selected NS-series as the Target Device for the attack definition.