Trellix vIPS for Azure is a GWLB-based solution that is capable of inspecting traffic flowing into and out of protected Azure instances. The solution has been designed to adapt to a public cloud environment and to scale with the requirements of your organization's network.
Deployment of Trellix vIPS can be fulfilled to suit your requirements based on the direction of traffic and inspection mode. In this section, we provide you with some scenarios which can serve as basic guidelines for your deployment.
Consider a scenario where Trellix vIPS is deployed to protect an organization's assets in the Azure environment. We assume that some of these assets to be protected are web servers with public IP addresses and that you have performed the following steps as part of the deployment:
Ensure that the Manager is:
Installed in the Azure environment
Able to reach required Clusters in the Azure environment
The vIPS Cluster is configured and the communication to the Manager is successful.
A Cluster and the associated VM groups are configured in the Manager.
Ensure that the traffic from the protected VMs is redirected to GWLB.
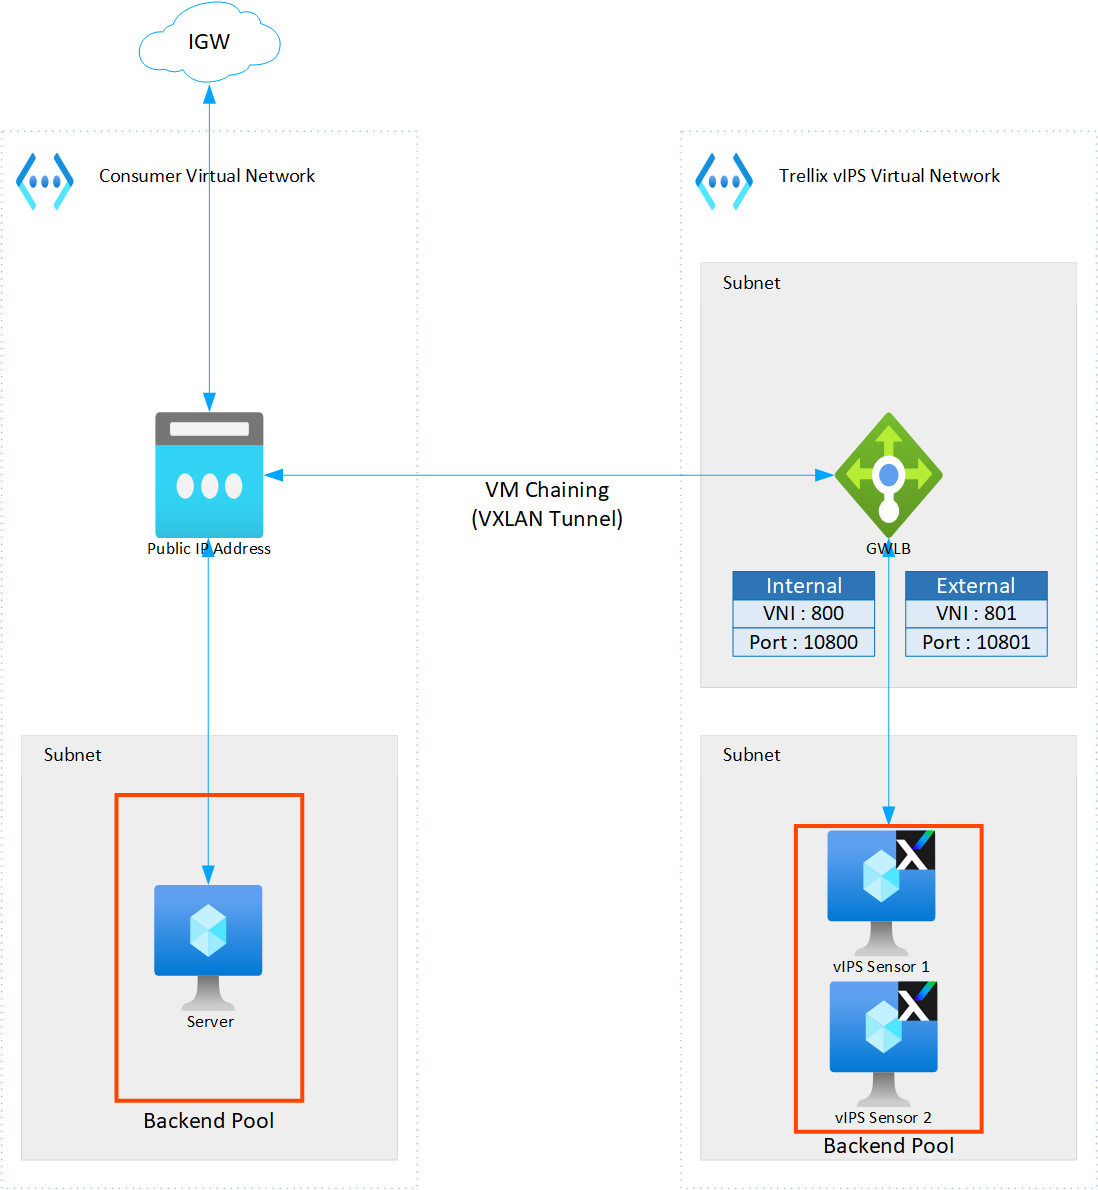
Scenario 1: Deployment of Gateway Load Balancer with Virtual Machine Chaining
Deploy the instances and connect them using VM Chaining.
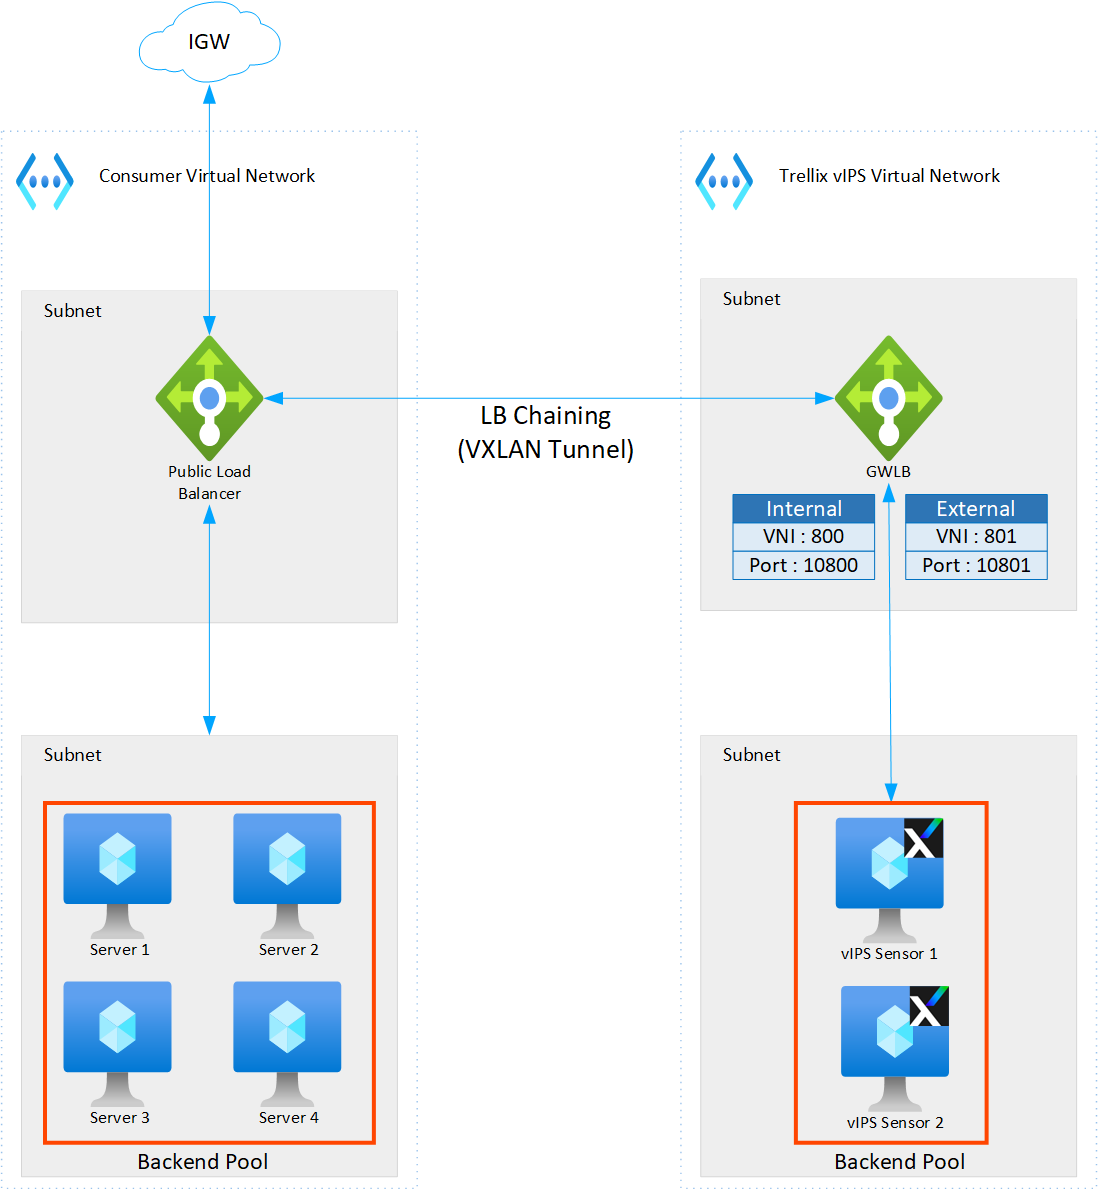
Scenario 2: Deployment of Gateway Load Balancer with Public Load Balancer Chaining
Deploy the instances and connect them using LB Chaining.
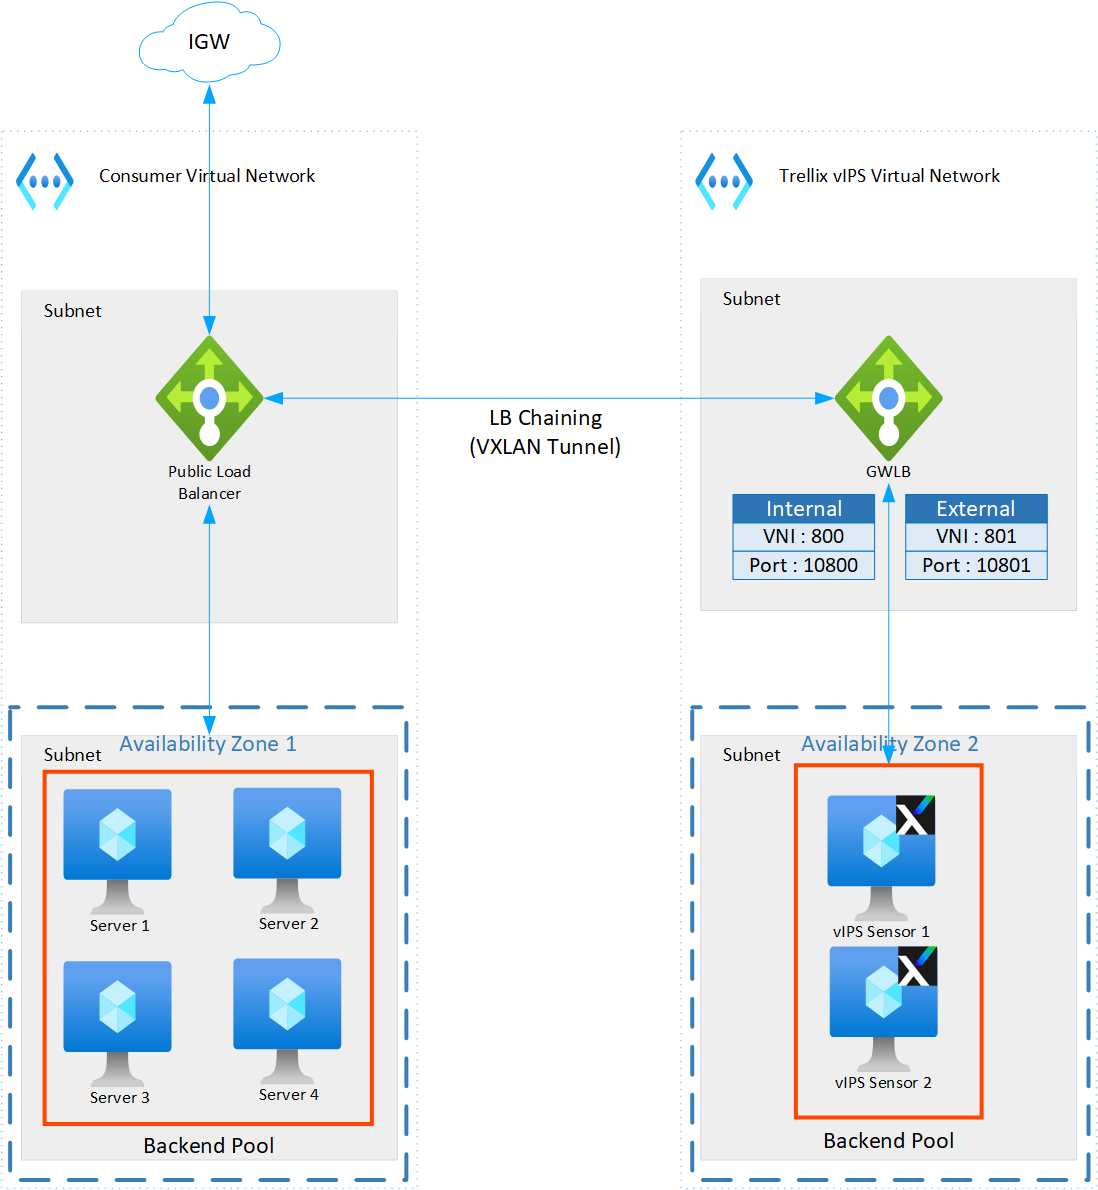
Scenario 3: Multi-zone deployment with Gateway Load Balancer
Deploy the instances across multiple zones and secure them using LB or VM Chaining.
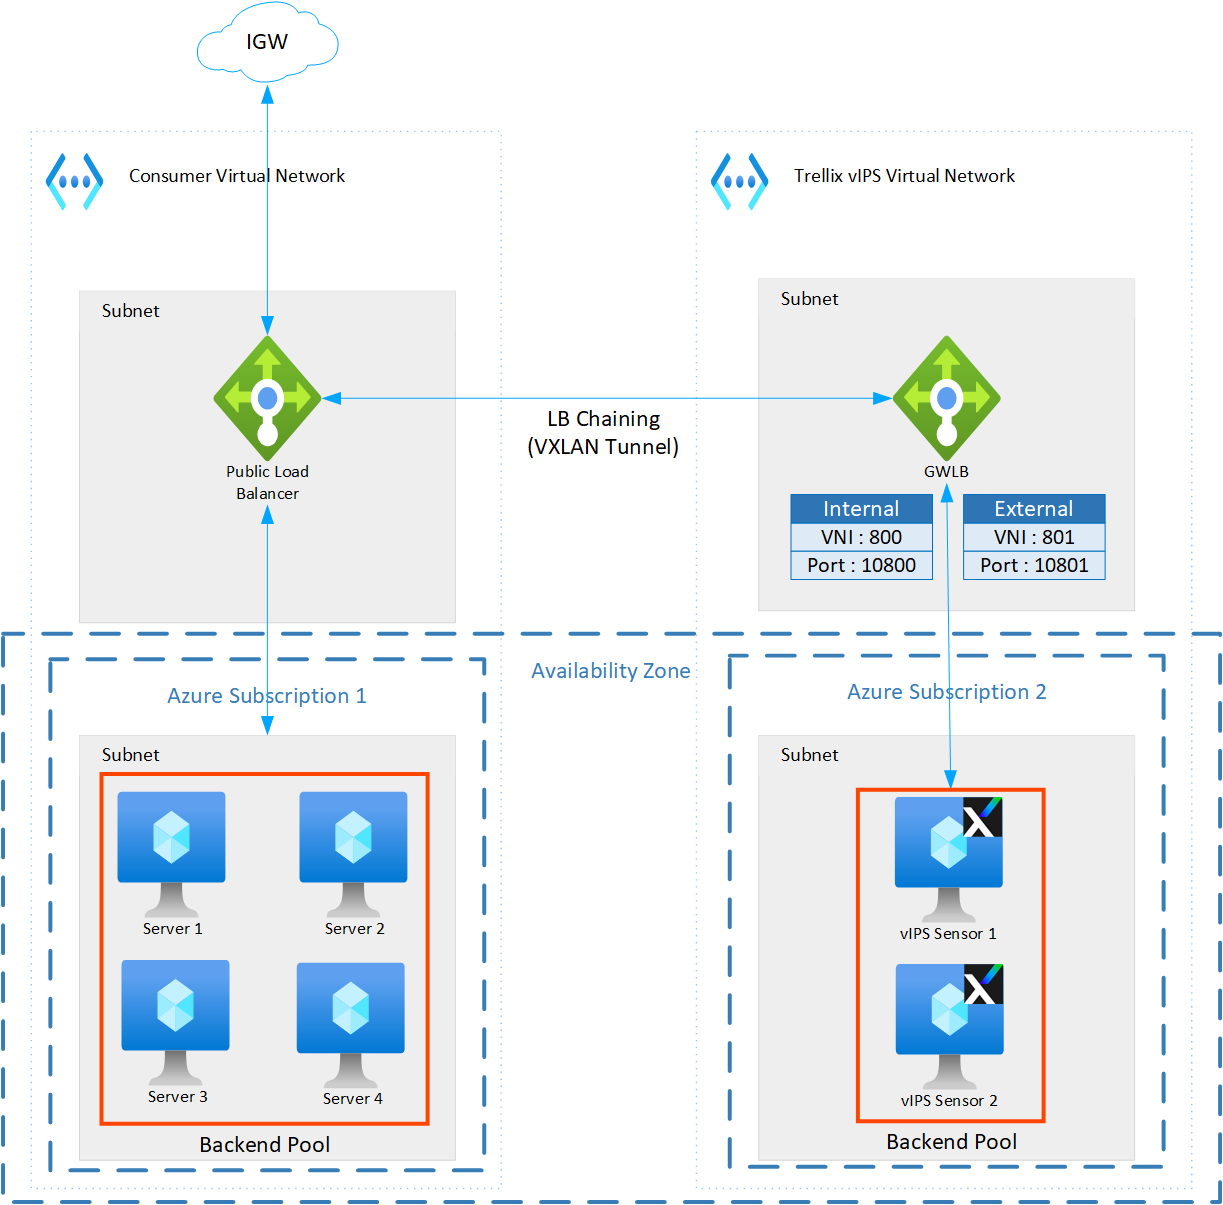
Scenario 4: Securing multiple Azure subscriptions
Deploy the instances across multiple Azure subscriptions and secure them using LB or VM Chaining..