Below are few use case scenarios for outbound SSL decryption:
With re-signing certificate imported to the browser
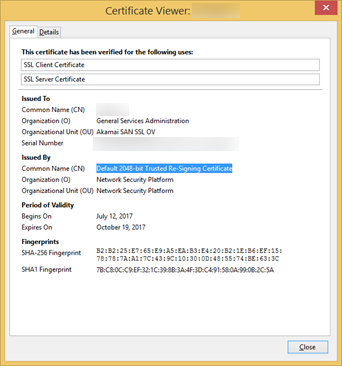
When the client initiates a request to the web server, the Sensor intercepts the traffic and initiates connection to the web server. For example, when you initiate a request from a secure Amazon website to the Amazon web server, the Sensor intercepts the connection from the website and initiates a connection with the web server. The connection from the web server is checked against the trusted CA list by the Sensor. The re-signing certificate must be exported from the Manager and installed in the browsers’ certificate store to initiate a secure connection. This is the re-signing certificate that the Sensor uses on the server's behalf when establishing connection with the client. In the process, the Sensor decrypts the traffic before sending it to the client. You can view the re-signing certificate from the Sensor by viewing the issuer name in the servers’ certificate list of the browser. Once the connection is established, the Sensor inspects the traffic between the client and web server.
Without certificate in the trusted list of the Sensor
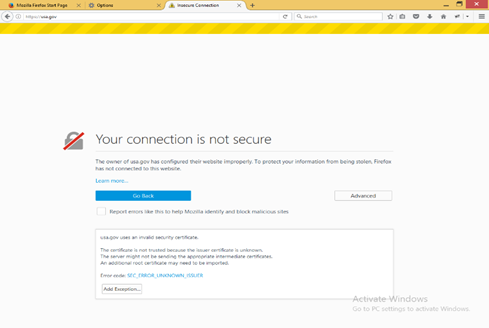
When a request from the client is sent to the web server, the Sensor intercepts the traffic and initiates a connection to the web server. If you have the failure handling configured to decrypt the flow when the certificate is untrusted/absent, a warning pops up in the browser stating that the connection is not secure. You can either proceed to the website or add the website as an exception. This happens when the certificate is not present in the trusted CA list. For the connection to establish, the certificate of the server must be present in the trusted CA list. When you add a website as an exception, the certificate will not be uploaded in the browser. The Sensor decrypts the traffic, but will not be inspected for malicious activity.