Traffic Mirroring is an Amazon VPC feature that you can use to copy network traffic from an elastic network interface of type interface.
The following are the key components of Traffic Mirroring:
Source - Includes a network interface to monitor
Target - It is the destination for a mirrored traffic
Filter - Used to define a set of rules to mirror the traffic
Session - Used to establish a relation between source, filter, and target
How does the AWS Traffic Mirroring work?
A traffic mirror session establishes a relationship between a traffic mirror source and a target. Traffic mirror sessions are evaluated based on the ascending session number you define while creating the session.
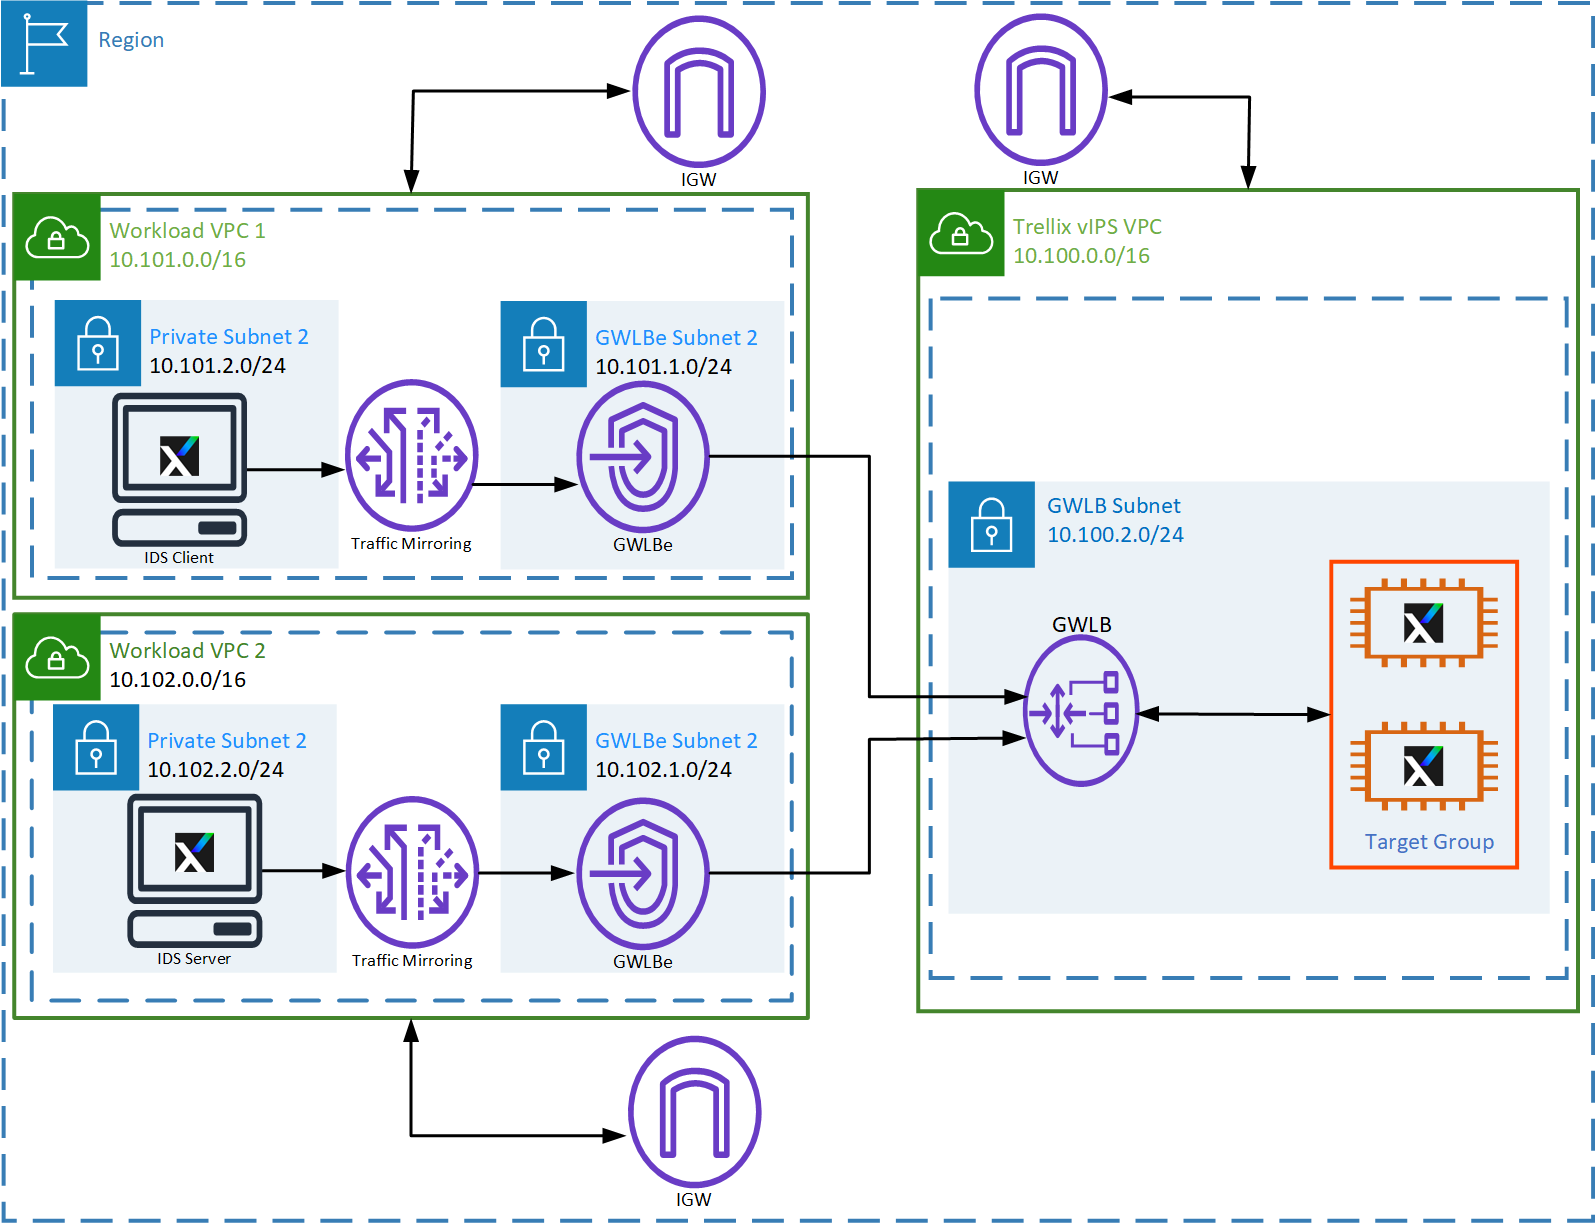
Create a Traffic Mirroring Target
Log in to the AWS console, and navigate to Services → VPC.
In the Region selector, choose the same AWS Region as your VPCs.
In the navigation pane, under Traffic Mirroring, choose Mirror targets.
Now, select Create traffic mirror target.
Create traffic mirror target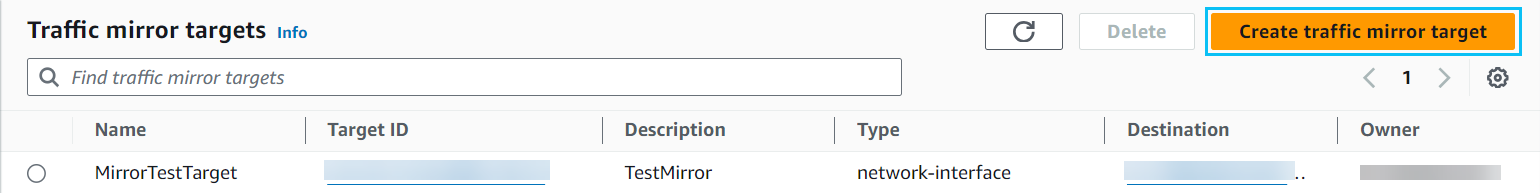
The Create traffic mirror target page is displayed. In the Target settings section provide the following details:
[Optional] Name tag - Name of the traffic mirror session
[Optional] Description - Description for the traffic mirror session
Target settings section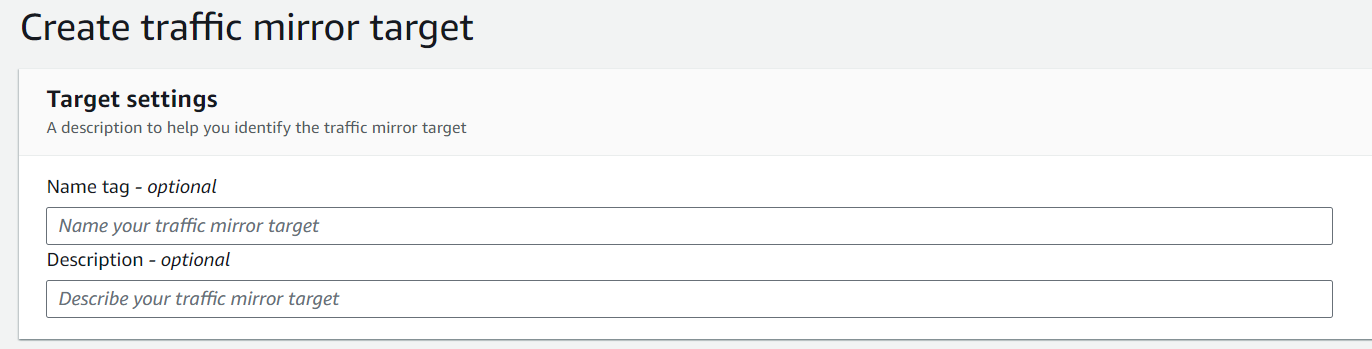
In the Choose target section provide the following details:
Target type - Select the Gateway Load Balancer Endpoint as the target type from the drop-down
Target - Select the target destination
Choose target section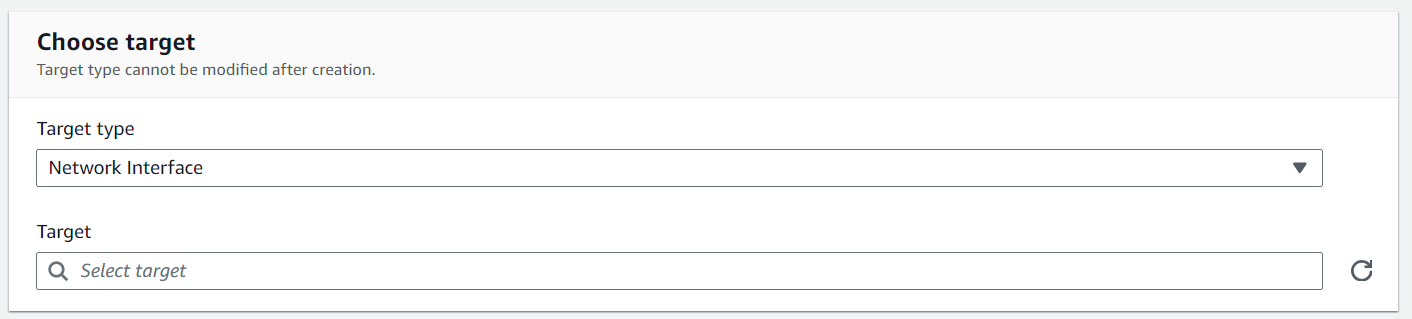
[Optional] In the Tags section, provide a tag to be associated with the resource.
Tags section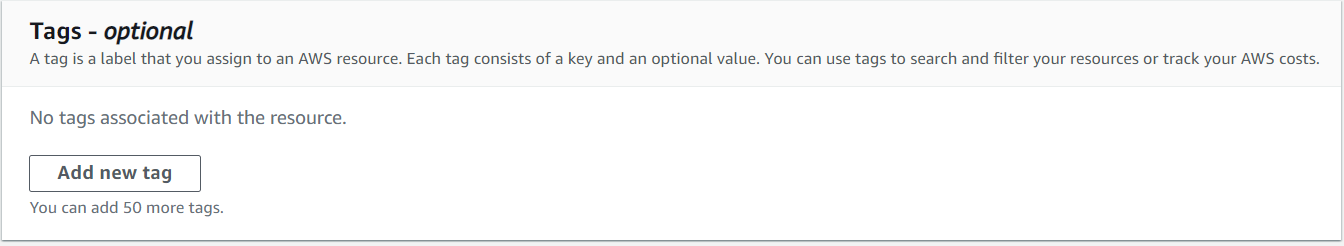
Next, click Create.
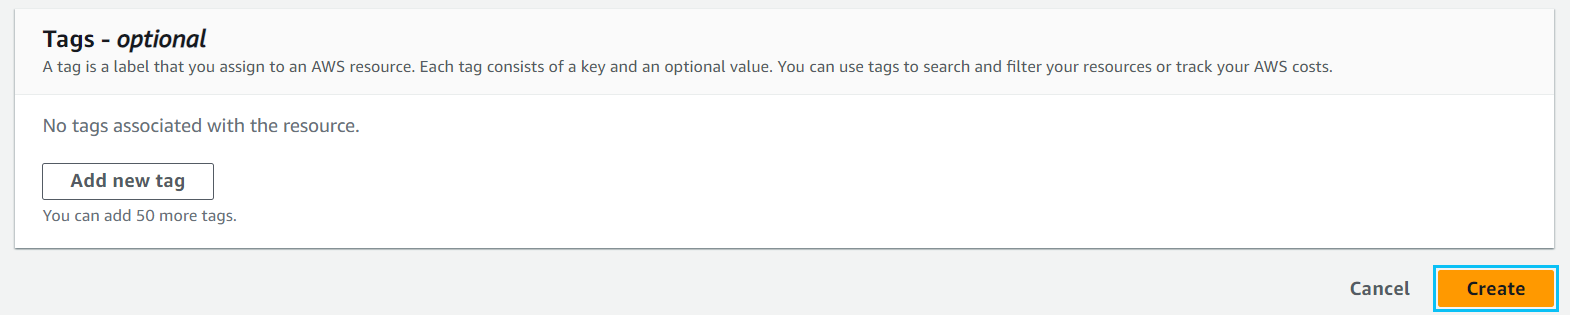
For more information, see Traffic mirror targets.
Create a Traffic Mirroring Filter
Log in to the AWS console, and navigate to Services → VPC.
In the Region selector, choose the same AWS Region as your VPCs.
In the navigation pane, under Traffic Mirroring, choose Mirror filters.
Now, select Create traffic mirror filter.
Create traffic mirror filter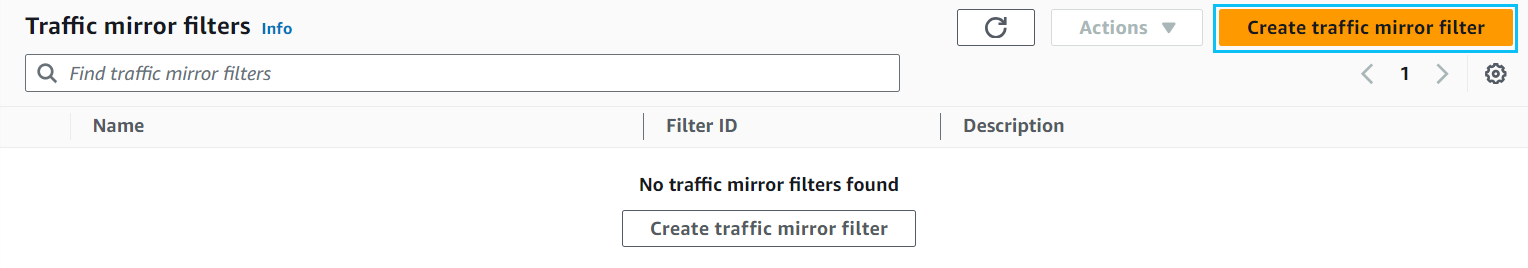
The Create traffic mirror filter page is displayed. In the Filter settings section provide the following details:
[Optional] Name tag - Name of the traffic mirror session
[Optional] Description - Description for the traffic mirror session
Filter settings section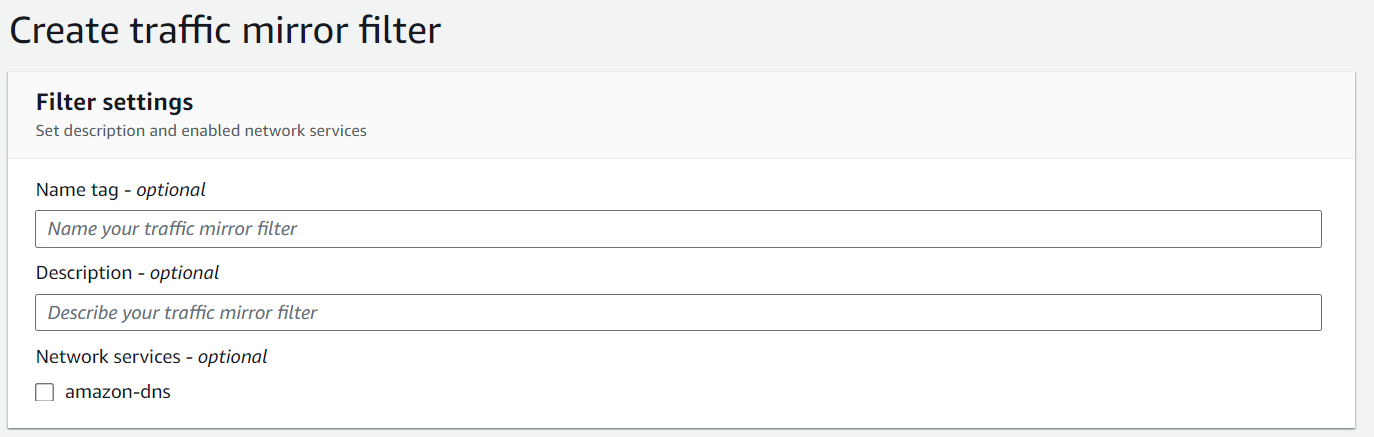
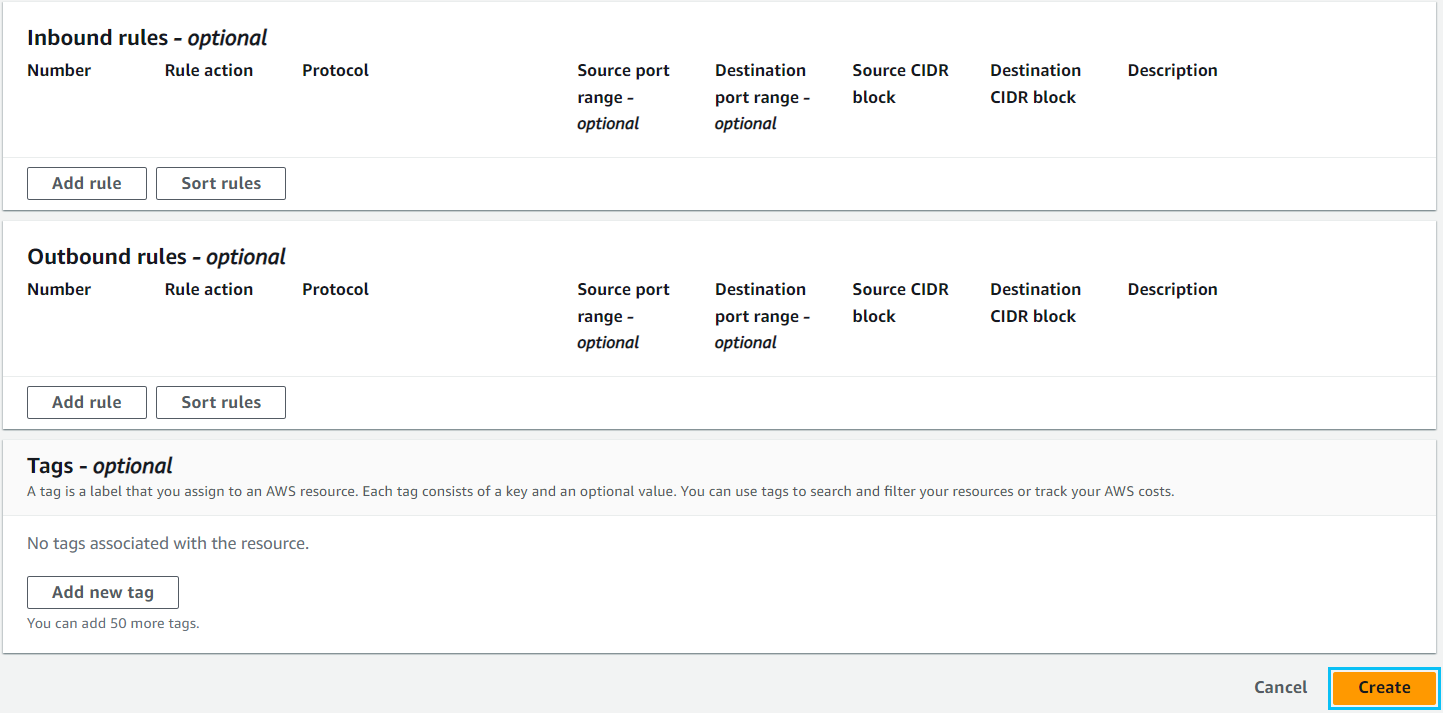
[Optional] Configure the required Inbound and Outbound rules.
[Optional] In the Tags section, provide a tag to be associated with the resource.
Next, click Create.
For more information, see Traffic mirror filters.
Create a Traffic Mirroring Session
Log in to the AWS console, and navigate to Services → VPC.
In the Region selector, choose the same AWS Region as your VPCs.
In the navigation pane, under Traffic Mirroring, choose Mirror sessions.
Now, select Create traffic mirror session.
Create a traffic mirror session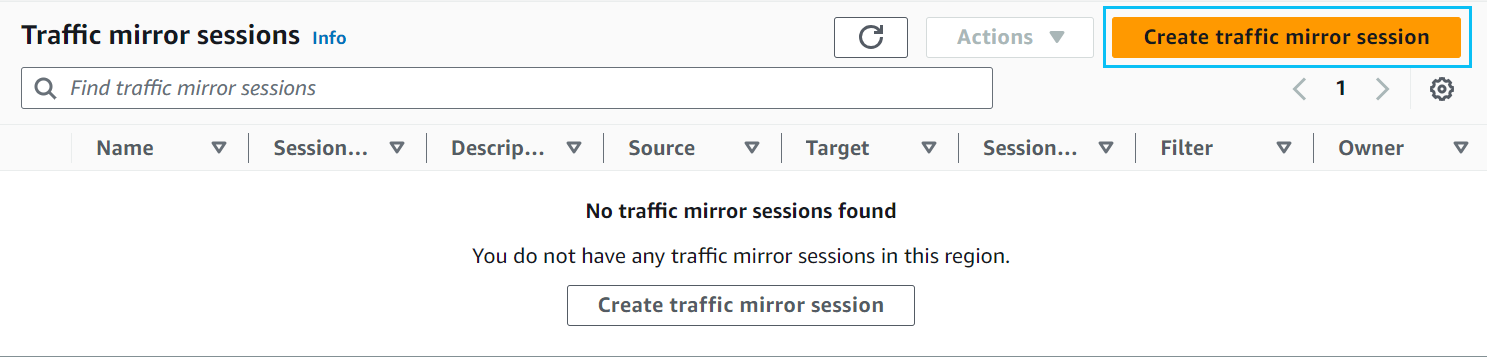
The Create traffic mirror session page is displayed. In the Session settings section provide the following details:
[Optional] Name tag - Name of the traffic mirror session
[Optional] Description - Description for the traffic mirror session
Mirror source - Select the required network interface for the mirror source
Mirror target - You can either choose an existing traffic mirror target from the drop-down or choose Create target. For more information, see Create a Traffic Mirroring Target.
Session settings section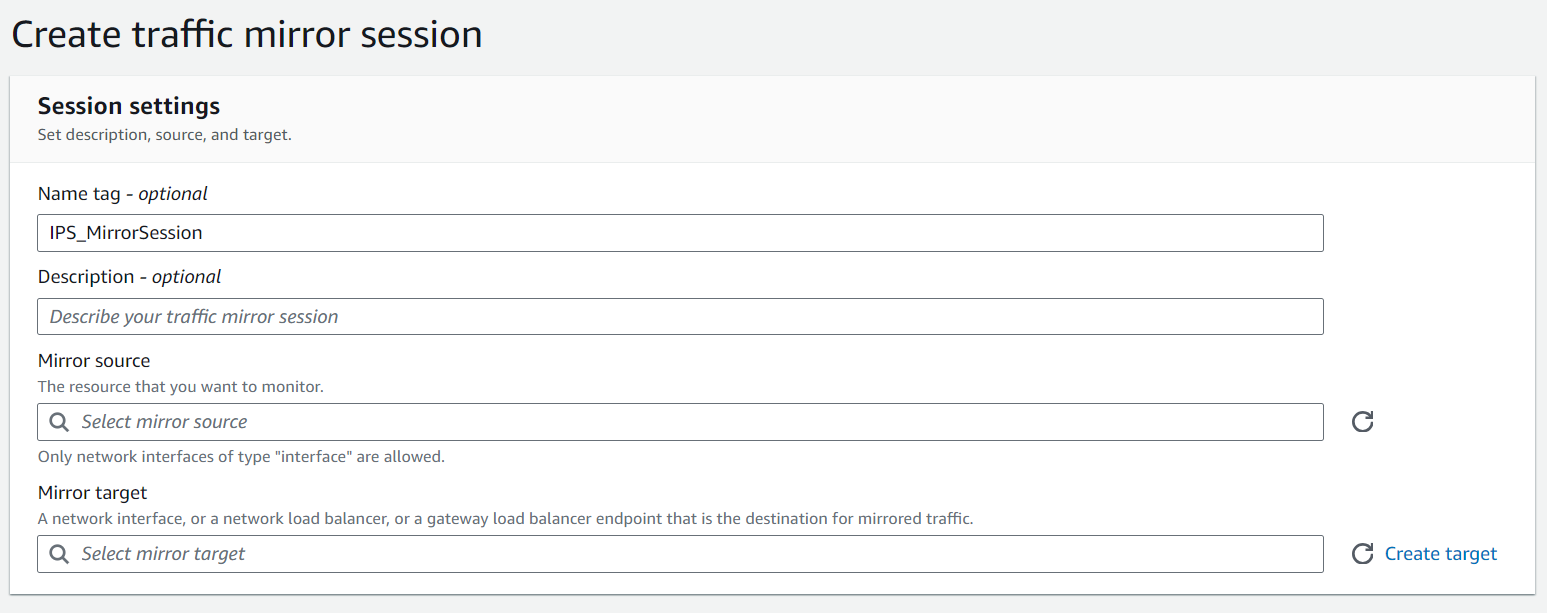
Go to Additional settings and provide the following details:
Session number - Provide a valid session number
Filter - You can either choose an existing traffic mirror filter from the drop-down or choose Create filter. For more information, see Create a Traffic Mirroring Filter.
Additional settings section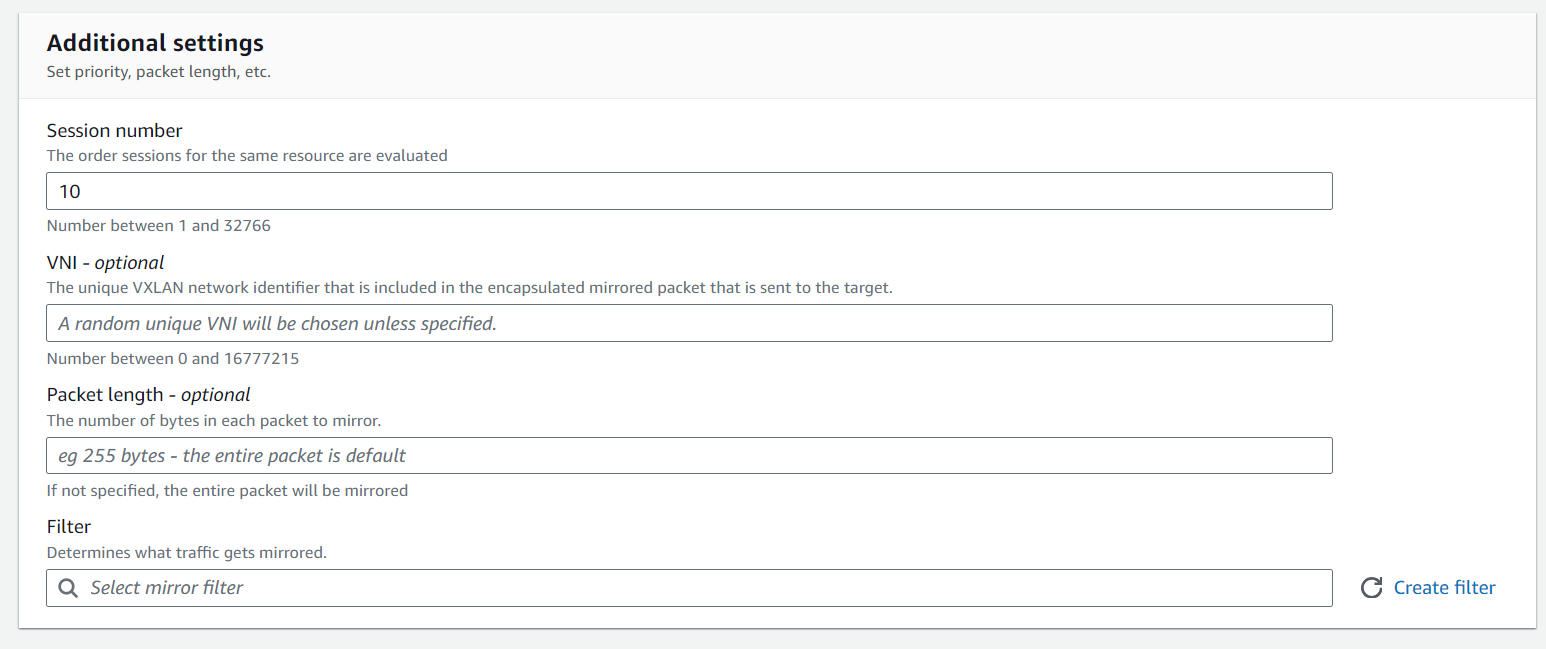
[Optional] In the Tags section, provide a tag to be associated with the resource.
Tags section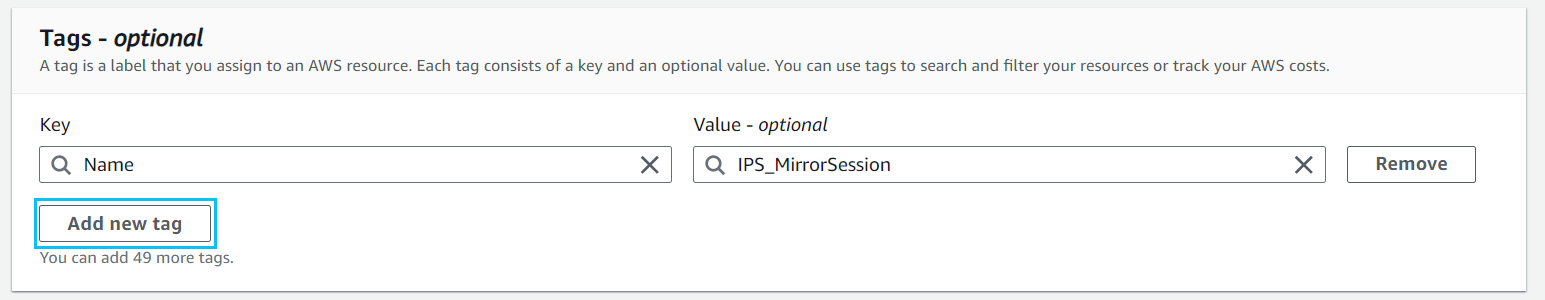
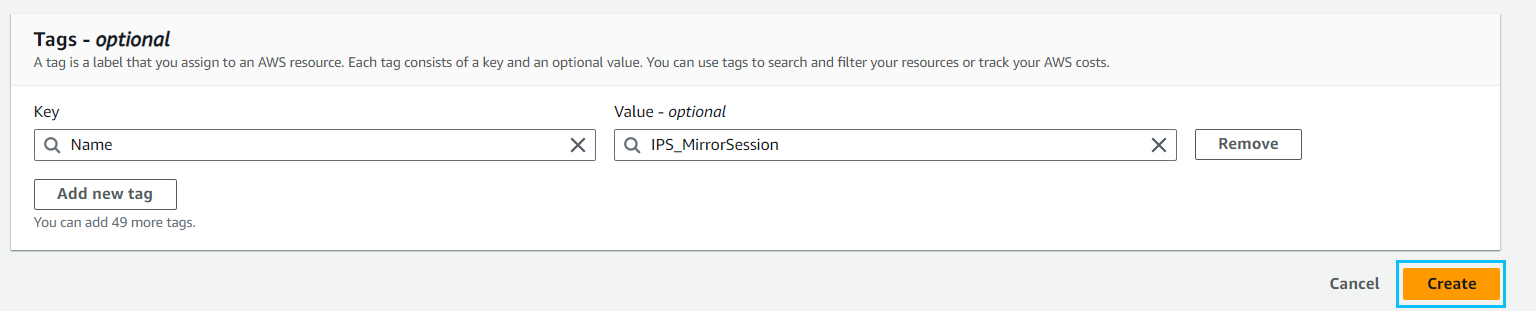
Next, click Create.
For more information, see Traffic mirror sessions.