Effective Firewall rules is a sequential list of access rules that a Sensor checks in a top-down fashion against the traffic that it sees at a port/port pair, interface, or subinterface. Afer you assign Firewall policies to the required Sensor resources, the Manager collates all the rules from these policies and creates the list of effective Firewall rules for each port/port-pair, interface, and subinterface. It creates separate lists for inbound and outbound traffic.
Note
In all effective Firewall rules list, the Manager adds a default entry at the bottom that allows all traffic with IPS inspection. You cannot modify or delete this default entry. If you do not assign any Firewall policy to any of the resources of a Sensor, this default entry is applied at all ports/port pairs, interfaces, and subinterfaces. Firewall logging is not applicable to this entry.
The order of the rules in the list of effective Firewall rules is based on the hierarchy of Sensor resources. That is, the rules of the pre-device Firewall policy are listed on top followed by the rules of the interface or subinterface policy, then followed by the port-level policy, and finally the post-device level policy. You can view the inbound and outbound effective Firewall rules for a port/port-pair, interface, and subinterface.
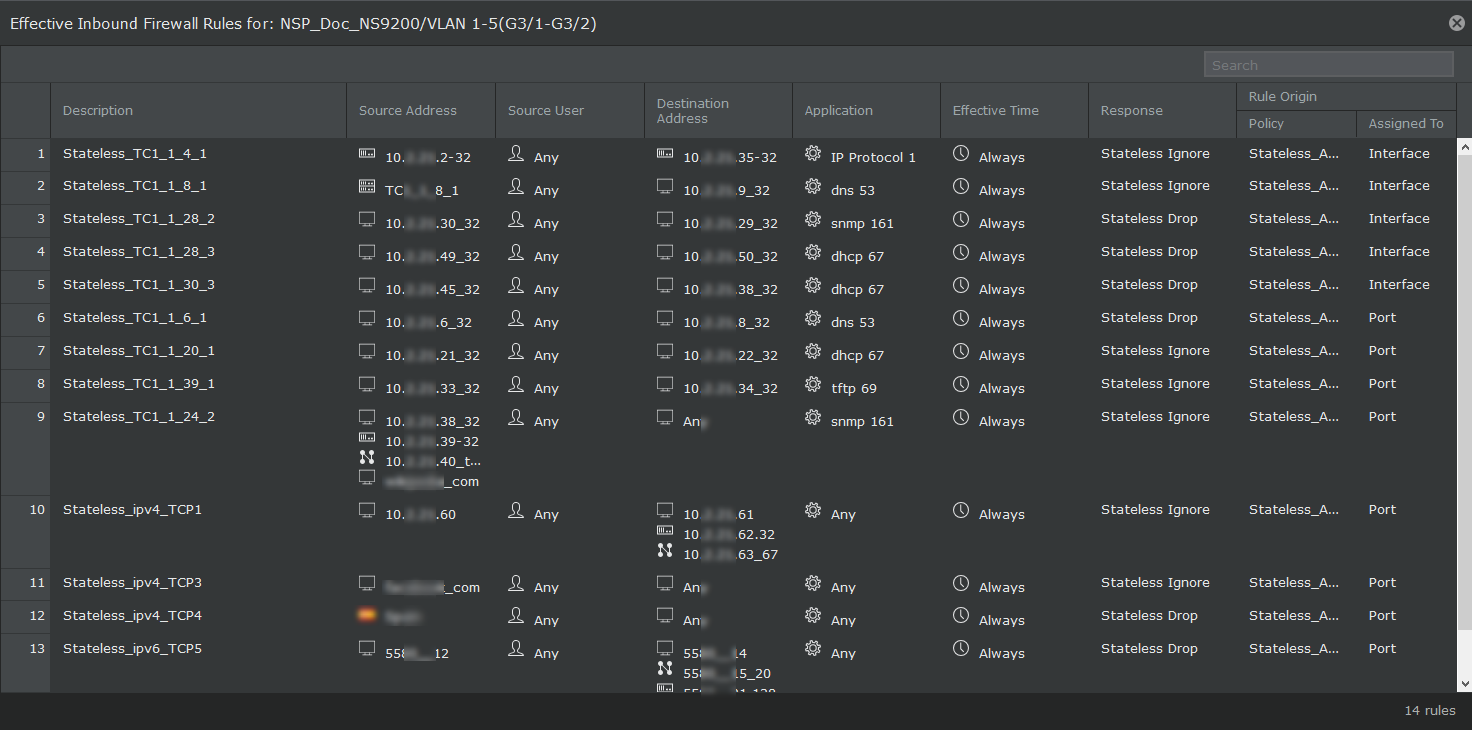
The fields displayed are:
Field | Description |
|---|---|
# | The order of the rule in the policy. |
Description | Description of the rule, if available. |
Source Address | The source of the traffic. In case of Advanced Firewall policies, it is based on country, host name, IPv4 or IPv6 address, IPv4 or IPv6 address range, IPv4 or IPv6 network, or Network Group. For Classic policies, it is based on IPv4 address or network. |
Source User | This is displayed only for Advanced Firewall policies. Indicates the AD user name and AD user group for the user logged on the source host. |
Destination Address | The destination of the traffic. In case of Advanced Firewall policies, it can be country, host name, IPv4 or IPv6 address, IPv4 or IPv6 address range, IPv4 or IPv6 network, or Network Group. For Classic policies, it can be IPv4 address or network. |
Application | It indicates the Application, Application Group, Application on Custom Port, Service, or Service Group. |
Effective Time | Indicates the time period when the rule is effective. Shows as Always for rules belonging to Classic policies. |
Service | This is displayed only if Classic policies are applied. It indicates the service defined for the rule. |
Response | The response action to be taken by the Sensor on traffic that matches the rule. |
Rule Origin | Policy — Name of the Firewall policy to which the rule belongs. Assigned to — Name of the interface to which the policy is assigned to. |
To view the Effective Rules:
Click the Policy tab.
Select the domain from the Domain drop-down list.
Select Policy Manager. List of interfaces for the Sensors configured is displayed.
Double-click the interface of a Sensor for which you wish you view the Effective Rules. The <Device Name/Interface> panel opens.
In the Firewall section, click Inbound or Outbound option under Effective Rules to view the rules configured.
Computing the number of access rules utilized per Sensor
You can calculate the number of Firewall access rules being utilized per Sensor by adding all the rules configured at the Sensor-level, port-level, and interface or subinterface level.
Example: Computing access rules utilized per Sensor
On an NS7200 Sensor, if you configure 8 rules at the Sensor level, 20 rules on port pair G3/1-G3/2, and 10 rules on the subinterface of G3/3-G3/4, you would have utilized 38 out of the 3000 limit.
You can also calculate the number of access rules utilized by adding the number of rules displayed under Inbound Rules and Outbound Rules link at each port, interface, and subinterface level of the Sensor.
Computing the number of access rules utilized during port clustering
When port clustering (interface grouping) is used, and port-level access rules are configured, the number of access rules utilized (for each port-cluster-level access rule) will be different based on the participant port-types of the cluster. One rule will be consumed per each inline port-pair member, and one rule will be consumed per each SPAN port member of the port cluster.
Examples: Computing the effective access rule utilization for each port-level access rule defined for a port-cluster
Port cluster 1: If your port cluster consists of G3/1-G3/2 (inline, fail-open), G3/3 (SPAN), and G3/5-G3/6 (inline, fail-close), 3 rules will be consumed for each rule configured at the port level.
Port cluster 2: If your port cluster consists of G3/1 (SPAN), G3/3 (SPAN), G3/5 (SPAN), G3/7-G3/8 (inline, fail-close), 4 rules will be consumed for each rule configured at the port level.