The Endpoint Executables page on the Analysis tab provides a snapshot of all the executables running on your internal endpoints that have made network calls. It also provides network visibility on how many endpoints are running the executables, how many connections were made, and the events triggered by the executable during the selected timeframe.
Note
All NTBA Appliances that have EIA services running on them will be displayed in the Devices drop-down list. You can filter data based on the NTBA Appliance selection.
The executables listed here are processes and files. They can be allowed, blocked, and unclassified. You can use this page to investigate further on what factors led to the classification of the executable and manually change the classification.
By default, the order is sorted by the endpoints, so executables with most endpoint connections are displayed first.
Note
Maximum number of executables displayed on the Endpoint Executables page is 4096. Historical data and inactive executable data are kept for 30 days.
The page is divided into the Executable panel and the Details panel. Click a row in the Executable panel to view additional information about the executable hash in the Details panel.
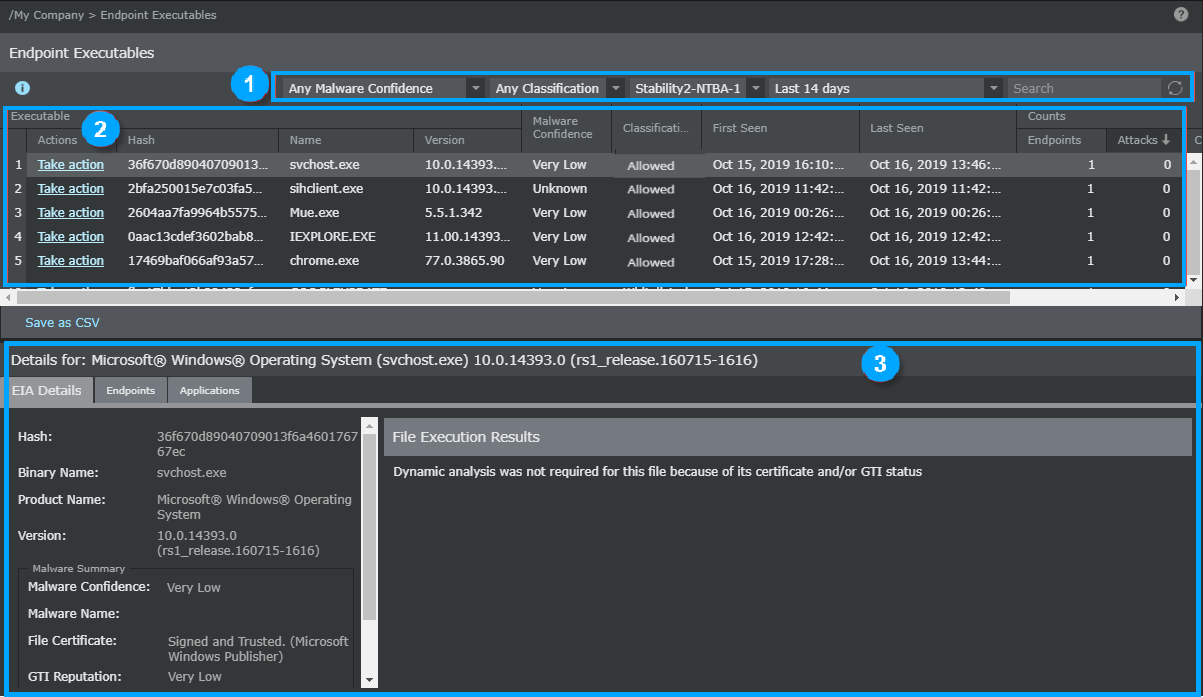
Item | Description |
|---|---|
1 | Filters and Search options |
2 | Executable panel |
3 | Details panel |
Following are the filters and search option available:
Field | Description | Default Value |
|---|---|---|
Malware Confidence |
| High+ Malware Confidence |
Classification |
| Any Classification |
Devices | Displays the list of NTBA Appliances that have EIA services running on them | Displays device names in the alphabetical order |
Time interval |
| Last 12 hours |
Search | Allows you to search executable by the file hash or the binary name of the executable | Blank |
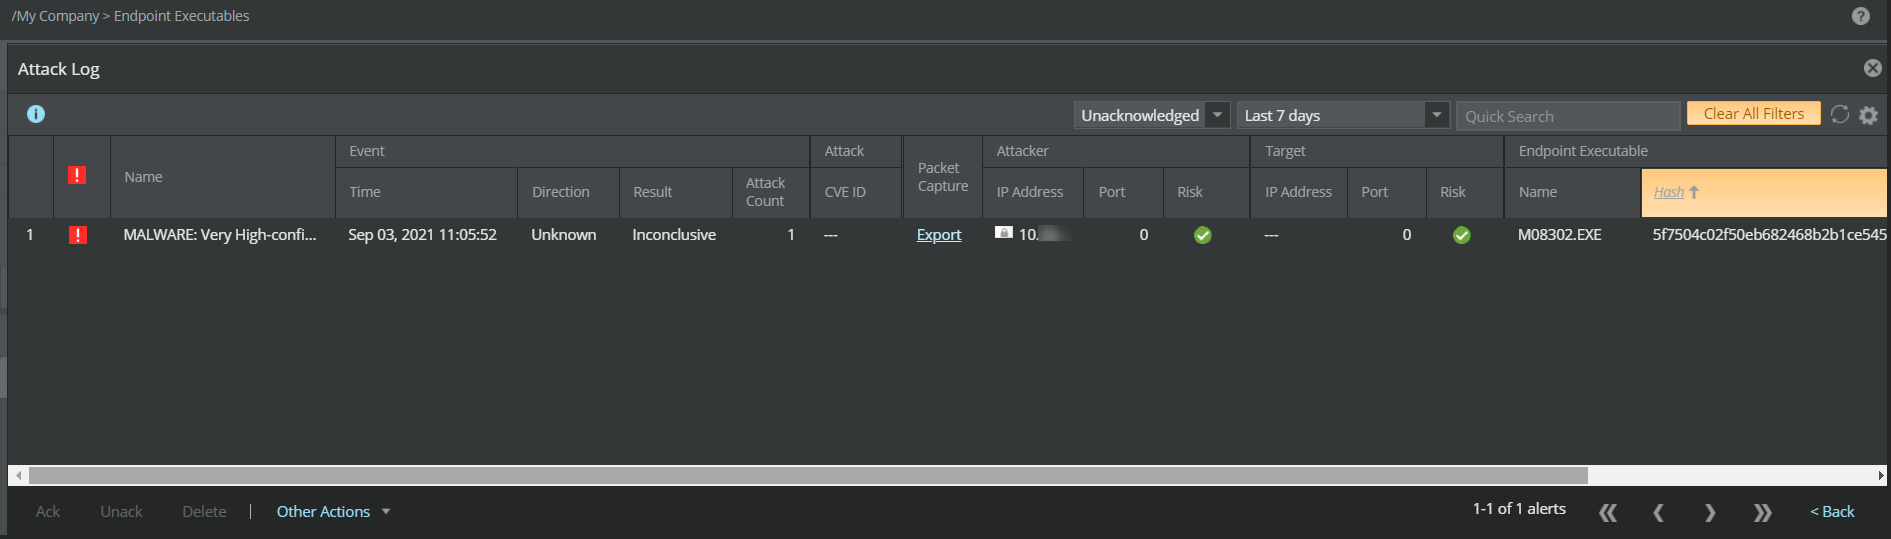
Attack Log
Upon double-clicking on any executable hash, you navigate to the Attack Log page. You can analyze and view alerts related to the selected hash.
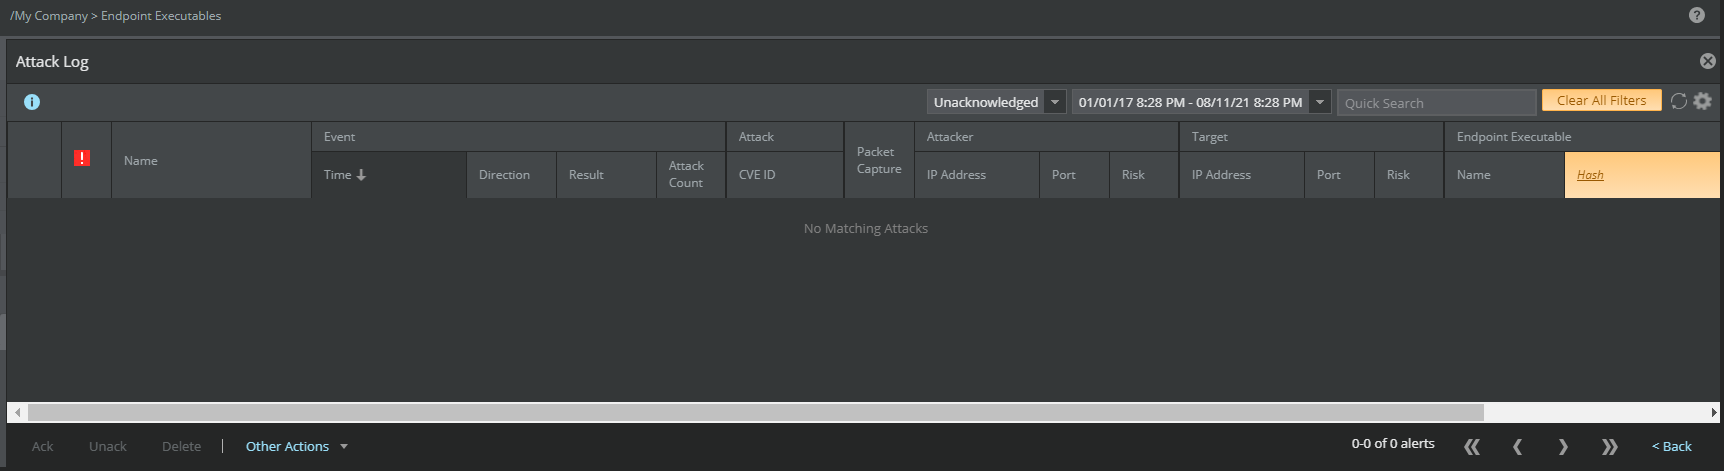
The date and time filter used in the Endpoint Executables page is persisted upon navigating to attack log. To close the attack log, click Back or  icon.
Manage Allow and Block lists
The Manage allow and block lists is a link to the File Hashes page.
For the selected NTBA Appliance, the Executable panel consists of the following:
Option | Definitions |
|---|---|
Executable |
|
Malware Confidence | Displays the malware confidence level returned by the configured EIA. The malware confidence values are very high, high, medium, low, very low, and unknown. |
Classification | Displays the executable classification whether blocked, allowed, or unclassified |
First Seen | Displays when the executable was first reported by EIA to the NTBA Appliance for the selected timeframe |
Last Seen | Displays when the executable was last reported by EIA to the NTBA Appliance |
Counts | By default, the order is sorted by the endpoints, so executables with most endpoint connections are displayed first.
|
Comment | Reason for changing the executable classification |
Click any row to see additional information of the executable hash in the Details panel. The Details panel consists of the following:
EIA Details
This tab displays the executable or file information. This includes:
Properties — Displays the malware confidence for the executable along with malware indicators that helped determine the reputation
Executable or file details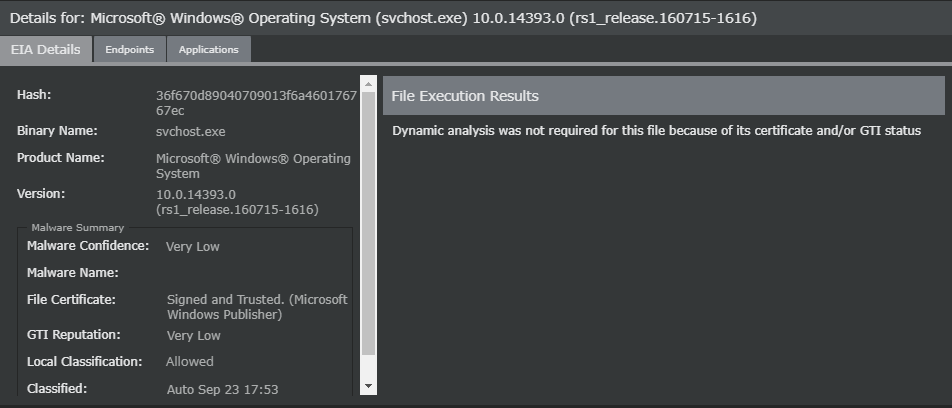 Field descriptions of EIA Details tab
Field
Description
Hash
Displays the file hash
Binary Name
Displays the binary name and the type, whether process or library
Product Name
Displays the product name for the executable or file
Version
Displays the product version number
Malware Summary
Malware Confidence
Displays the malware confidence level returned by the configured EIA. The malware confidence values are very high, high, medium, low, very low, and unknown.
Malware Name
Displays the malware name, for example, gtalk.exe
File Certificate
Displays the certificate signer and status for the file certificate, for example, Microsoft Corporation
GTI Reputation
Displays the file reputation received from GTI. Valid values are Very Low, Low, Medium, High, Very High, and Unknown.
Local Classification
Displays the executable classification whether Blocked, Allowed, or Unclassified
Classified
Displays the method of classification (Auto if the executable has been auto-classified by the NTBA Appliance or Manual if it has been manually classified) and the timestamp, only for classified executables.
File Execution Summary
Displays a summary of the tasks performed when a program was executed. Examples: connects to the internet, changes proxy settings, adds host file entries.
File Execution Details
Displays execution details as they happened
Save as CSV — Exports the list of executables in CSV format
Executable — Displays the executable name, example, gtalk.exe
Action — Displays action performed by the program, example, create_dir
Target Object — Specifies the path where this action was performed, example,
\Device\Harddisk\Users\Ellie\LocalSearch — Displays details based on search criteria
File Execution Results — Shows some of the methods and engines that were used to compute the executable reputation
Endpoints
This tab displays the list of endpoints running the executable during the selected timeframe.
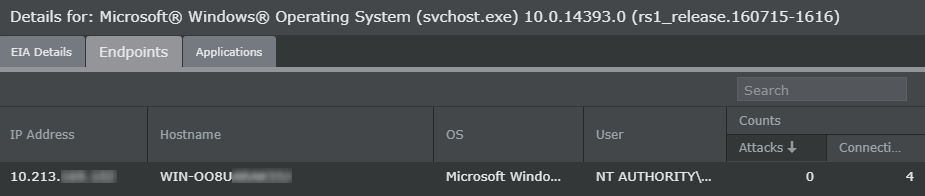
Field | Description |
|---|---|
IP Address | Displays the IP address of the endpoint |
Hostname | Displays the name of the managed host |
OS | Displays the version of the operating system running on the endpoint. For example: Windows 10. |
User | Displays the user name who invoked the executable or the DLL. The user name can include system users and local users. |
Counts |
|
The Search field allows you to search by IP address, host name, operating system, or user columns.
Double-click the IP address to view alerts related to the IP address in the Attack Log. The alerts are filtered based on the IP address selected. To close Attack Log, click Back or icon.
Applications
This tab displays the list of applications that have been invoked by the executable during the selected timeframe.
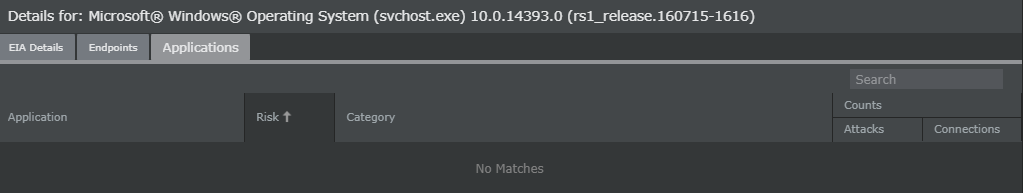
Field | Description |
|---|---|
Application | Displays the name of the application |
Risk | Displays whether the application is high, medium, or low risk. Trellix Advanced Research Center categorizes an application based on its vulnerability and the probability for it to deliver malware. |
Category | Displays the category that the application falls under. For example, HTTP falls under the Infrastructure Services category. |
Counts |
|
The Search field allows you to search by application name, risk, or category.
Double-click the application to view alerts related to the application in the Attack Log. The alerts are filtered based on the application selected. To close Attack Log, click Back or icon.