Trellix IPS Central Manager provides you with a single sign-on mechanism to manage the authentication of global users across all Managers configuration. Threat analysis tasks are performed at the Manager level and aggregated at the Central Manager. Local Managers attached to the Central Manager push new alerts and modifications into the Central Manager. These alerts are aggregated in the Central Manager Attack Log.
Alerts from the Managers managed by the Central Manager can be monitored and managed from the Central Manager. The Attack Log of the Central Manager consolidates alerts from the local Managers and displays them for monitoring purposes.
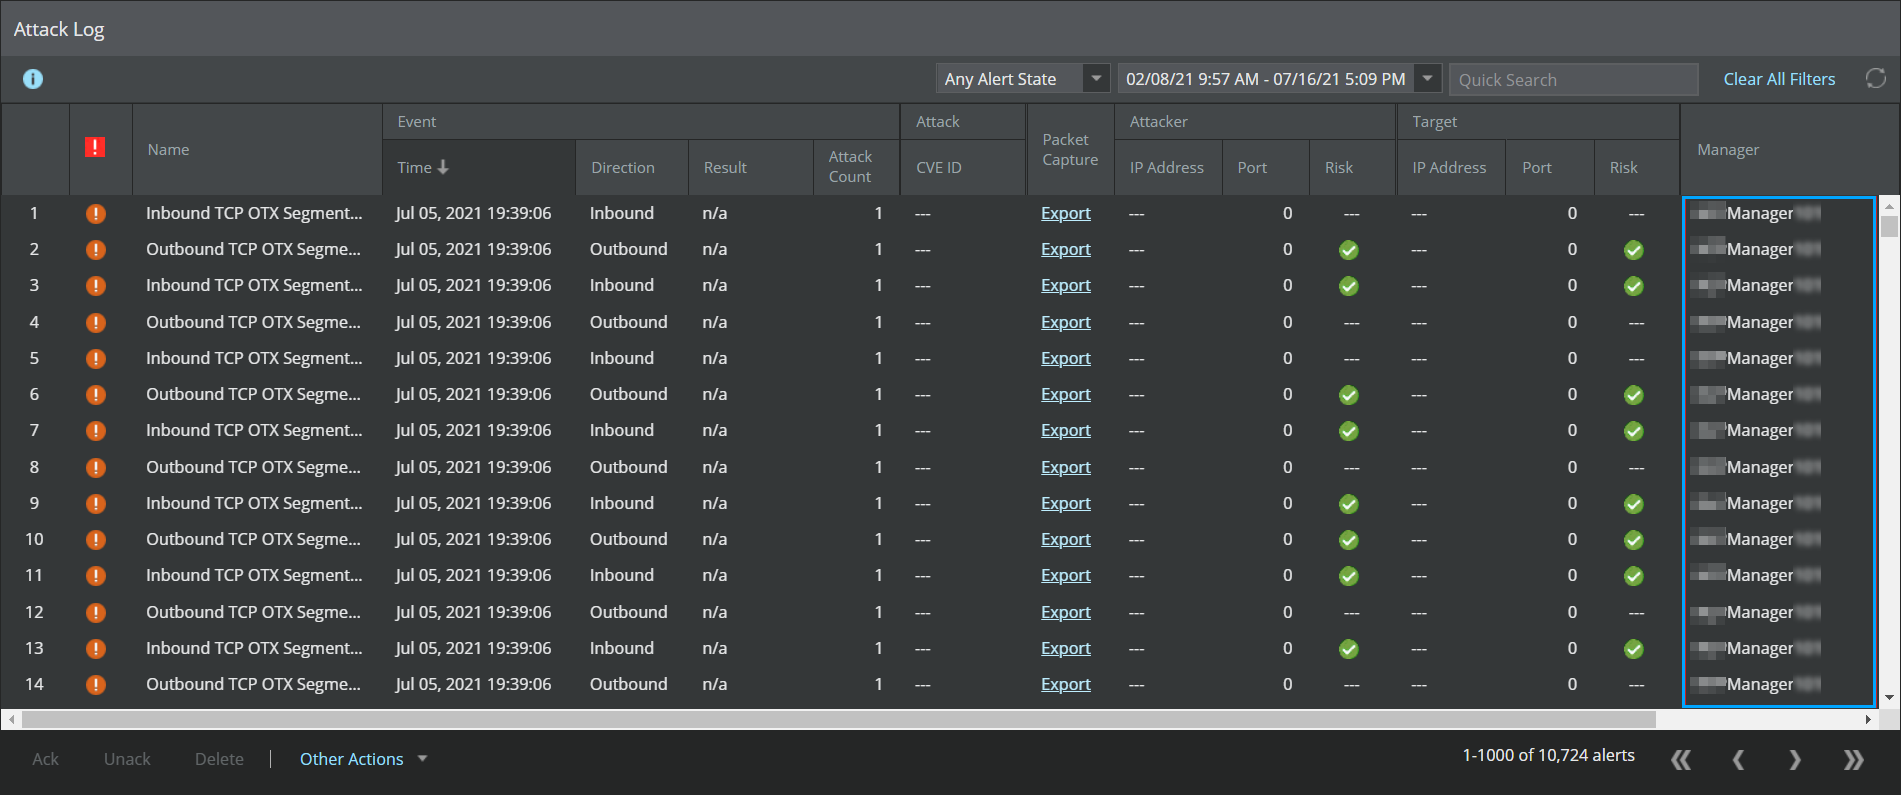
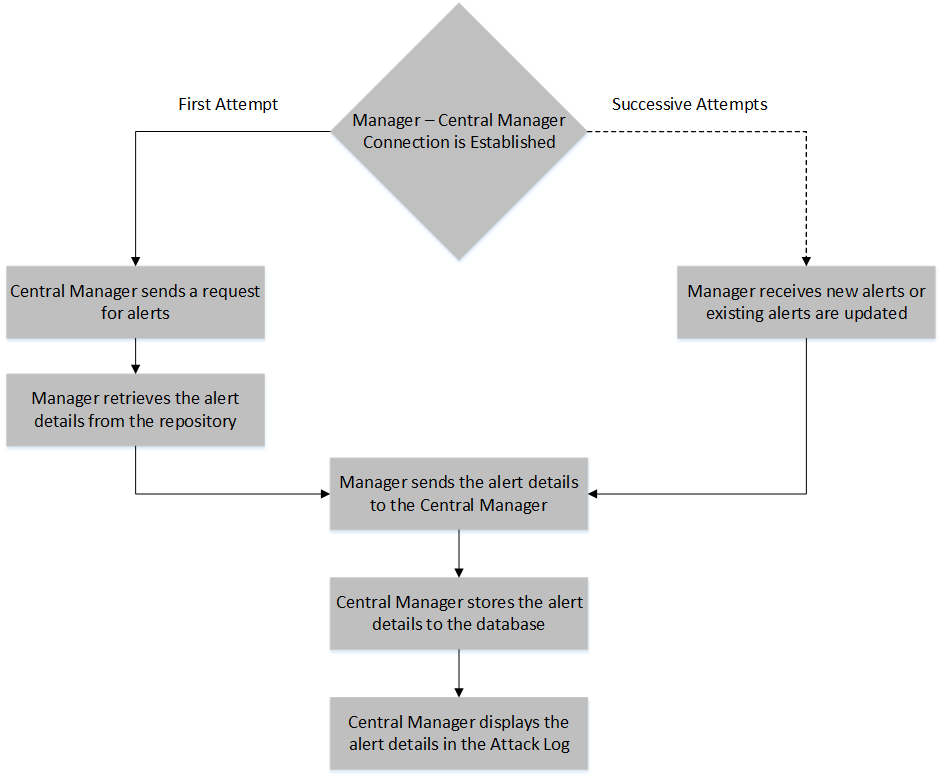
Once the Manager and the Central Manager establish a connection, the Central Manager sends a request to the Manager for alert details. The Manager retrieves the existing alert details and sends the information to the Central Manager.
When the Manager receives new alerts the next time or if an existing alert is updated, it retrieves the alert details from the repository and sends the information to the Central Manager. Once it receives the alert details from the Manager, the Central Manager stores alert details in its database and displays those details along with the Manager name in the Attack Log.
When a Manager is removed from the Central Manager, all the alerts synchronized from that Manager are also removed from the Central Manager repository.
Note
To view Endpoint information, go to Analysis → <Admin Domain Name> → Quarantine in the corresponding Manager.
For more information on Attack Log, refer to the Attack Log section this guide.