Load balancing among the Virtual IPS Sensors provides the capability to handle higher network throughput. This is achieved due to the Virtual IPS Sensors' scale out and scale in capability in auto scaling groups. As the traffic in the network increases, the Virtual IPS Sensors are launched through the auto scaling feature in AWS. In case of excessive traffic flows, a single Virtual IPS Sensor may be overloaded due to which the traffic may not inspected. In such a scenario, auto scaling of Virtual IPS Sensors is capable of handling excessive flows by launching new instances of the Sensor. This way the traffic load is evenly distributed among the Virtual IPS Sensors.
vIPS Probes are able to load balance traffic to all of the Virtual IPS Sensors in the Cluster. The distribution is done on a flow by flow basis. Probes are able to send traffic to a newly launched Sensor as well as redirect traffic from a Sensor that is removed due to a scale-in event.
Note
TCP Flow Violation feature must be set to Permit out-of-order for Clusters that are enabled for auto scaling.
You can configure the limit to launch a new Virtual IPS Sensor in auto scaling groups. When the traffic load in the network reaches the configured limit, a new Virtual IPS Sensor instance is launched and a part of the traffic is redirected to the new Sensor instance. The auto scaling group launches new instances of the Virtual IPS Sensor based on the alarm configured for “CPU Utilization” and “Network In” parameters through AWS cloudwatch. The AWS cloudwatch maintains the alarms and monitors the traffic throughput. When the traffic exceeds the configured limit, it notifies the auto scaling group to launch a new instance of the Virtual IPS Sensor.
The Virtual IPS Sensors are either in active state or inactive state which depends on whether the Probe in each instance is able to forward traffic to a Sensor. The list of active and inactive Sensors are maintained by the Probes to forward traffic.
The Cluster uses the AWS auto scaling group to provide a method to increase the bandwidth of traffic to be inspected. Auto scaling groups use the scale out and scale in concept for launching the Virtual IPS Sensor. Instead of using a single Sensor to handle traffic, multiple Sensors with the same configurations are used. This provides failover for Sensors — even if one Sensor becomes inactive or is terminated, the traffic load is distributed between the other active Sensors in the cluster.
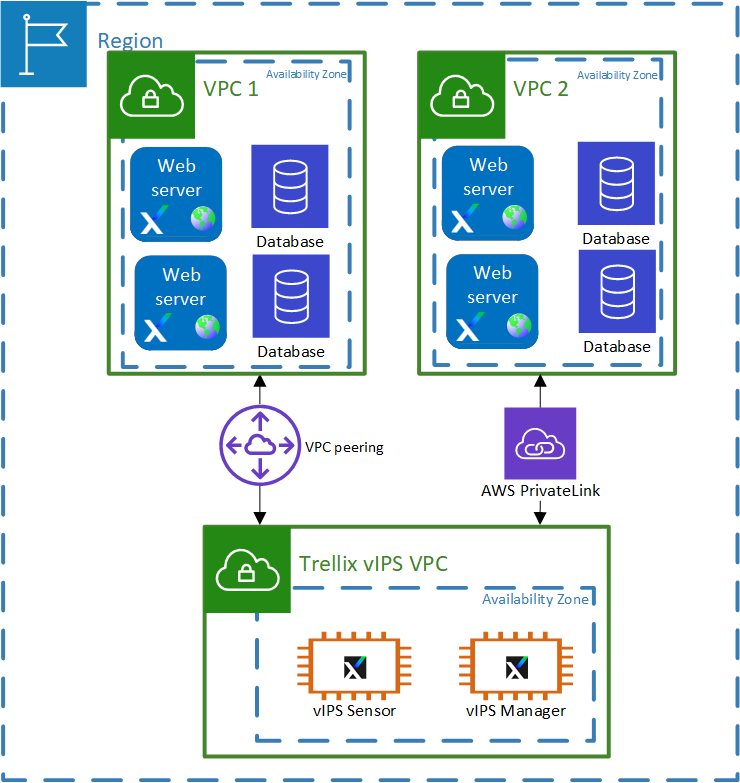
While designing your network for auto scaling, it is recommended to have a VPC dedicated for vIPS cloud solution which includes the Virtual IPS Sensor, Controller, and the Manager. VPC peering makes sure that the traffic from the VPC to be protected is directed to the security VPC.
It is also recommended to have separate Clusters for each Availability Zone. This provides Availability Zone level redundancy as well as avoids the cost of forwarding traffic from one zone to another for inspection.
Following are some scenarios under which the Virtual IPS Sensors are auto-scaled:
You can configure to launch new Virtual IPS Sensors when the traffic exceeds the CPU utilization of Sensors, or bandwidth to the Sensors exceed the threshold in AWS. You can also launch new Sensors based on custom monitoring configured for instances.
A Virtual IPS Sensor instance is terminated when the condition used to launch an instance no longer exists.
To maintain the minimum number of Sensors configured in auto scale, a new Virtual IPS Sensor instance is launched when a Sensor instance is terminated.
New Virtual IPS Sensor instances are not launched when a Sensor reboots or is down due to network failure. The Sensor is moved to the inactive list till the time it is active again.