The next step is to allocate one or more of those VLANs to a sub-interface to further refine the scanning process.
In the figure, we are adding a sub-interface called "WindowsServers", assigning it the Default Prevention policy, and allocating VLANs 2 and 5 to it:
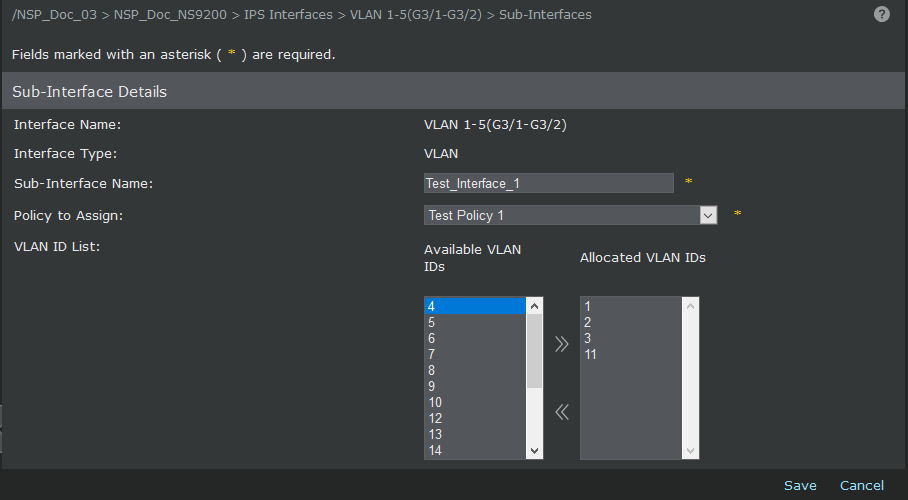
We highly recommend you give the sub-interface a name that indicates its contents. The name could have been as obvious as VLANS_1_2. It is more common, however, to name the sub-interface after the user community or hosts it protects, for example, Accounting_VLANs or, as is the case here, WindowsServers.
When we now look back at the details of the interface, a few things have changed:
The IPS interfaces now includes an icon representing the new sub-interface.
The details of the final configuration are as follows:
Traffic with a VLAN tag ID of 2 and 5 will have the Default Prevention policy applied to it.
Traffic with a VLAN tag ID of 1,3,and 4 will have the Default Detection policy applied to it.
We could of course create another sub-interface for Linux servers and allocate VLAN 7-9 to it, for example. At that point, all VLANs defined on the VLAN 7-9 interface would be allocated to sub-interfaces.
If we subsequently wanted to allocate yet another VLAN to a sub-interface, we would first have to de-allocate an existing VLAN ID from an existing sub-interface or add another VLAN ID to the G3/3-G3/4 interface.