Use this file to discover all available pages before exploring further.
The new docs.trellix.com features a modernized UI and AI-powered conversational search. Content is currently available in English, with additional languages launching in early November 2026. We hope you enjoy the updated experience.
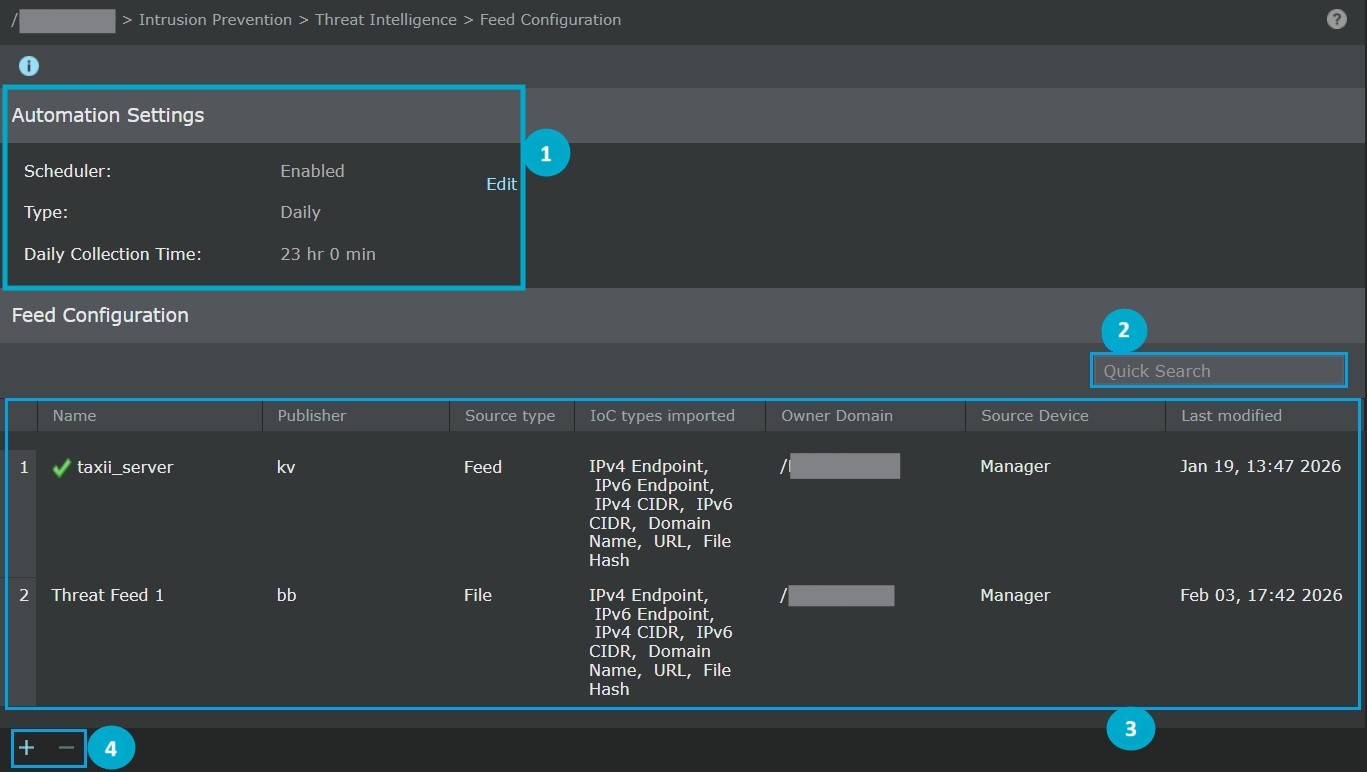
On the Policy → <Admin Domain Name> → Threat Intelligence → Feed Configuration page:
Create a threat feed: Create a new feed configuration on the Configure Feed tab:
Create a threat feed using file import: Upload the STIX-formatted JSON file containing the IoCs and import the IoC types based on your network requirements.
Create an automated threat feed using TAXII server: Configure the TAXII server and schedule the collection of threat feeds to automatically fetch STIX-formatted IoCs based on your network requirements.
Customize the IoC values: Once the threat feed is saved, you can view and exclude one or more imported IoC values for each IoC type from the IoC Values tab. The excluded values appear on the Exclusions tab and are not used for threat detection by the Sensors.
Assign the feed to Sensors: After the configuration of the threat feed, you must assign it to one or more Sensors from the Device Assignments tab. A single threat feed can be assigned to multiple Sensors.
Go to the Feed Assignments Summary page if you want to view the assignment of Sensors to different threat intelligence feeds.
Completing the task of threat feed configuration and alert logging differs by the imported IoC types that you want to use for threat detection:
IPv4/IPv6 endpoints and CIDRs: Configure a syslog server using the Firewall Access Logging Page in the Manager to log the alert messages.
Domains, URLs: Add or update an inspection policy and do the following -
Enable Layer 7 Data Collection in the required direction on the Traffic Inspection tab.
Enable URL Reputation Analysis from the GTI Reputation Services tab, and assign the policy to the required Sensor(s).
File Hash: Create an advanced malware policy, select the required file types for Threat feed / Local Block List malware engine, and assign the policy to the required Sensor(s).