Prerequisites:
Before you begin to construct the Snort rules, review the following:
In the rule, you can use only the variables, classtypes, and references that are available in the Manager. For information on how to view the available values, see Viewing the variables and classification types.
You can write only one rule at a time.
You can construct Snort rules directly in the Manager using the Custom Attack Editor. Note that these rules must conform to the Snort rules language syntax. Structure of a Snort rule provides information how to construct Snort rules within Trellix IPS.
To construct Snort rules in the Manager, perform the following steps:
Select Policy → <Admin Domain Name> → Intrusion Prevention → Policy Types → IPS. Click Custom Attacks.
The Custom Attack Editor opens with the existing Custom Attacks listed on the Native Trellix IPS Format tab.
Click Snort Format tab.
Click
 .
The New Snort Rule interface opens.
New Snort Rule window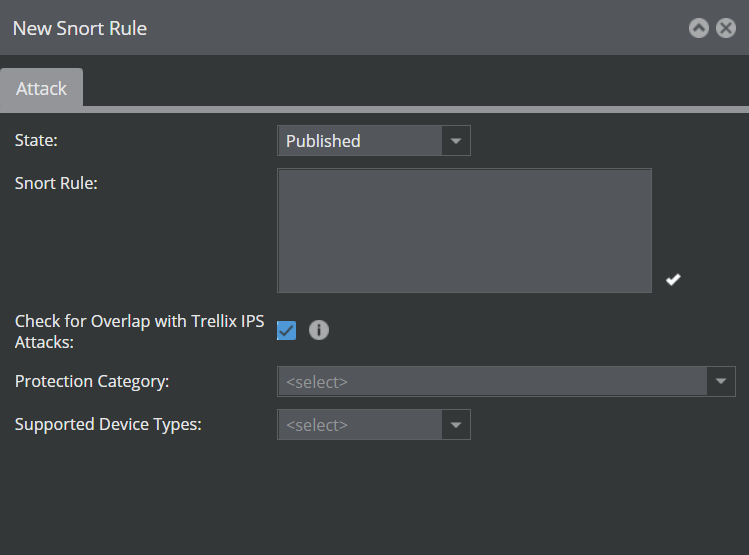
Construct the Snort rule in the Add Snort Rule dialog.
Note the following:
You cannot define variables in the Add Snort Rule dialog, but you can use the variables that are available in the database.
You can write only one rule at a time.
If you are using the keywords such as classtype or reference, make sure the corresponding values are already defined and available in the database. For example, to import classifications, you can import a file that calls the classification config file and then use these classifications in the rules that you construct.
Select Check for Overlap with Trellix IPS Attacks to verify if the rule matches an existing Trellix IPS attack definition. If the rule matches then the Snort Rule will be Staged.
Select the most appropriate Protection Category for the attack.
Click Add.
The rule is listed in the All Custom Attacks tab.
Save the rule to the database so that it gets published in the relevant policies.